
HIPAA requires documented safeguards
Healthcare organizations need appropriate administrative, physical and technical safeguards for electronic protected health information and a documented risk analysis.
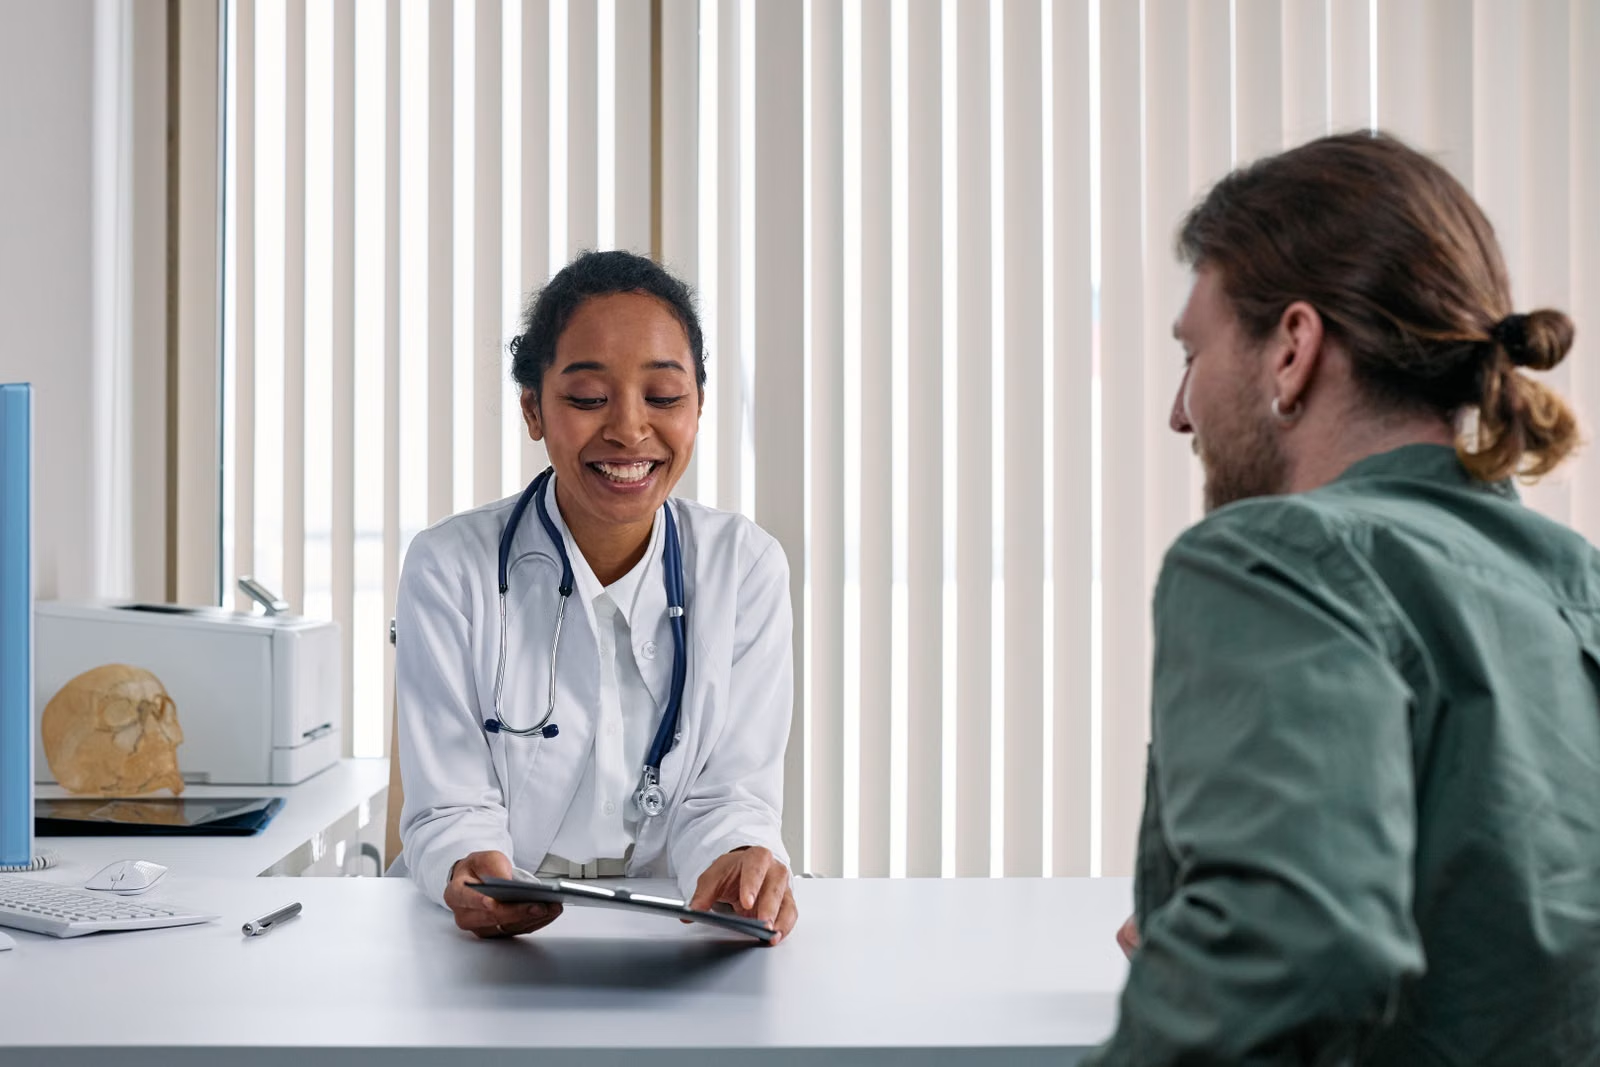
CMIT Solutions of Cincinnati East helps medical, dental, behavioral health and specialty practices keep systems reliable, protect patient information and support the technology that keeps care moving.
Managed IT for a healthcare practice can include 24/7 monitoring and help desk support, EHR and practice management support, HIPAA-focused access controls and security practices, risk assessments, encrypted backups, secure email, network management, cybersecurity and business continuity planning.
Healthcare organizations have to balance patient care, system uptime, privacy and security at the same time. A technology problem can quickly become an operational or patient-care problem.
Healthcare organizations need appropriate administrative, physical and technical safeguards for electronic protected health information and a documented risk analysis.
Cyber incidents can interrupt access to systems and records, creating immediate pressure on staff, schedules and patient workflows.
When EHR, scheduling, billing or connectivity fails, staff productivity and patient flow can slow down quickly.
EHR vendors, billing partners, laboratories and other service providers may require access controls, contracts and security oversight.
Before we recommend a single tool, we learn how your practice operates, which systems your staff depend on and what a disruption could mean for your patients, employees and business.
"Clients don't need us to sound smart. They need us to understand their business and help." Hal Theobald, Managing Partner


Our approach starts with how your healthcare organization works, so IT decisions support patient care, staff productivity, security and growth.

Access enterprise-grade technology partners and products through the CMIT Solutions network, backed by local Cincinnati East support.

High-quality managed service designed for organizations with 1 to 200 users and the technology risks they carry.
One local team for support, security, compliance and planning across your healthcare technology environment.
Proactive monitoring and maintenance for workstations, servers, networks and other critical healthcare technology.
Keep your EHR, scheduling, billing and connected applications available to the people who rely on them.
Layered protection for patient information, accounts, endpoints and connected systems.
Risk review, security controls and supporting documentation for your healthcare compliance program.
Critical business and patient-related data protected against failure, deletion, ransomware and other disruptions.
Reliable connectivity with network controls designed to separate appropriate access across staff, guests and critical systems.
Every managed IT plan includes these protections, so the basics are covered.
 EDREndpoint detection and response on every device
 Email securityFiltering for phishing, malware and impersonation
 DNS filteringBlocks malicious and unwanted websites
 Access managementControlled accounts, permissions and directories
 Backup validationBackups checked so restores actually work
 Disaster recovery planA written plan to get you running again
Your organization remains responsible for compliance. We provide technical safeguards, documentation and evidence behind your security program and help align controls to applicable healthcare, customer, contract and insurance requirements.
| Standard | What it asks of you | What we put in place |
|---|---|---|
| HIPAA Security Rule | Administrative, physical and technical safeguards for electronic protected health information, including a documented risk analysis. | Risk assessment support, access controls, encryption, logging, security planning and technical safeguards. |
| HITECH breach notification | Requirements related to certain breaches of unsecured protected health information. | Security controls, incident-response planning, logging and recovery support. |
| 42 CFR Part 2 | Additional confidentiality protections for substance use disorder treatment records where applicable. | Access restrictions, security planning and appropriate system controls. |
| Ohio breach notification | Ohio law establishes notification obligations for certain breaches involving computerized personal information. | Encryption, logging, incident-response planning and recovery controls that support your response process. |
Which requirements apply depends on your organization, data, contracts and business model. CMIT provides technical and documentation support; it does not provide legal advice or certify an organization for HIPAA compliance.
 Secure AI
Healthcare teams are exploring AI for documentation, communication, research and workflow support. A managed approach can add governance, access controls and human review so adoption does not create an unnecessary path for sensitive information to leave the organization.
Healthcare case studies from the CMIT Solutions network show how proactive IT support, security and planning can help keep patient-focused organizations running.
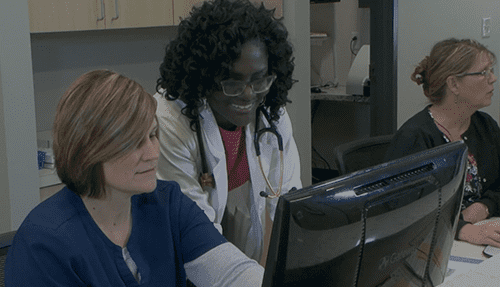
A multi-location optical retailer with in-house doctors and an EMR environment used proactive IT support and infrastructure planning to simplify growth and compliance.

Matthews Internal Medicine moved from repeated IT service problems to a more reliable technology partnership that helped the practice focus on patient care.

A medical society turned to CMIT Solutions for technology planning and around-the-clock support so its team could spend less time worrying about IT problems.
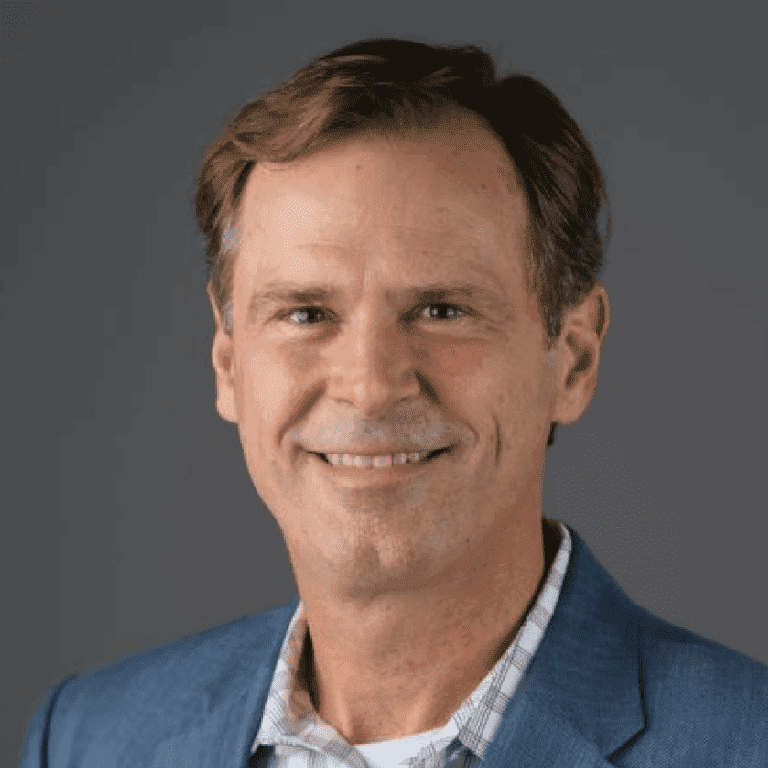
Hal Theobald leads CMIT Solutions of Cincinnati East with a business-first approach focused on downtime risk, operational resilience and practical technology decisions.
CMIT Solutions of Cincinnati East has received four consecutive years of recognition in the Computer Networking Company category from Ohio Business Magazine.
CMIT Solutions has consistently ranked on Entrepreneur Magazine's Franchise 500 list for more than a decade.
ConnectWise has recognized CMIT Solutions with its Partner of the Year award, described by CMIT as its highest partner honor.
Technology changes are planned around patient-care schedules, operational priorities and business needs to reduce unnecessary disruption.
We learn how your organization operates and identify important technology and security exposures.
You receive a written, prioritized roadmap connecting technology work to operational needs.
Changes are coordinated and communicated around your business and patient-care requirements.
Monitoring, help desk support, security, maintenance and ongoing technology planning continue after launch.
Straight answers to what Cincinnati-area healthcare organizations ask before choosing a managed IT partner.
Talk to the Cincinnati East team about your systems, technology risks, compliance needs and priorities.
Ask our team or call (513) 815-5500Yes. When our work involves systems containing protected health information, we can establish the appropriate business associate agreement before services begin and help you keep track of vendors that need one.
Yes. We can inventory systems that handle ePHI, assess threats and vulnerabilities, rate the risks, and provide a written remediation plan. The assessment can be repeated as part of an ongoing compliance program and after significant changes.
Yes. We support the workstations, network, scanners, connectivity and integrations your EHR depends on, and coordinate with your EHR vendor when an issue belongs to the application itself.
Yes. Cincinnati East supports healthcare organizations including medical, dental, behavioral health, specialty and other patient-care practices. Organizations subject to additional privacy requirements may need more specific access controls and documentation.
Managed IT is typically provided at a predictable monthly rate based on the users, devices, services and environment agreed after an assessment. The plan and pricing are documented before work begins.
We learn how your business runs, review your network, devices, backups, Microsoft 365 setup and security controls, identify important gaps, and translate the findings into a plain-language, prioritized plan. There is no cost and no obligation.
Yes. We can help identify, implement and document common controls insurers may ask about, including multi-factor authentication, endpoint protection, backups, security awareness training and incident-response planning. Requirements vary by carrier and policy.
Yes. Cincinnati East provides 24/7 monitoring and support options, with remote assistance and on-site service when an issue needs hands-on attention.
CMIT Solutions of Cincinnati East serves businesses throughout Greater Cincinnati, including Cincinnati, Anderson Township, Milford, Miami Township, Norwood, Blue Ash, Mason, West Chester, Loveland, Batavia and surrounding communities.
Find out where your healthcare technology environment is exposed and what it would take to strengthen reliability, security and recovery readiness.
Prefer to talk?(513) 815-5500
Visit us6809 Main Street, Unit 350, Cincinnati, OH 45244
Short on time?Take the quick Cincinnati East IT self-assessment