
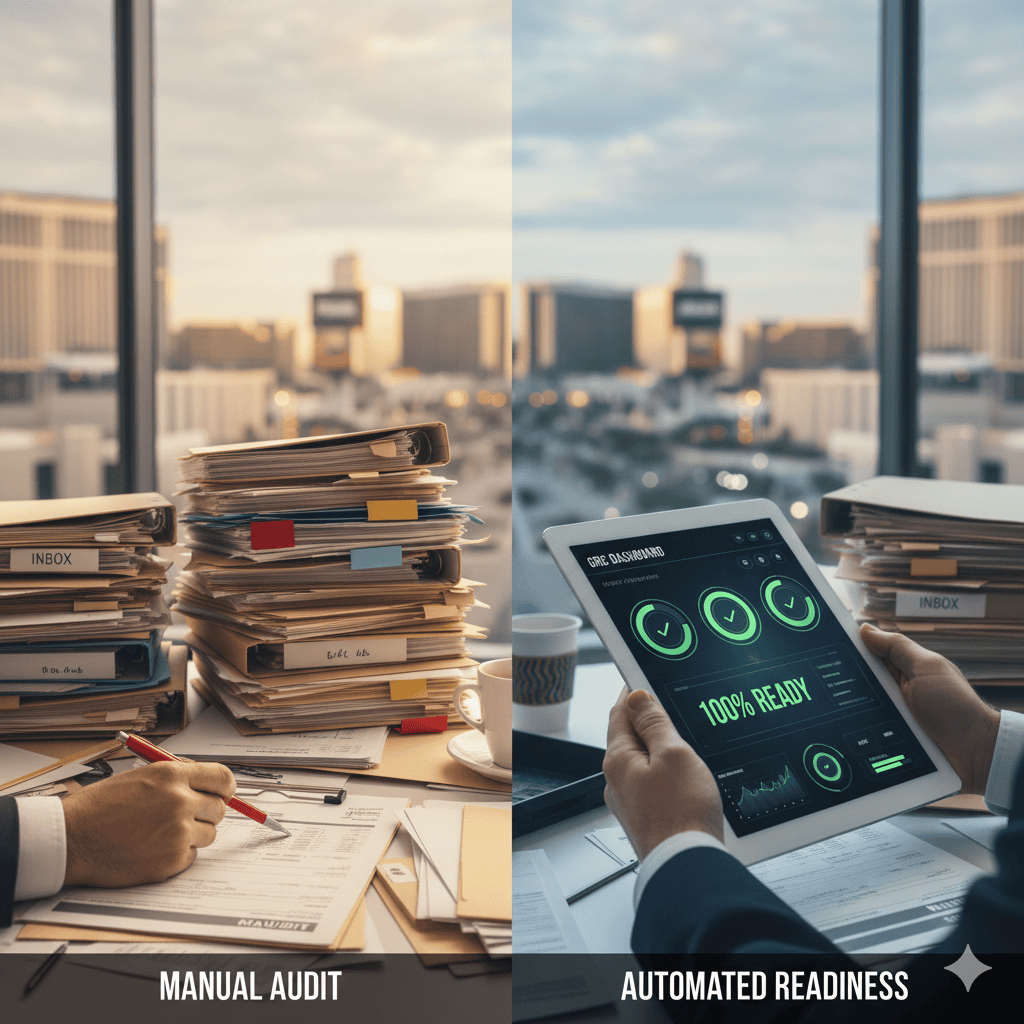
Stop Burning Money: Why You Shouldn’t Call a CPA for Your SOC 2 Audit (Yet)
If you are a business in Las Vegas—whether you are a SaaS company in Summerlin or a defense contractor in North Las Vegas—you have likely heard the demand from your clients: “Send us your SOC 2 Report,” or “Are you CMMC ready?”
Your first instinct is probably to call a CPA firm to schedule an audit. That is a $20,000 mistake.
Here is the dirty little secret of the compliance industry: If you bring a CPA in before you are ready, they will charge you their premium hourly rates just to tell you your policies are missing. They are auditors, not fixers.
At CMIT Solutions of Las Vegas, we help local companies navigate the “Pre-Audit” phase. Our goal is simple: get you 100% ready before the clock starts ticking, so you pay the auditor for a “Sign-off,” not a “Clean-up.”
The “Ticking Clock”: November 10, 2025 (CMMC 2.0)
For our local Department of Defense (DoD) contractors, the timeline is no longer theoretical. The CMMC Final Rule enforcement phase is scheduled to begin on November 10, 2025.
If you are not compliant by then, you will be ineligible for new contracts. Since the average readiness process takes 12-18 months, if you haven’t started your Gap Analysis yet, you are already behind schedule.
The 3-Step “Readiness” Strategy to Save 50% on Audit Fees
Step 1: The Readiness Assessment (Gap Analysis)
Before anyone looks at your books, we conduct a technical “Gap Analysis.” We look at your current IT environment against the framework you need (SOC 2, ISO 27001, CMMC, or NIST).
We identify exactly where you fail: Do you have Multi-Factor Authentication on all admin accounts? Do you have an offboarding checklist for fired employees? We find the holes so we can patch them proactively.
Step 2: Implementing a GRC Tool (The Death of Spreadsheets)
In the old days, audits meant hundreds of Excel spreadsheets and screenshots. In 2025, that is obsolete.
We implement a Governance, Risk, and Compliance (GRC) tool (like Drata or Vanta) for you. This software connects directly to your cloud, HR system, and device manager. It automates evidence collection 24/7.
- Old Way: You manually take a screenshot of your firewall settings every Monday.
- New Way: The GRC tool monitors the firewall and logs a “Pass” automatically every hour.
Step 3: The “Remediation” Phase
Once the GRC tool flags the errors, CMIT Solutions fixes them. We write the policies, we configure the encryption, and we secure the endpoints. We turn all those “Red X’s” into “Green Checkmarks.”
The Final Handoff: Choosing the Right CPA
Only once your GRC dashboard is green do we invite the CPA in for the Attestation. Because all your evidence is organized and automated, the auditor spends less time hunting for data.
Less time for the CPA = Lower fees for you.
Get Your Free Audit RFP Template
Don’t negotiate with a CPA empty-handed. We have developed a comprehensive RFP Template specifically for Las Vegas businesses seeking SOC 2 or CMMC attestation.
It includes the tough technical questions you need to ask to ensure you aren’t overcharged. Contact us today, and we will send it to you for free.
Call (702) 725-2877 to Get Your Free RFP
More Resources for Las Vegas Business Security
- 🚨 The Scams: Protect your compliance status by stopping 3 Phishing Scams Targeting Las Vegas Businesses.
- 🤖 The Risk: Don’t let AI ruin your audit. Read about Shadow AI Risks in Nevada.