
Cybersecurity Compliance & Risk Management Services
Practical compliance support for NIST, CMMC, HIPAA, FTC Safeguards, SOC 2, WISP requirements, cyber insurance, and organizational resilience.
Compliance is not simply about satisfying regulations.
Strong compliance programs help organizations reduce risk, improve resilience, strengthen security practices, and build trust with customers, vendors, insurers, and stakeholders.
CMIT Solutions of Northwest Metro Detroit helps organizations develop practical compliance and resilience programs that support business objectives while improving security, governance, and operational readiness.
[Schedule a Compliance & Resilience Assessment]
[Talk With a Compliance Advisor]
Explore Options

Frameworks We Support
NIST Cybersecurity Framework (CSF)
Risk assessment, cybersecurity maturity, governance and security-program improvement.
NIST SP 800-171
Assessment and remediation planning for organizations that need to protect CUI.
CMMC
Readiness, gap assessments, remediation roadmaps, documentation and ongoing cybersecurity support for defense contractors and suppliers.
HIPAA Security Rule
Security risk assessments, safeguards, policies, incident readiness and ongoing security management.
FTC Safeguards Rule
Risk assessments, security controls, vendor oversight, policies and documentation.
SOC 2 Readiness
Control mapping, gap identification, evidence readiness, remediation and ongoing technology/security support.
NIST & CMMC Readiness
Build a Practical Path Toward Cybersecurity Compliance
Organizations working with government agencies, defense contractors, manufacturers, and regulated supply chains may face cybersecurity requirements based on NIST standards or CMMC.
Areas We Help Address
NIST CSF alignment
NIST SP 800-171 assessments
CMMC readiness
Gap assessments
Remediation roadmaps
Security policies and procedures
Evidence and documentation readiness
Technology/security control implementation
Ongoing compliance management
HIPAA Security Support
Improve Security and Risk Management
Healthcare organizations must protect sensitive information while maintaining operational effectiveness.
Areas We Help Address
- Security Risk Assessments
- Security Program Reviews
- Policies & Procedures
- Workforce Awareness
- Incident Response Planning
- Vendor Reviews
- Documentation Support
Outcomes
- Improved readiness
- Better governance
- Reduced risk
- Stronger security programs
FTC Safeguards Rule Support
Protect Customer Information
Organizations handling sensitive financial information may face obligations under the FTC Safeguards Rule.
Areas We Help Address
- Risk Assessments
- Security Controls
- Policy Development
- Vendor Oversight
- Security Awareness
- Incident Response Planning
- Program Documentation
Outcomes
- Improved readiness
- Better documentation
- Reduced risk exposure
- Greater confidence
Why Compliance & Resilience Matter
Organizations face increasing expectations from:
- Customers
- Insurance carriers
- Regulators
- Business partners
- Vendors
- Industry standards
At the same time, cyber threats, operational disruptions, and business continuity concerns continue to increase.
Compliance and resilience programs help organizations establish the policies, processes, and controls necessary to manage risk and support long-term success.
Written Information Security Programs (WISP)
Establish a Structured Security Program
Many organizations must document how they protect sensitive information.
Areas We Help Address
- WISP Development
- Policy Reviews
- Security Controls
- Risk Assessments
- Employee Responsibilities
- Vendor Oversight
- Incident Response Planning
- Program Maintenance
Outcomes
- Better documentation
- Improved governance
- Reduced compliance risk
- Stronger security programs
SOC 2 Readiness
Build the Controls and Evidence Needed for SOC 2
Organizations pursuing SOC 2 need more than policies—they need security and technology controls that are implemented, documented, and operating effectively.
Areas We Help Address
- SOC 2 readiness and gap assessments
- Trust Services Criteria control mapping
- Security policies and procedures
- Identity and access management
- Vulnerability management and security monitoring
- Incident response and business continuity
- Vendor and third-party risk
- Evidence and documentation readiness
- Technology control implementation
- Ongoing compliance management
CMIT Solutions helps prepare your technology and cybersecurity environment for SOC 2 and can work alongside your independent auditor or compliance partners. We do not perform SOC 2 examinations or issue SOC 2 reports.
Compliance Beyond Checklists
Compliance should support business objectives—not create unnecessary complexity.
Effective compliance programs help organizations:
- Reduce risk
- Improve security
- Strengthen governance
- Improve documentation
- Support business continuity
- Demonstrate due diligence
- Build stakeholder confidence
Risk Assessments
Understand Your Current Risk Exposure
Risk assessments provide the foundation for effective compliance and resilience programs.
Areas We Evaluate
- Cybersecurity Risks
- Operational Risks
- Technology Risks
- Vendor Risks
- Compliance Gaps
- Business Continuity Risks
- Documentation Gaps
- Governance Practices
Outcomes
- Improved visibility
- Prioritized recommendations
- Better decision-making
- Reduced uncertainty
Cyber Insurance Readiness
Align Security Practices with Insurance Expectations
Insurance carriers increasingly evaluate security practices before issuing or renewing coverage.
Areas We Help Address
- Security Controls
- MFA Readiness
- Endpoint Security
- Security Awareness
- Backup Validation
- Incident Response Planning
- Documentation Reviews
Outcomes
- Improved insurance readiness
- Better visibility
- Reduced underwriting concerns
- Stronger security posture
Business Continuity & Resilience
Prepare for Operational Disruptions
Compliance and resilience are closely connected.
Areas We Help Address
- Business Continuity Planning
- Disaster Recovery Planning
- Incident Response Planning
- Tabletop Exercises
- Recovery Testing
- Operational Resilience Reviews
Outcomes
- Faster recovery
- Reduced downtime
- Improved preparedness
- Greater resilience
Governance & Policy Development
Establish Clear Expectations and Accountability
Strong governance helps organizations make better decisions and manage risk consistently.
Areas We Help Address
- Security Policies
- Governance Frameworks
- Vendor Governance
- Technology Governance
- Executive Reporting
- Risk Oversight
Outcomes
- Improved accountability
- Better decision-making
- Stronger governance
- Increased visibility
Who Benefits Most?
Organizations that:
- Handle sensitive information
- Have compliance obligations
- Need cyber insurance
- Work with regulated data
- Face client security requirements
- Want stronger governance
- Need improved resilience planning
Common Industries We Support
- CPA & Accounting Firms
- Healthcare Organizations
- Manufacturing Companies
- Construction Firms
- Financial Services Organizations
- Law Firms
- Nonprofits
- Professional Services Firms
How Compliance & Resilience Fit Into Our Framework
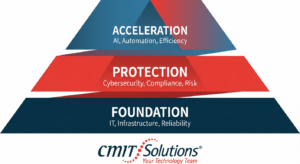
Compliance and resilience are core elements of the Protection layer.
Foundation
Reliable technology operations.
Protection
Cybersecurity, compliance, governance, and resilience.
Acceleration
Technology strategy, AI governance, automation, and innovation.
Organizations achieve stronger outcomes when compliance programs support broader business and technology objectives.
[Learn More About Our Framework]
Why CMIT Solutions of Northwest Metro Detroit?
Compliance should support operational effectiveness and risk management—not become a burden.
We help organizations build practical programs that improve security, strengthen governance, support resilience, and align with business objectives.
We focus on helping leadership answer:
- What requirements apply to us?
- Where are our biggest gaps?
- What should we address first?
- How prepared are we?
- How do we improve over time?
Need Ongoing Compliance & Security Leadership?
Compliance isn’t always a one-time project. Organizations with ongoing regulatory, customer, insurance or governance requirements may benefit from Fractional CISO support.
Frequently Asked Questions
What cybersecurity compliance requirements apply to my business?
Requirements depend on your industry, customers, contracts, the type of data you handle, and other regulatory obligations. We help organizations assess their environment, identify applicable cybersecurity requirements, and develop a practical roadmap for addressing gaps.
Can you help with NIST cybersecurity compliance?
Yes. We help organizations assess and improve their alignment with NIST frameworks and standards, including the NIST Cybersecurity Framework (CSF) and NIST SP 800-171. Support can include assessments, gap analysis, remediation planning, security controls, policies, documentation, and ongoing cybersecurity management.
Can you help our organization prepare for CMMC?
Yes. We can support CMMC readiness through gap assessments, NIST SP 800-171 alignment, remediation planning, security control implementation, policies, documentation, evidence readiness, and ongoing cybersecurity support. Formal CMMC assessments and certifications are performed by authorized third parties when required.
Do you provide HIPAA cybersecurity and compliance support?
Yes. We help healthcare organizations and other businesses handling protected health information evaluate cybersecurity risks, strengthen administrative and technical safeguards, improve policies and procedures, and address technology-related HIPAA Security Rule requirements.
Can you help us prepare for SOC 2?
Yes. We support SOC 2 readiness through gap assessments, control mapping, security improvements, policies and procedures, evidence preparation, and ongoing technology and cybersecurity management. CMIT Solutions does not perform SOC 2 examinations or issue SOC 2 reports; those services are provided by independent CPA firms.
Can you help with FTC Safeguards Rule requirements?
Yes. We help applicable organizations evaluate their cybersecurity environment and address technology-related safeguards, including risk assessments, access controls, encryption, multi-factor authentication, monitoring, incident response, vendor risk, and documentation.
Can you help with cyber insurance requirements?
Yes. We can assess your existing security controls against common cyber insurance requirements and help address gaps involving MFA, endpoint protection, backups, email security, privileged access, security monitoring, incident response, and other controls commonly requested by insurers.
Is compliance a one-time project?
Usually not. Cybersecurity frameworks, customer requirements, technology environments, threats, and business operations change over time. We can provide ongoing compliance and security management to help maintain controls, documentation, evidence, risk reviews, and remediation activities.
What happens during a Compliance & Risk Assessment?
We review your technology environment, cybersecurity controls, policies, documentation, business requirements, and relevant compliance obligations. The goal is to identify gaps, prioritize risks, and develop a practical roadmap for remediation and ongoing management.
Build a Stronger Compliance & Resilience Program
Compliance is not just about satisfying requirements.
It’s about reducing risk, improving preparedness, strengthening governance, and protecting organizational success.
Whether you’re developing a WISP, preparing for insurance requirements, improving resilience, or strengthening governance, CMIT Solutions can help.