IT Compliance Services for Atlanta Businesses

Meet Compliance Requirements and Protect Your Business

Every industry faces different requirements for protecting sensitive information. CMIT Solutions helps Atlanta businesses understand their obligations, address security gaps, and maintain practical compliance programs.

Identify Your Most Important Compliance Risks

Effective compliance begins with understanding which requirements apply to your organization and how well your current practices satisfy them.

CMIT Solutions evaluates your technology, security controls, policies, data handling procedures, and employee practices. We identify weaknesses, prioritize immediate needs, and develop a practical roadmap for improving compliance over time.

Assess Your Compliance Readiness

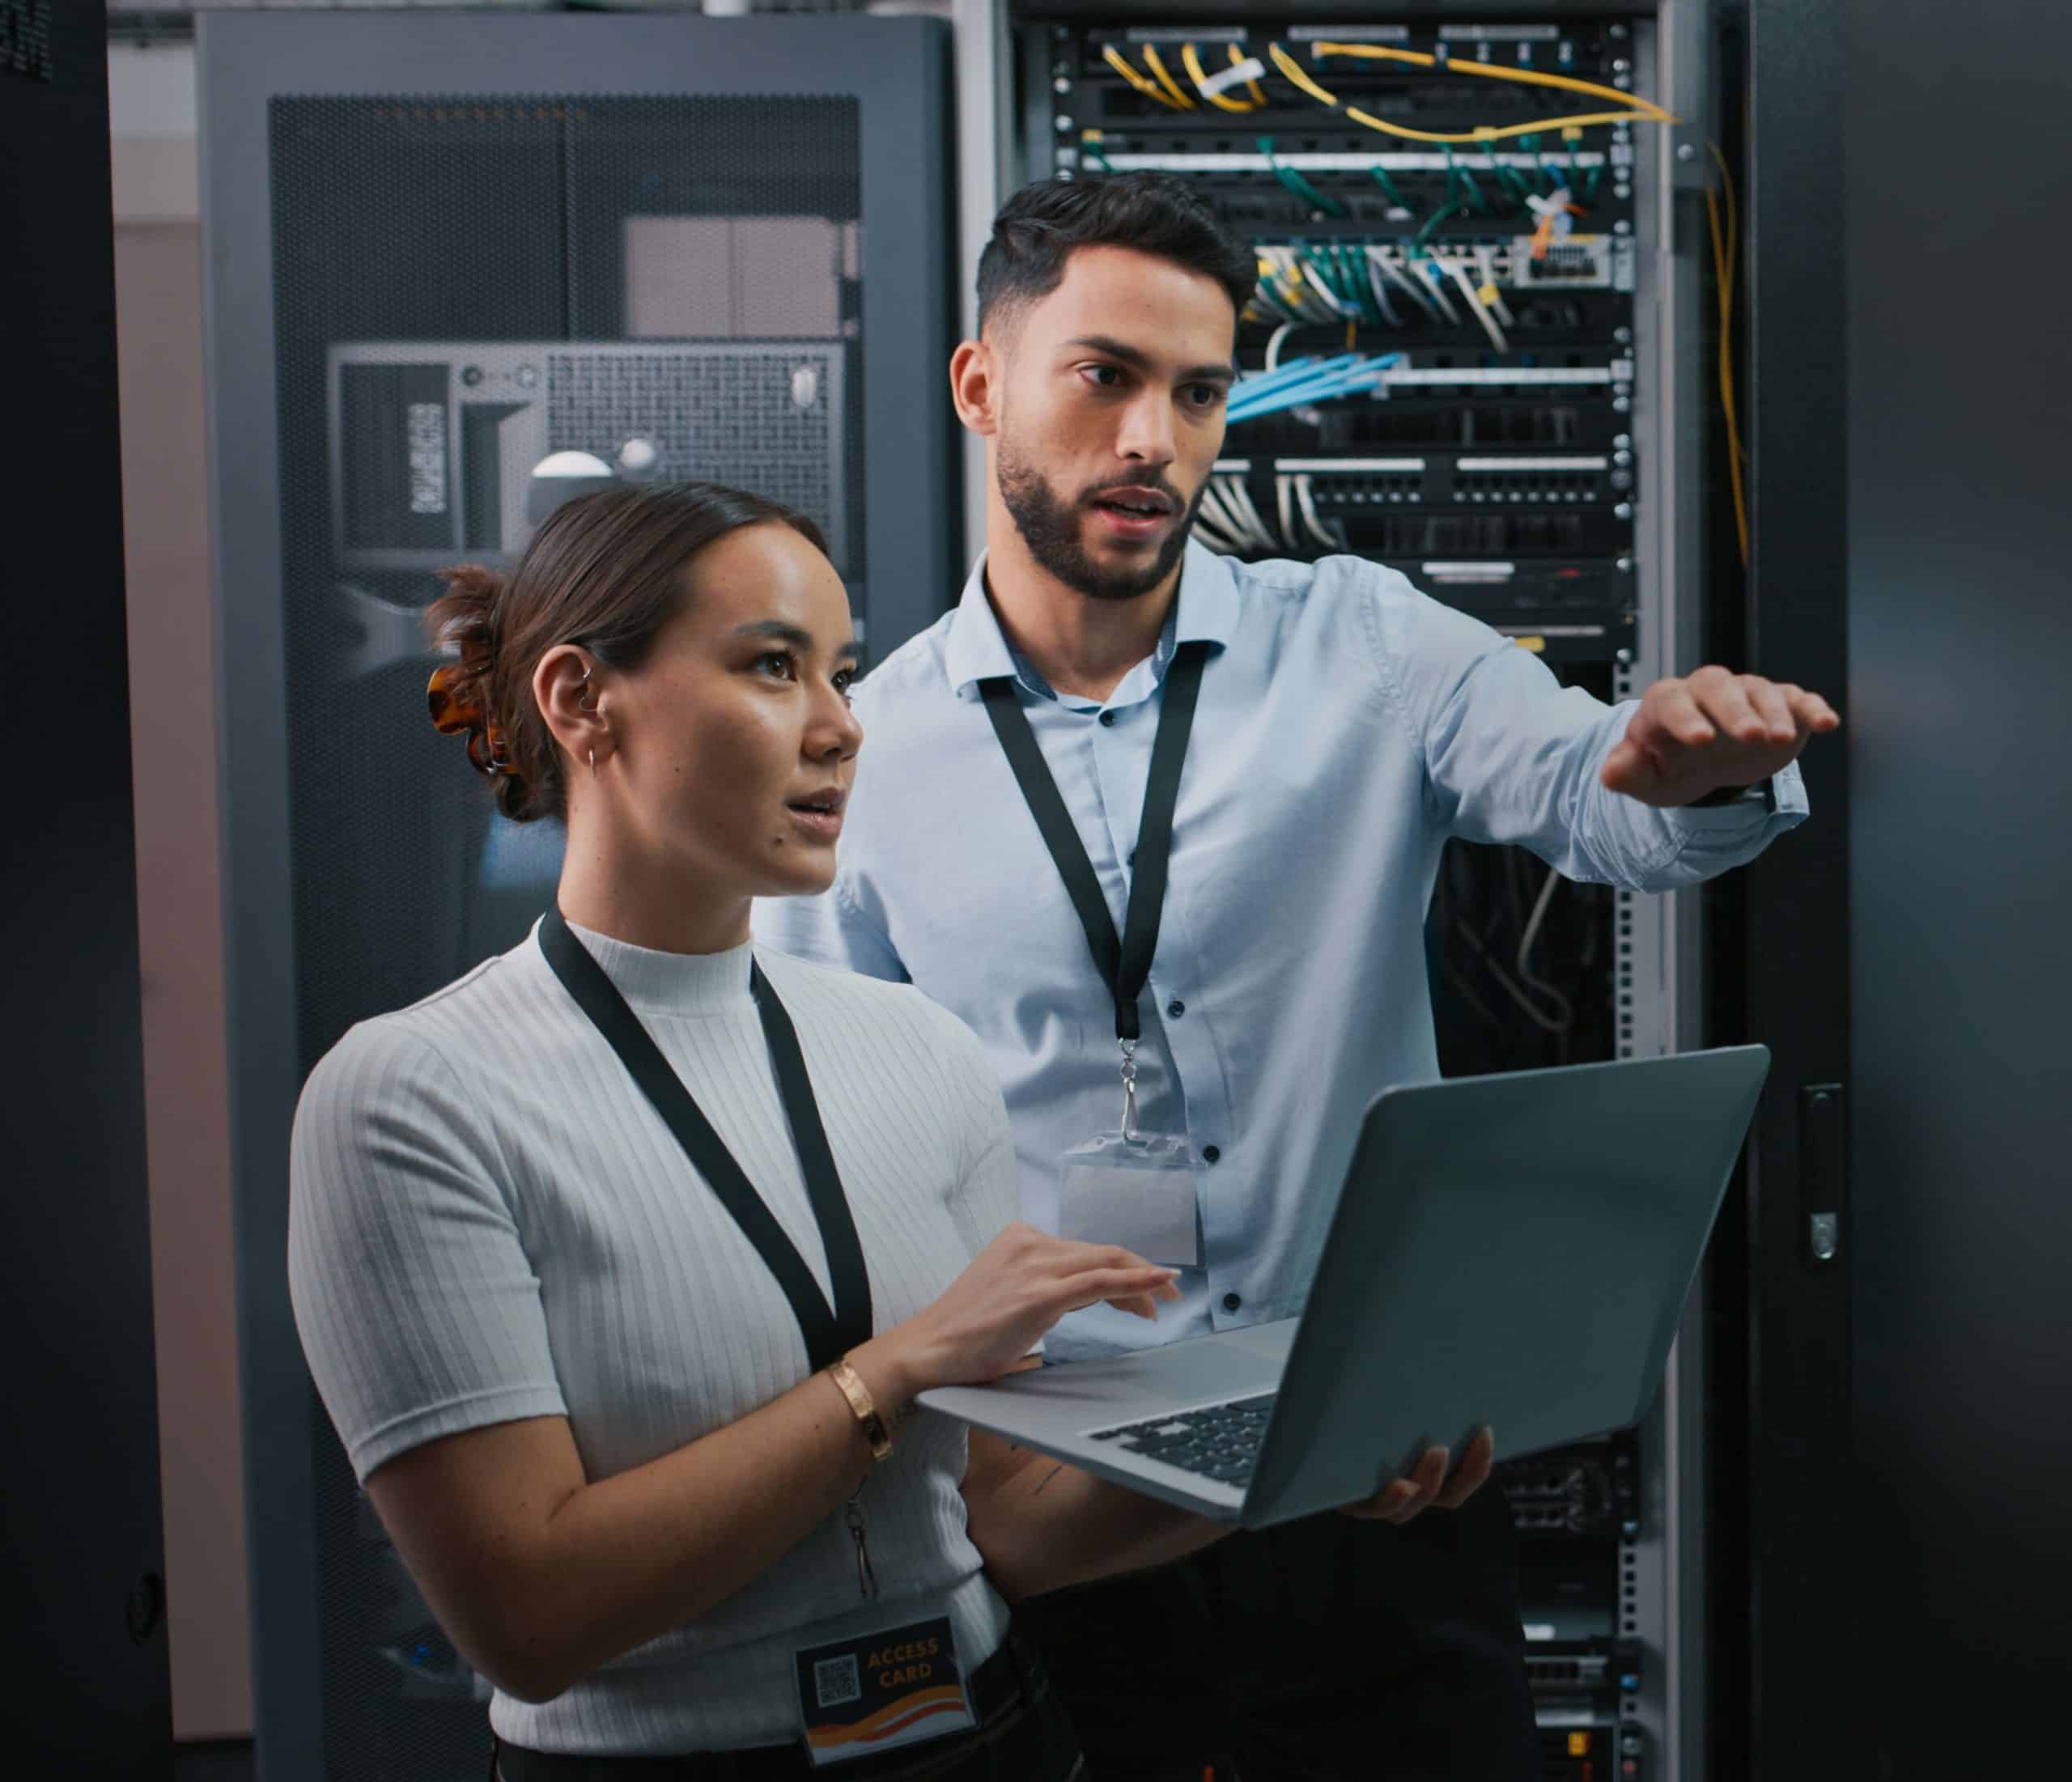
Two IT professionals in a data center review server equipment, with the man pointing at cables while the woman holds a laptop

Turn Compliance Requirements into Practical Safeguards

Frameworks such as HIPAA, CMMC, PCI DSS, NIST, FINRA, and GDPR can involve overlapping but distinct responsibilities. Applying those requirements to your specific systems and workflows requires more than a generic checklist.

We help translate applicable standards into technical and operational controls, including access management, encryption, monitoring, documentation, employee training, incident response, and vendor oversight.

Strengthen Your Compliance Program

Close-up of hands pressing keys on a white calculator beside printed documents on a desk.

Keep Compliance Current as Requirements Change

Compliance is not a one-time project. Regulations, contractual obligations, cybersecurity threats, technology environments, and business operations continue to evolve.

CMIT Solutions provides ongoing guidance, monitoring, documentation support, and periodic assessments to help your business adapt. This continuous approach makes compliance part of normal operations instead of an emergency before every audit.

Maintain Long-Term Compliance

Person typing on a laptop with a blue cybersecurity graphic and a white lock icon on screen
Team of colleagues gathered around a table collaborating on documents in a modern office conference room.

Compliance should strengthen your business, not overwhelm it.

Build a practical program that protects sensitive information, supports regulatory requirements, and prepares your organization for future assessments.

Request a Meeting

IT Compliance Services for Your Business

We help Atlanta businesses evaluate requirements, implement appropriate safeguards, and maintain the documentation needed to demonstrate compliance.

Triangle warning icon with an exclamation mark in the center

Compliance Risk Assessment

Evaluate your current technology, policies, security controls, data practices, and documentation against applicable requirements.

Blue caduceus medical symbol: a staff with twin snakes entwined and wings at the top.

HIPAA Compliance Support

Help covered entities and business associates protect electronic protected health information through appropriate administrative, physical, and technical safeguards.

Dark blue obelisk monument silhouette centered on a pale background with a rectangular base.

CMMC Compliance Support

Prepare defense contractors and subcontractors for applicable CMMC requirements through scoping, gap analysis, remediation, documentation, and assessment readiness support.

Circular camera shutter icon in dark teal on a light background; represents photography

NIST Framework Alignment

Organize cybersecurity practices around the NIST Cybersecurity Framework functions: Govern, Identify, Protect, Detect, Respond, and Recover.

Computer monitor with a gear icon, representing settings

FINRA Compliance Support

Help FINRA member firms strengthen cybersecurity governance, access management, incident response, vendor oversight, and protection of customer information.

Wallet icon with a shield, symbolizing secure paymentsy?

PCI DSS Compliance Support

Protect payment account data and support PCI DSS requirements for businesses that store, process, transmit, or could affect the security of cardholder data.

Logo of overlapping dark blue speech bubbles on a light background

GDPR Compliance Support

Help organizations evaluate technical and operational safeguards when offering goods or services to individuals in the EU or monitoring their behavior.

Server icon with a checkmark indicating verified status

ISO 27001 Readiness

Align information security policies, controls, risk management practices, and documentation with ISO 27001 requirements.

Document icon (blue file with a folded corner)

Policies and Documentation

Develop and maintain security policies, procedures, risk records, response plans, inventories, diagrams, and other compliance evidence.

Illustration of a person in front of a computer screen with a padlock, symbolizing secure login or authentication

Security Awareness Training

Teach employees how compliance requirements affect their responsibilities and incorporate secure behavior into everyday workflows.

Blue circular first aid icon

Penetration Testing

Use controlled security testing to identify exploitable vulnerabilities, support remediation, and provide evidence for applicable compliance programs.

Ongoing Monitoring

Review systems, security events, controls, and regulatory developments to identify emerging risks and maintain compliance readiness.

A Practical Approach to Business Compliance

Technology can do more for your business than ever before. But it’s also more complicated than ever to manage. Don’t pull your team away from operations to babysit your technology. Here’s what our Atlanta clients get from partnering with us:

Clear Assessments

Understand where your organization currently stands, which gaps require attention, and what evidence may be needed.

Clear Assessments

Understand where your organization currently stands, which gaps require attention, and what evidence may be needed.

Adaptable Protection

Update safeguards and documentation as regulations, contracts, technology, and business operations change.

Adaptable Protection

Update safeguards and documentation as regulations, contracts, technology, and business operations change.

Expert Guidance

Receive ongoing compliance direction without the expense of maintaining a full-time internal compliance or security specialist.

Stronger Customer Trust

Demonstrate that your organization takes data security, privacy, and responsible information handling seriously.

IT Compliance Services for Atlanta Southern Crescent Businesses

Businesses throughout Atlanta’s Southern Crescent may be responsible for protecting health information, payment data, government information, customer records, employee data, or other sensitive material. The requirements vary considerably, but the need for documented, consistently applied safeguards remains the same.

CMIT Solutions supports organizations in Fayetteville, Newnan, Peachtree City, Carrollton, Locust Grove, McDonough, Zebulon, Stockbridge, and surrounding Georgia communities. Our local team begins by understanding your industry, contractual obligations, technology environment, and the types of information your business handles.

We then evaluate your current controls and help establish a practical compliance plan. Depending on your requirements, that may include access controls, encryption, security monitoring, employee training, documentation, incident response planning, vendor assessments, vulnerability testing, and ongoing risk reviews.

CMIT Solutions of Atlanta Southern Crescent combines attentive local support with the cybersecurity expertise and resources of a nationwide network. Whether you are preparing for an assessment, responding to a customer requirement, pursuing regulated contracts, or strengthening an existing compliance program, we can help you determine what needs to happen next.

Talk to a Local IT Compliance Expert

Ready to Get Started with Managed IT Services?

Business Data Compliance FAQs

What are business data compliance solutions?

Business data compliance solutions help organizations identify applicable requirements and implement the policies, processes, documentation, and technical safeguards needed to satisfy them. The exact program depends on the organization’s industry, contracts, data, and risk profile.

Which Atlanta businesses need IT compliance support?

Compliance support may be appropriate for businesses that handle health information, accept payment cards, work with government agencies, operate as FINRA member firms, serve individuals in the European Union, or have customers and contracts that impose specific cybersecurity requirements.

Can IT compliance services improve cybersecurity?

Yes. Many compliance programs require safeguards that are also central to effective cybersecurity, including controlled access, encryption, system monitoring, employee training, vendor oversight, backups, and incident response planning.

What risks can non-compliance create?

Depending on the applicable requirement, non-compliance may lead to fines, legal exposure, failed assessments, lost contracts, increased insurance difficulty, operational disruption, remediation expenses, and damage to customer trust.

How often should a business conduct a compliance assessment?

The appropriate schedule depends on the framework and the organization’s risk. Assessments should also be considered after major technology changes, security incidents, acquisitions, new contracts, regulatory updates, or changes in the types of data the business handles.

Does CMIT Solutions provide legal certification that a business is compliant?

No. CMIT Solutions can assess technology controls, identify gaps, implement safeguards, develop documentation, and support assessment readiness. Legal interpretations and official certifications should come from qualified counsel or the authorized assessor responsible for the applicable framework.