Many businesses treat IT the same way they treat a car that’s still running fine: if nothing seems broken, why spend money fixing it? That mindset feels practical in the short term, but it quietly builds up costs that rarely show up on a monthly budget line until a crisis forces the issue. By then, the price of waiting has usually grown far larger than the cost of addressing problems early would have been.
CMIT Solutions of Austin Downtown West sees this pattern play out regularly with businesses that call after a system failure, a security incident, or a slowdown that’s been building for months. This article breaks down the real, often hidden costs of a reactive approach to IT, why it’s become riskier than ever, and what a more proactive model actually looks like in practice.
Why the “If It Isn’t Broken” Mindset Feels Reasonable
On the surface, waiting until something fails before investing in IT seems like a sensible way to control costs. Every dollar spent on maintenance, monitoring, or upgrades feels optional when systems appear to be working normally. This thinking is reinforced by a few common assumptions:
- Technology that’s currently working doesn’t need attention
- IT spending is easier to justify when tied to a visible problem
- Preventive maintenance feels like an ongoing expense with no clear return
- Smaller businesses often believe major outages only happen to larger companies
The problem is that these assumptions rarely account for what’s happening beneath the surface. Aging hardware, unpatched software, and outdated network configurations often continue functioning right up until the moment they don’t, and that moment is rarely convenient.
The Direct Financial Costs of Reactive IT
When something does break, the financial impact tends to be far higher than the cost of preventing the issue in the first place.
Emergency repair premiums. IT providers, like most service industries, typically charge more for urgent, same-day support than they would for scheduled maintenance, meaning businesses often pay a premium specifically because they waited.
Extended downtime. Diagnosing and fixing an unexpected failure takes longer than addressing a known issue proactively, and every hour of downtime translates directly into lost revenue and productivity.
Data loss and recovery costs. Systems that fail without proper backups in place can result in permanently lost files, customer records, or financial data, often at a cost far exceeding what backup infrastructure would have required.
Hardware replaced under pressure. Emergency equipment purchases rarely allow time to shop for the best price or right-sized solution, often resulting in businesses overpaying for whatever is immediately available.
These direct costs are only part of the picture. A closer look at how poor network management costs accumulate over time shows how much of this expense builds up quietly before ever becoming visible on a balance sheet.
The Productivity Cost Nobody Tracks
Beyond the obvious repair bills, reactive IT quietly drains productivity in ways that rarely get measured but add up significantly over time.
- Employees working around slow or malfunctioning systems instead of reporting issues
- Repeated small outages that interrupt workflow throughout the day
- Staff spending time troubleshooting problems instead of doing their actual jobs
- Delayed projects caused by unreliable systems or software crashes
- Frustration and lower morale from working with unreliable technology day after day
Most businesses never calculate the cumulative cost of these smaller disruptions, yet they often exceed the cost of a single major outage over the course of a year. Recovering this lost time requires a shift in approach, one explored further in this discussion of recovering lost productivity through smarter, better-maintained systems.
Security Risks That Build Quietly Over Time
Reactive IT doesn’t just create operational risk, it creates a widening security gap that attackers are increasingly skilled at finding and exploiting.
- Unpatched software vulnerabilities remain open far longer without regular maintenance schedules
- Outdated systems often stop receiving security updates entirely once they fall behind current versions
- Weak or inconsistent access controls tend to go unnoticed until an incident forces a review
- Security tools left unmonitored can miss active threats for weeks or months at a time
Waiting for a visible problem before addressing security means many issues are only discovered after an attacker has already found and exploited them. Establishing preventive security measures before an incident occurs remains far less costly than responding to an active breach.
Why Reactive IT Has Become Riskier Than Ever
The consequences of waiting until something breaks have grown more severe in recent years, driven by a few key shifts in how businesses operate and how attackers target them.
Greater system interdependence. Modern businesses rely on interconnected cloud platforms, software integrations, and remote access tools, meaning a single failure can cascade across multiple systems rather than staying isolated to one device.
Faster-moving cyber threats. Attackers move quickly once they find a vulnerability, often exploiting gaps within hours of discovery, leaving little room for a slow, reactive response.
Rising customer and regulatory expectations. Businesses are increasingly expected to demonstrate reasonable safeguards were in place, and a reactive approach rarely holds up well under scrutiny after an incident.
Remote and hybrid work complexity. Distributed teams working from multiple locations and devices create more potential points of failure than a single centralized office environment did in years past.
This shift is part of a broader move many businesses are making toward proactive IT support models designed to catch issues before they escalate into full outages. More businesses across the region are recognizing the value of forward thinking IT management that identifies risks well before they become emergencies.
The Business Growth Trap
One of the most overlooked hidden costs of reactive IT shows up as a business grows. Systems that worked fine for a small team often can’t keep pace as headcount, data volume, and customer demands increase, and the resulting strain frequently goes unnoticed until it causes a visible failure.
- Software licensing that no longer matches current team size or usage patterns
- Network infrastructure never upgraded to handle increased traffic or device count
- Manual processes that worked at a small scale but create bottlenecks as volume grows
- Security policies that haven’t been updated to reflect a larger, more complex organization
This pattern is explored in depth in this look at outgrowing business technology without realizing it until a costly breakdown forces the issue. Fast-growing companies are particularly susceptible, a challenge covered further in this discussion of unnoticed technology growth gaps that widen quietly during periods of expansion.
Blind Spots That Leadership Often Misses
Reactive IT tends to thrive in environments where leadership doesn’t have full visibility into the state of the company’s technology. Without regular reporting or reviews, problems can persist for a long time before anyone at a decision-making level becomes aware of them.
Common blind spots include:
- Assuming IT issues are being handled simply because no one has complained recently
- Not knowing how old critical hardware or software actually is
- Underestimating how much time employees spend working around technology problems
- Believing current backups are reliable without ever testing a full recovery
These gaps are discussed further in this look at leadership technology blind spots that often go unnoticed until they’ve already begun slowing down broader operations. Left unaddressed, many businesses find themselves gradually losing technology control without a single dramatic event marking the turning point.
What Happens When Backups Are an Afterthought
Backups are one of the clearest examples of how reactive thinking creates hidden risk. Many businesses assume backups are working correctly simply because a backup process was set up at some point, without ever testing whether a full recovery would actually succeed.
- Backup failures often go unnoticed until they’re needed during an actual emergency
- Incomplete backups may miss critical files or recent changes not captured in the last scheduled run
- Recovery time expectations are frequently unrealistic when they haven’t been tested in advance
- Ransomware attacks specifically target backup systems, making outdated protection especially dangerous
Understanding common backup mistakes crisis situations reveal helps businesses avoid discovering these gaps at the worst possible moment. Modern approaches to faster disaster recovery are helping businesses close this gap with smarter, more reliable backup infrastructure than older systems could offer.
The Real Cost of a Major Outage
When reactive IT finally results in a significant failure, the consequences often extend well beyond the immediate technical fix.
- Lost revenue during downtime, particularly for businesses reliant on continuous system access
- Damaged customer trust if service interruptions become visible or repeated
- Employee frustration and burnout from repeatedly dealing with preventable problems
- Increased insurance premiums or claim denials tied to inadequate preventive measures
One particularly stark example involved a manufacturing business whose production line shutdown following a ransomware attack illustrates just how far-reaching the consequences of inadequate preparation can be. Preparing in advance requires treating continuity preparedness gaps as a priority long before an actual incident forces the conversation.
Making IT a Leadership Priority, Not Just a Technical One
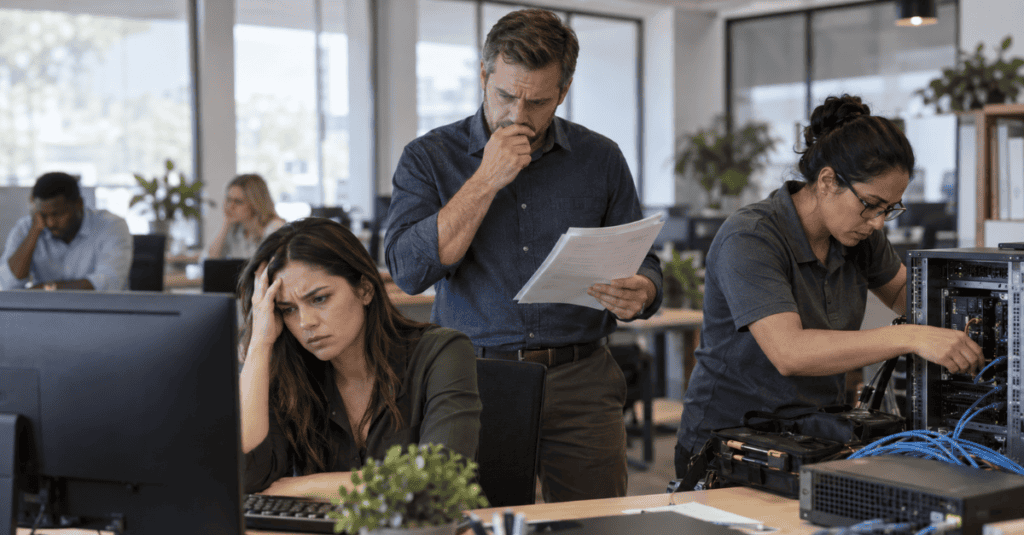
One of the biggest shifts businesses need to make is recognizing that IT decisions aren’t purely technical, they’re business decisions with direct financial and operational consequences. Treating IT strategy as a leadership responsibility, rather than delegating it entirely and revisiting it only when something breaks, changes the entire approach to risk.
This shift in perspective is covered in more depth in this discussion of leadership continuity conversation topics that increasingly belong in boardroom discussions rather than being left solely to IT staff.
Building a Proactive IT Strategy
Moving away from a reactive approach doesn’t require an overwhelming overhaul. It starts with a few foundational changes that shift the focus from fixing problems to preventing them.
- Establish regular monitoring. Continuous monitoring catches early warning signs, such as declining hardware performance or unusual network activity, well before they escalate into a full failure.
- Schedule proactive maintenance. Routine patching, updates, and system checks should happen on a predictable schedule rather than only after something stops working correctly.
- Test backups regularly. A backup system is only as good as its last successful test. Regular recovery drills confirm that data can actually be restored when it matters most.
- Plan technology upgrades ahead of need. Budgeting for hardware and software refresh cycles in advance avoids the pressure and inflated costs of emergency replacements.
- Build a documented response plan. Even proactive businesses occasionally face unexpected issues. Having a clear plan in place reduces confusion and downtime when something does happen.
Building this kind of structure often benefits from a documented approach, similar to the structured technology planning frameworks more businesses are adopting instead of continuing to fix problems one at a time as they surface.
Where Managed IT Support Fits In
Shifting from a reactive to a proactive approach is significantly easier with a dedicated technology partner managing the details rather than trying to handle everything internally on an as-needed basis.
A well-rounded approach typically starts with proactive IT management that catches small issues before they become expensive emergencies, supported by rapid response support whenever something unexpected does come up. Ongoing protection depends on consistent network oversight that keeps infrastructure running smoothly rather than waiting for a visible slowdown to prompt a review.
As business needs shift, flexible cloud solutions allow systems to scale without the strain that often leads to reactive fixes down the road, while protected data storage ensures critical information is recoverable no matter what happens to the original system. Businesses in regulated industries benefit from compliance readiness support that keeps documentation and safeguards current rather than scrambling during an audit.
Day-to-day operations run more smoothly with streamlined business communication tools that reduce the friction reactive systems often create, paired with efficient software tools that are properly maintained rather than left to degrade over time. When it’s time to invest in new equipment or platforms, planned technology investment ensures purchases are made thoughtfully rather than under emergency pressure.
Ongoing IT consulting helps businesses build a long-term roadmap rather than continuing to make decisions one crisis at a time. CMIT Solutions of Austin Downtown West works with local businesses to build exactly this kind of proactive foundation, replacing the stress and expense of reactive fixes with a plan built around prevention. Businesses exploring their options more broadly can also review general Austin IT provider resources available across the region.
Making the Shift Before the Next Breakdown
The true cost of ignoring IT rarely shows up as a single line item. It builds quietly through lost productivity, mounting security risk, and the eventual price of an emergency fix that could have been avoided. Businesses that shift toward a proactive approach consistently spend less over time while avoiding the disruption that reactive IT almost guarantees eventually.
If your business is ready to stop waiting for the next breakdown, schedule a consultation to review your current systems and build a plan focused on prevention rather than emergency repairs.
Frequently Asked Questions