Cyber insurance used to be a fairly simple purchase. A business filled out a short application, answered a handful of general questions, and received a policy at a predictable rate. That process has changed dramatically over the past few years, and many Cincinnati business owners are discovering the shift only when a renewal notice arrives with a longer application, a higher premium, or an outright denial of coverage.
Insurance carriers have paid out enormous sums following ransomware attacks, business email compromise incidents, and data breaches, and they have responded the way any industry does after sustained losses. They have tightened underwriting standards, added detailed security requirements, and started treating cyber policies more like commercial property insurance, where the condition of what is being insured directly affects both eligibility and price.
For small and mid sized businesses, this shift creates a real challenge. The security controls insurers now expect often exceed what many businesses currently have in place, and figuring out what actually qualifies as “reasonable” security can feel like guesswork. Business owners who have carried the same policy for years without much change are often caught off guard when a renewal application suddenly asks detailed technical questions their previous applications never touched. This guide breaks down what has changed, what insurers are looking for today, and how a business can close the gap without overhauling its entire technology budget.
Why Cyber Insurance Requirements Have Tightened
A few converging trends explain why underwriting has become so much stricter in a relatively short period of time.
- Ransomware payouts have surged. Carriers have absorbed significant losses covering ransom payments, recovery costs, and business interruption claims, pushing them to demand stronger preventative controls before issuing coverage.
- Claims data now informs underwriting decisions. Insurers have years of claims history showing which specific gaps, such as missing multi-factor authentication, correlate most strongly with successful attacks.
- Regulatory pressure has increased. As data privacy laws expand, insurers face growing exposure tied to compliance violations, prompting closer scrutiny of applicant practices.
- Attackers have become more efficient. Automated attack tools mean that weak security controls get exploited faster than in previous years, shortening the window insurers have to intervene before a claim is filed.
The result is an underwriting environment where businesses without documented, verifiable security practices face higher premiums, reduced coverage limits, or denied applications altogether.
What Insurers Are Requiring Right Now
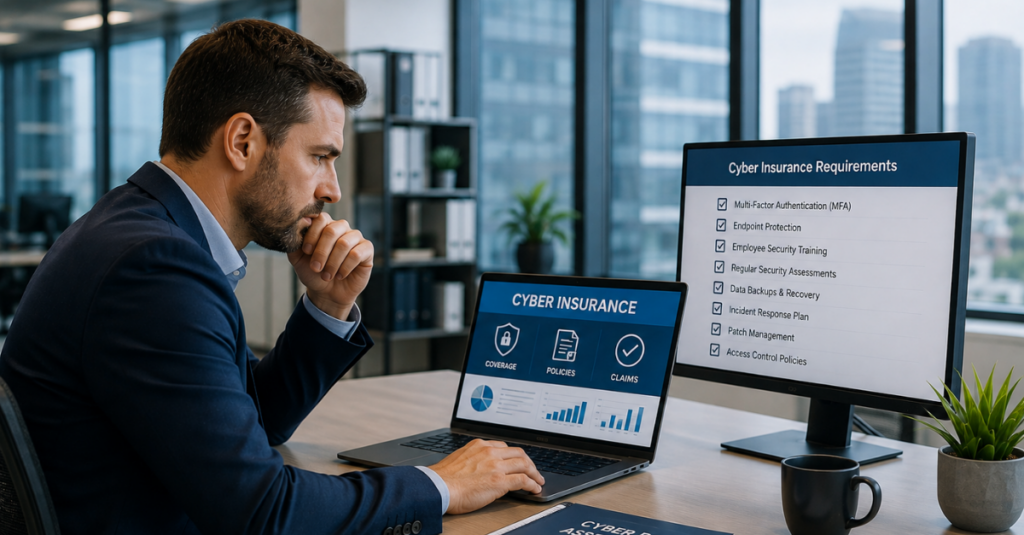
Cyber insurance applications have grown considerably more detailed, often asking pointed technical questions rather than general yes-or-no items. While specific requirements vary by carrier and policy size, several controls have become close to universal expectations.
- Multi-factor authentication on email, remote access, and administrative accounts, often listed as a non-negotiable requirement rather than a recommendation
- Endpoint detection and response tools capable of identifying and stopping threats in real time, rather than relying solely on traditional antivirus software
- Tested, offline or immutable backups that cannot be encrypted or deleted during a ransomware attack
- Documented incident response plans outlining exactly how a business would respond to a breach or attack
- Regular employee security training, particularly around phishing recognition
- Patch management processes that keep software and systems updated on a consistent schedule
- Privileged access management, limiting administrative account access to only those who genuinely need it
Businesses unable to demonstrate these controls often face significantly higher premiums, and in some cases, carriers decline coverage entirely until gaps are addressed.
The Connection Between Weak Security and Denied Claims
Meeting minimum requirements to obtain a policy is only part of the picture. Insurers also scrutinize claims closely, and businesses that misrepresented their security posture during the application process risk having claims denied entirely, even after paying premiums for months or years.
This has become a common and costly surprise. A business checks a box confirming multi-factor authentication is in place, but only a portion of accounts are actually protected. An attack occurs through one of the unprotected accounts, and the carrier denies the claim, citing a misrepresentation on the application. Cases like this have become a growing point of frustration for business owners who assumed a signed policy guaranteed protection, only to learn during a claims investigation that the fine print on their original application carried far more weight than they realized. Understanding employee AI usage and other emerging tools that expand a business’s attack surface has become part of this picture too, since insurers increasingly ask about AI-related data handling practices as part of the underwriting process.
To avoid this outcome:
- Verify every security claim on an application is fully and accurately implemented, not partially in place
- Keep documentation ready to prove controls are active, such as configuration screenshots or vendor reports
- Update insurers promptly if security controls change between renewal periods
- Work with a knowledgeable IT partner before completing an application, rather than filling it out based on assumptions
Ransomware Remains the Primary Driver of Stricter Requirements
Ransomware continues to dominate cyber insurance claims data, and insurers have responded by making ransomware-specific controls a central part of underwriting. Data on why ransomware payment trends continue rising shows a troubling pattern, where businesses that pay once are frequently targeted again, sometimes by the same attackers testing whether the same vulnerabilities remain unaddressed.
Insurers now commonly require:
- Immutable backup systems specifically designed to resist ransomware encryption
- Network segmentation limiting how far an attacker can move after an initial breach
- Endpoint monitoring capable of detecting ransomware behavior before full encryption occurs
- Clear documentation showing backups are tested regularly, not just scheduled
The broader operational disruption caused by these attacks, detailed in reporting on how ransomware system management failures cascade across an organization, helps explain why insurers have become so focused on prevention rather than simply covering the aftermath.
How Multi-Factor Authentication Became Non-Negotiable
Few individual controls have had as much influence on underwriting decisions as multi-factor authentication. Claims data consistently shows that accounts without this protection are dramatically more likely to be compromised, particularly through phishing and credential-stuffing attacks.
- Nearly every major carrier now requires multi-factor authentication on email systems at minimum
- Many policies extend this requirement to remote access tools, administrative accounts, and cloud platforms
- Partial implementation, covering only some accounts, is increasingly treated the same as having no protection at all during claims review
- Some insurers now request documentation proving multi-factor authentication is enforced organization-wide, not just technically available
Businesses exploring how authentication standards continue evolving may find it useful to look at emerging password free authentication methods, since several carriers have begun recognizing these stronger verification approaches favorably during underwriting.
Phishing Awareness and the Cost of a Single Click
Human error remains one of the leading causes of successful cyberattacks, and insurers increasingly expect businesses to demonstrate ongoing staff training rather than a single annual session. Newer phishing tactics have made this training even more important, particularly as attackers shift toward methods like QR code phishing that bypass many traditional email security filters entirely.
- Run phishing simulations regularly to measure staff awareness in practice, not just in theory
- Document training completion for every employee, since insurers may request proof during underwriting or claims review
- Update training content as attack tactics evolve, rather than reusing the same material year after year
- Establish a clear, simple process for staff to report suspicious emails without fear of embarrassment
Building the Security Foundation Insurers Expect
Meeting current cyber insurance requirements does not require an unlimited budget, but it does require a structured approach. The following areas represent the core foundation most carriers now expect to see in place.
Strong Cybersecurity Controls
A comprehensive approach to cybersecurity protection services forms the backbone of insurance readiness, covering endpoint protection, threat monitoring, and access controls in a way that satisfies both practical security needs and underwriting requirements.
Reliable Backup and Recovery
Since ransomware remains the top driver of claims, dependable data backup solutions with regular restoration testing are essential, not optional. Insurers increasingly request specific details about backup frequency, storage location, and testing schedules during the application process.
Secure Cloud Infrastructure
Businesses relying on cloud platforms need to confirm those environments meet the same standards insurers expect elsewhere. Properly configured secure cloud solutions include encryption, access controls, and vendor agreements that address data protection responsibilities clearly.
Documented Compliance Practices
Industries facing regulatory requirements, including healthcare, legal, and financial services, benefit from formal compliance support services that keep documentation current and audit-ready, which often overlaps directly with what cyber insurers request during underwriting.
Network Visibility and Segmentation
Insurers want assurance that an attacker cannot move freely across an entire network after a single compromised account. Proper network management tools provide the visibility and segmentation needed to limit this kind of lateral movement.
Industry-Specific Considerations
Cyber insurance requirements are not identical across every industry, and businesses in higher-risk sectors often face additional scrutiny. Legal practices handling confidential client information have seen particularly close attention paid to legal practice security during underwriting, given the sensitive nature of the data involved. Engineering firms managing proprietary technical data face similar scrutiny, making investment in solid engineering firm infrastructure an increasingly important factor in securing favorable coverage terms. Accounting and financial services firms, frequently targeted due to the payment and banking data they handle, face similar pressure tied to financial data risks that insurers evaluate closely during the application process.
Zero Trust and the Future of Underwriting Standards
As underwriting standards continue tightening, many industry analysts expect zero trust principles to become an explicit requirement rather than an optional best practice. The core idea behind zero trust security already aligns closely with what insurers are asking for: verified access, limited permissions, and continuous monitoring rather than blind trust extended to anything inside the network.
- Verify every access request rather than assuming internal network traffic is automatically safe
- Limit each user’s access strictly to what their role requires
- Monitor access patterns continuously to flag unusual behavior quickly
- Document these controls clearly, since insurers increasingly ask for specifics rather than general assurances
Comparing Cyber Insurance Carriers and Policy Terms
Not every cyber insurance policy offers the same protection, even when premiums look similar on the surface. Businesses evaluating options, whether for a first policy or a renewal, benefit from looking beyond price alone.
- Review sub-limits carefully. Some policies cap specific types of coverage, such as ransomware payments or business interruption losses, far below the overall policy limit, which can leave a business underinsured for its most likely scenario.
- Understand the claims process before signing. Carriers vary significantly in how quickly they respond to claims and how much documentation they require during an active incident, when time matters most.
- Ask about panel requirements. Many policies require businesses to use pre-approved incident response firms or legal counsel, which can limit flexibility during an actual event if a business already has trusted vendors in place.
- Clarify what counts as a covered incident. Definitions of a qualifying breach or attack vary between carriers, and some exclusions are easy to miss without careful review.
- Confirm renewal terms in advance. Understanding how requirements might tighten at the next renewal helps a business plan security investments proactively rather than scrambling each year.
Working through these details with both an insurance broker and an IT partner familiar with current underwriting standards helps ensure a policy actually delivers the protection a business expects when it matters most. A policy that looks affordable on paper can end up costing far more than a slightly higher premium if it leaves a business underinsured during the exact scenario it was purchased to cover.
The Growing Role of Third-Party Risk in Underwriting
Insurers are increasingly looking beyond a business’s own systems to evaluate the vendors and partners connected to its network. A breach originating from a billing company, software vendor, or IT contractor can trigger a claim just as easily as one originating internally, and carriers have started asking more detailed questions about these relationships.
- Maintain a current list of vendors with access to sensitive data or systems
- Confirm vendors carry their own cyber insurance coverage where appropriate
- Review data protection agreements with key vendors to clarify responsibility in the event of an incident
- Limit vendor access strictly to what each relationship actually requires
This growing focus on third-party risk reflects a broader shift in how insurers evaluate exposure, treating a business’s full network of connections as part of its overall risk profile rather than looking only at internal systems in isolation.
Preparing for a Cyber Insurance Application or Renewal
A structured preparation process makes the underwriting experience far less stressful and improves the odds of favorable terms. The following steps help businesses get ready before an application or renewal deadline arrives.
- Complete an internal IT self assessment to identify gaps before an insurer identifies them first
- Gather documentation proving current security controls, including configuration details and training records
- Review the specific application questions in advance, since many carriers now provide detailed questionnaires rather than short forms
- Consult with an IT partner offering strategic IT guidance to address gaps before submitting an application
- Avoid rushing the process during the final days before a renewal deadline, since meaningful improvements often take weeks to implement properly
What Happens If a Business Cannot Meet Current Requirements
Businesses that discover significant gaps during the application process are not necessarily out of options. Most carriers offer a path forward, though it typically requires demonstrated improvement within a defined timeframe.
- Some insurers offer conditional coverage that requires specific improvements within a set period, such as ninety days
- Premiums may increase temporarily until documented improvements are verified
- Coverage limits may be reduced until a business demonstrates stronger controls
- Working with a qualified IT partner to close gaps quickly often improves both eligibility and pricing at the next renewal
Businesses facing this situation benefit from moving quickly rather than waiting until the next renewal cycle to address identified weaknesses. Delaying often means facing the same conversation again at the following renewal, with even stricter requirements and less goodwill from a carrier that has already flagged the account as higher risk.
The Role of a Managed IT Partner in Insurance Readiness
Navigating cyber insurance requirements alongside daily business operations is difficult without dedicated support. A managed IT services partnership provides the ongoing monitoring, documentation, and technical controls insurers expect, without requiring a business to build this expertise internally.
- Continuous monitoring generates the kind of documentation insurers increasingly request
- Regular security assessments catch gaps before they affect an application or claim
- Established relationships with security tools and vendors streamline implementation of required controls
- Ongoing responsive IT support ensures issues are addressed quickly, reducing the risk of a control lapsing between reviews
Businesses evaluating whether their current provider is keeping pace with these changing requirements can review client success stories from similar organizations, or explore educational webinar sessions covering cyber insurance and security topics in more depth. Understanding what distinguishes a trusted technology partner from a general-purpose provider matters significantly here, since insurance readiness requires specific expertise beyond basic technical support. Learning more about the local IT experts guiding these recommendations helps businesses understand who they are trusting with this process. Many business owners find that the same partner who handles daily IT support is also best positioned to speak knowledgeably with an insurance broker, since they already understand the specific systems and controls in question rather than needing to learn them from scratch during a stressful renewal period.
Budgeting for Insurance-Ready Security
Business owners often assume that meeting insurer requirements demands a large capital investment. In practice, the improvements needed frequently cost far less than the premium increases or coverage denials businesses face without them.
- Use available cost calculator tools to compare current security spending against the cost of improved coverage terms
- Review helpful IT resources covering budgeting for security and compliance improvements
- Consider flexible IT service packages that bundle the controls insurers most commonly require
- Factor IT procurement services into planning so security-related purchases avoid unnecessary duplication
Recent updates on regional technology and insurance trends are also available through recent company news, and businesses can review current industry certifications partners as part of evaluating provider credibility during this process. Business owners who take the time to compare these details before a renewal deadline tend to negotiate from a much stronger position than those scrambling to gather documentation after receiving a denial or a steep premium increase.
The Cost of Waiting Too Long to Act
Some business owners delay addressing security gaps until a renewal notice forces the issue, assuming there will be time to catch up before coverage actually lapses. This approach carries real risk. Meaningful improvements, such as rolling out multi-factor authentication across every account or establishing a properly tested backup system, take time to implement correctly, and rushing the process increases the likelihood of gaps being overlooked.
- Waiting until the last minute limits options and often results in accepting whatever terms a carrier offers rather than negotiating from a position of strength
- Rushed implementations are more prone to configuration errors that undermine the very protections being put in place
- A gap in coverage, even a brief one, leaves a business fully exposed to any incident that occurs during that window
- Starting early allows time to properly test new controls before they need to hold up against a real threat
Treating cyber insurance readiness as an ongoing process, reviewed well before each renewal, consistently produces better outcomes than a last-minute scramble.
A Simple Starting Checklist
Business owners preparing for an upcoming cyber insurance application or renewal can start with these steps this month.
- Confirm multi-factor authentication is active across every account, not just email
- Test backup restoration to verify data can actually be recovered, not just backed up
- Gather documentation proving current security controls before the application process begins
- Schedule a phishing awareness session and document staff participation
- Visit the Cincinnati IT provider homepage to review available support options for closing identified gaps
- Compare current infrastructure against a modern managed IT services offering built around today’s insurance standards
Final Thoughts
Cyber insurance is no longer a simple formality businesses can renew without close attention. Underwriting standards have tightened significantly, and the businesses best positioned for favorable coverage are the ones treating security as an ongoing practice rather than a checklist completed once a year. Closing the gap between current practices and what insurers now expect does not require an unlimited budget, but it does require a clear plan and consistent follow-through.
This trend shows no signs of reversing. As claims data continues to accumulate and attackers refine their methods further, it is reasonable to expect underwriting standards to keep tightening rather than loosen back to where they stood a few years ago. Businesses that build strong security habits now will find each future renewal far less stressful than those still catching up application after application. CMIT Solutions of Cincinnati East helps local businesses build exactly that kind of foundation, aligning practical security improvements with the documentation and controls today’s cyber insurance market demands.
If your business is ready to find out where it stands against current cyber insurance requirements, schedule a consultation with our team to get started.
Frequently Asked Questions