For years, business continuity planning meant one thing above all else: backups. If a server failed or a disaster struck, businesses assumed that having a recent backup was enough to get operations running again. That assumption no longer holds up in 2026. Modern threats are not just about losing data, they are about attackers actively targeting the systems, credentials, and processes businesses rely on to function every single day.
Cyber resilience has become the real foundation of business continuity planning. It is a broader concept than backups alone, covering how quickly a business can detect an attack, contain it, recover from it, and keep operating throughout the process. This article explains why this shift matters, what cyber resilience actually includes, and how businesses can build a continuity plan that reflects the realities of today’s threat landscape. Businesses starting this process often begin with a comprehensive IT assessment to understand where their current plan falls short.
Why Backups Alone Are No Longer Enough
Backups remain an essential part of any continuity strategy, but treating them as the entire strategy creates a dangerous blind spot. A backup only helps if the business can actually detect a problem quickly, contain it before it spreads, and restore operations without introducing the same vulnerability all over again.
Consider what a backup alone does not address:
- Detection speed. A backup does not help if an attacker sits undetected inside a network for weeks before triggering an incident.
- Containment. Restoring from backup does not stop an active attacker from reentering the same environment through the same vulnerability.
- Operational continuity during recovery. Backups restore data, but they do not keep a business running while systems are being rebuilt.
- Reinfection risk. Restoring data without addressing the original point of compromise often leads to the same incident happening again shortly after recovery.
This is why modern continuity planning increasingly centers on cyber resilience rather than backup files alone. A closer look at real world incidents in downtime prevention strategies shows how businesses relying solely on backups often still experience extended downtime, even after data has technically been restored.
What Cyber Resilience Actually Means
Cyber resilience refers to a business’s ability to continue operating, or recover quickly, in the face of a cyberattack. It goes beyond preventing incidents entirely, since no business can guarantee complete prevention, and instead focuses on minimizing impact when something does happen.
Core pillars of cyber resilience include:
- Prevention. Reducing the likelihood of an attack succeeding through strong security controls
- Detection. Identifying suspicious activity quickly, rather than discovering an incident after significant damage has occurred
- Response. Containing and neutralizing a threat before it spreads across the entire network
- Recovery. Restoring systems and data efficiently, without reintroducing the original vulnerability
- Continuity. Keeping critical operations running throughout the entire incident, not just after recovery is complete
This layered approach is a significant shift from older continuity models built almost entirely around the assumption that a backup alone would solve the problem. Businesses building this foundation often pair it with a managed detection response program to ensure detection happens as early as possible.
Why 2026 Has Made This Shift Urgent
Several trends have converged to push cyber resilience to the center of continuity planning this year.
- Attack sophistication has increased. Ransomware groups now routinely target backup systems directly, knowing businesses rely on them for recovery.
- Downtime costs have grown. Every hour of disruption tends to carry a higher financial and reputational cost than it did just a few years ago.
- Attackers move faster. The time between initial compromise and full network impact has shortened significantly, leaving less room for manual detection.
- Remote and hybrid work has expanded the attack surface. More devices and access points mean more potential entry points for an attacker.
These trends are explored further in emerging security threats, which highlights how quickly attacker techniques have evolved compared to traditional continuity assumptions built years ago.
How Attackers Specifically Target Backup Systems
One of the most important developments driving this shift is that modern ransomware attacks frequently target backup systems directly, specifically because attackers know backups are the primary recovery method most businesses rely on.
Common tactics include:
- Locating and encrypting backup files alongside primary systems
- Deleting backup snapshots before deploying ransomware on live systems
- Compromising backup credentials to disable automated backup schedules in advance
- Targeting cloud based backup platforms that are not properly isolated from the main network
This is precisely why many businesses discover, often too late, that their Microsoft 365 backup assumptions were incomplete, since standard cloud subscriptions frequently lack the isolated, independent backup protection that true resilience requires.
Building a Continuity Plan Around Detection, Not Just Recovery
A modern continuity plan needs to place equal weight on detecting problems early as it does on recovering from them. The faster an issue is identified, the less damage occurs and the shorter the recovery process becomes.
Key detection focused elements include:
- Continuous monitoring across every device and system connected to the network
- Behavioral analysis that flags unusual activity before it escalates into a full incident
- Regular vulnerability scanning to identify weaknesses before attackers find them
- Clear escalation procedures so suspicious activity is reviewed and acted on quickly
Businesses building this detection layer often review why zero trust security as a framework for ensuring no device or user is automatically trusted, significantly reducing how far an attacker can move undetected.
The Role of Network Architecture in Cyber Resilience
How a network is structured plays a direct role in how well a business can contain an incident once detected. A flat, unsegmented network allows an attacker who compromises one device to move freely across the entire environment.
Strong architecture for resilience includes:
- Segmenting critical systems away from general administrative and guest access
- Limiting how far any single compromised account can reach within the network
- Isolating backup infrastructure from primary systems entirely
- Maintaining clear documentation of how systems connect to one another
This structural planning is often addressed through dedicated network management solutions, ensuring the network itself supports containment rather than accidentally enabling an attack to spread further.
Recovery Planning: Beyond Simply Restoring Data
Recovery is more than pulling files from a backup. A true recovery plan accounts for how a business will actually resume operations, including systems, communication, and staff coordination during the process.
A complete recovery plan includes:
- Prioritized recovery order, identifying which systems must come back online first
- Clear internal and external communication procedures during an active incident
- Verified, tested backup restoration processes rather than assumptions that backups will work
- A plan for maintaining unified communication systems so staff can coordinate even if primary systems are down
Reviewing data backup solutions with recovery speed in mind, rather than storage cost alone, often reveals gaps that would otherwise only surface during an actual emergency.
Employee Readiness as Part of Continuity Planning
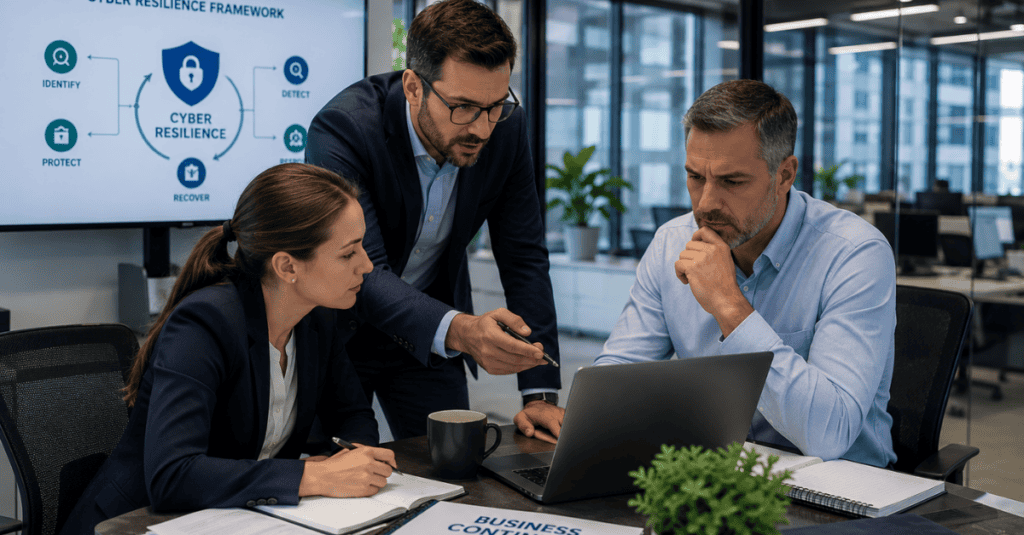
Technology alone cannot guarantee resilience. Staff need to understand their role during an incident, since confusion and delayed decision making often extend downtime far longer than the technical recovery itself requires.
Effective readiness measures include:
- Clear internal documentation outlining who is responsible for what during an incident
- Regular tabletop exercises simulating a real incident scenario
- Ongoing training tied to existing productivity tools setup so staff know how to operate securely even during disrupted conditions
- Defined communication channels that do not depend entirely on systems that might be affected during an incident
Businesses that practice their response plan before an actual incident occurs consistently recover faster than those relying purely on documentation that has never been tested.
Compliance and Regulatory Considerations for Continuity Planning
Regulatory expectations around business continuity and cyber resilience continue to expand, particularly for industries handling sensitive data. Even businesses outside heavily regulated sectors are increasingly expected to demonstrate a documented, tested continuity plan.
Relevant considerations include:
- Documentation proving regular testing of backup and recovery processes
- Clear incident notification procedures aligned with applicable regulations
- Evidence of ongoing risk assessments rather than a one time policy document
- Vendor and third party continuity requirements built into contracts
Businesses navigating these expectations often pair their continuity planning with a broader compliance challenges 2026 review, alongside dedicated compliance support services to ensure documentation keeps pace with evolving requirements.
Vendor and Third Party Resilience Risk
Modern businesses depend on a wide network of software vendors, cloud providers, and service partners. A continuity plan that only accounts for internal systems misses a significant portion of overall risk.
Businesses should evaluate:
- Whether critical vendors have their own documented continuity and resilience plans
- How quickly a vendor can recover if their own systems are compromised
- What certifications or industry certifications partners vendors hold to demonstrate accountability
- Contractual guarantees around uptime and data recovery commitments
A business can build a strong internal resilience plan and still face significant disruption if a critical vendor experiences an outage or breach without a plan of their own.
Cloud Infrastructure and Resilience Planning
Cloud environments play a central role in modern continuity planning, both as a recovery resource and as a potential point of vulnerability if not properly configured.
Important considerations include:
- Ensuring secure cloud services include properly isolated backup environments separate from primary systems
- Understanding how quickly cloud based systems can be restored during an incident
- Reviewing whether hybrid infrastructure provides additional resilience compared to a single environment
- Confirming cloud providers meet the same continuity standards expected internally
Businesses exploring this balance often review hybrid cloud growth as a way to distribute risk across multiple environments rather than depending entirely on a single infrastructure model.
Cost of Reactive Recovery vs Proactive Resilience Planning
The financial difference between businesses with a proactive resilience plan and those relying purely on reactive recovery is often substantial once measured directly.
Reactive recovery typically involves:
- Extended downtime while the scope of an incident is being determined
- Higher recovery costs due to lack of preparation and testing
- Increased risk of paying a ransom due to inadequate backup isolation
- Reputational damage from prolonged service disruption
Proactive resilience planning typically involves:
- Faster detection and containment, significantly reducing overall downtime
- Predictable recovery costs built into ongoing IT investment
- Reduced reliance on paying attackers, since backups remain isolated and functional
- Stronger client and partner confidence due to demonstrated preparedness
Reviewing managed IT costs alongside a ransomware survival guide gives businesses a realistic picture of what separates these two outcomes in practice.
How CMIT Solutions of Plano & Garland Supports Cyber Resilience Planning
CMIT Solutions of Plano & Garland helps local businesses build continuity plans centered on cyber resilience rather than backups alone, ensuring operations can continue even when an incident does occur.
Support typically includes:
- A full comprehensive IT assessment to identify gaps in current continuity planning
- Guidance on network management solutions structured to contain incidents before they spread
- Isolated, tested data backup solutions designed to withstand direct targeting by attackers
- Support building strategic IT guidance that ties continuity planning to broader business goals
- Access to additional IT resources and helpful IT tools for businesses evaluating their own resilience gaps
- Insight from client success stories involving other local businesses that have gone through this process
- Educational webinar sessions covering resilience planning in clear, practical terms
To understand the broader philosophy behind this approach, businesses can review our proven approach or learn our story, and see how ongoing support differs meaningfully from a one time recovery vendor treated purely as network support value rather than a strategic partner.
Conclusion
Business continuity planning in 2026 requires a fundamentally different foundation than it did just a few years ago. Backups remain important, but they are no longer sufficient on their own, especially as attackers increasingly target backup systems directly as part of their strategy. Cyber resilience, built around detection, containment, tested recovery, and ongoing readiness, has become the real measure of whether a business can withstand a serious incident and keep operating throughout it.
If your business is ready to build a continuity plan grounded in real cyber resilience rather than backups alone, schedule a consultation with the team at CMIT Solutions of Plano & Garland to get started: schedule a consultation.
Frequently Asked Questions