Peak shopping season is when retail businesses make their year, and it’s also when they’re most exposed. Higher transaction volume, temporary staff, overloaded networks, and a surge in both in store and online traffic create the perfect conditions for a security incident. Attackers know this too, which is exactly why retail data breaches spike so predictably every year around the same high volume shopping windows.
The frustrating part is that most peak season security failures aren’t the result of a sophisticated, unstoppable attack. They’re the result of ordinary gaps that existed all year but only become a real problem once transaction volume multiplies and the margin for error disappears. A point of sale system running outdated software, a website plugin that hasn’t been updated, or a seasonal employee given more system access than necessary can all turn into serious incidents once the stakes are higher and the pressure to keep things running is greater.
CMIT Solutions of Plano & Garland works with retail businesses of all sizes to get ahead of these risks before the busiest weeks of the year arrive, rather than reacting to a problem in the middle of the holiday rush. This guide walks through exactly where customer data is most at risk during peak periods and what a practical protection plan looks like.
Why Peak Season Multiplies Risk
Retail security risk doesn’t stay flat throughout the year. It concentrates heavily around specific high volume periods, and understanding why helps explain where to focus preparation efforts.
Factors That Raise Risk During Peak Periods
- Transaction volume increases dramatically, giving attackers more opportunities and more data to target
- Seasonal and temporary staff often receive system access quickly, without the same vetting or training as full time employees
- Networks and servers face traffic loads far beyond normal operating conditions
- IT and security teams are stretched thin trying to keep everything running rather than actively monitoring for threats
- Third party vendors, from payment processors to shipping integrations, see increased activity and become more attractive targets themselves
Attackers are aware of all of this. Recent ransomware incidents affecting retail businesses have shown a clear pattern of targeting companies specifically during high volume periods, when the cost of downtime is highest and businesses are more likely to make hasty decisions under pressure.
Point of Sale Security Deserves Special Attention
Point of sale systems are one of the most direct paths to customer payment data, and they’re often the least frequently updated piece of technology in a retail environment. Many businesses treat POS systems as “set it and forget it” hardware, which is precisely the assumption attackers rely on.
Common POS Vulnerabilities
- Outdated software missing critical security patches
- Default administrative credentials never changed after installation
- POS terminals connected to the same network as guest Wi-Fi or other non essential systems
- Physical access to terminals not properly restricted during busy periods
- No monitoring in place to detect unusual transaction patterns
Point of sale networking should isolate payment terminals onto a dedicated, restricted network segment, separate from guest Wi-Fi, back office systems, and any other non essential traffic. This single step significantly reduces the chance that a compromised device elsewhere in the store can reach payment systems directly.
Preparing POS Systems Before the Season Starts
- Confirm all POS software and firmware are fully updated well before peak season begins
- Change any default or shared administrative passwords across all terminals
- Verify that payment card compliance requirements are met and documented
- Test backup POS processes in case primary systems experience an outage during high traffic periods
Ecommerce Security During High Traffic Periods
Online retail faces its own distinct set of risks during peak shopping windows, particularly around checkout page security and the increasingly common practice of digital skimming, where malicious code is injected into a checkout process to quietly capture payment information as customers enter it.
Signs an Ecommerce Platform May Be Vulnerable
- Outdated plugins or extensions on the shopping cart platform
- No regular integrity checks on checkout page code
- Third party scripts loaded directly onto payment pages without review
- Missing web application firewall protection against common attack patterns
Digital skimming attacks are particularly dangerous because they often go undetected for weeks, quietly capturing customer payment data while the site continues functioning normally. Regular integrity monitoring on checkout pages, combined with a current threat landscape review before peak season, helps catch these issues before they affect a large volume of customer transactions.
Handling Traffic Surges Without Sacrificing Security
- Load testing the website well before peak traffic is expected to confirm it can handle volume without slowing security processes
- Ensuring scalable cloud infrastructure is in place so sudden traffic spikes don’t force shortcuts around security checks
- Confirming SSL certificates are current and properly configured across all customer facing pages
- Reviewing checkout page code for unauthorized changes on a regular basis throughout the season, not just once beforehand
Payment Compliance Cannot Be an Afterthought
Retail businesses accepting card payments are subject to Payment Card Industry Data Security Standard requirements, commonly referred to as PCI DSS. Peak season is exactly when compliance gaps tend to surface, since increased transaction volume means increased exposure if standards aren’t being consistently met.
Core Compliance Areas Worth Reviewing Before Peak Season
- Encryption standards for payment data both in transit and at rest
- Network segmentation separating payment systems from other business operations
- Access controls limiting who can view or handle payment card data
- Documentation and audit trails proving compliance measures are actively maintained
Payment card compliance isn’t just a legal requirement. Non compliance discovered after a breach typically results in significantly higher penalties and can affect a retailer’s ability to continue accepting card payments at all. Core protection standards should be reviewed and documented well ahead of the season, not scrambled together after volume has already increased.
Seasonal Staffing Introduces Real Risk
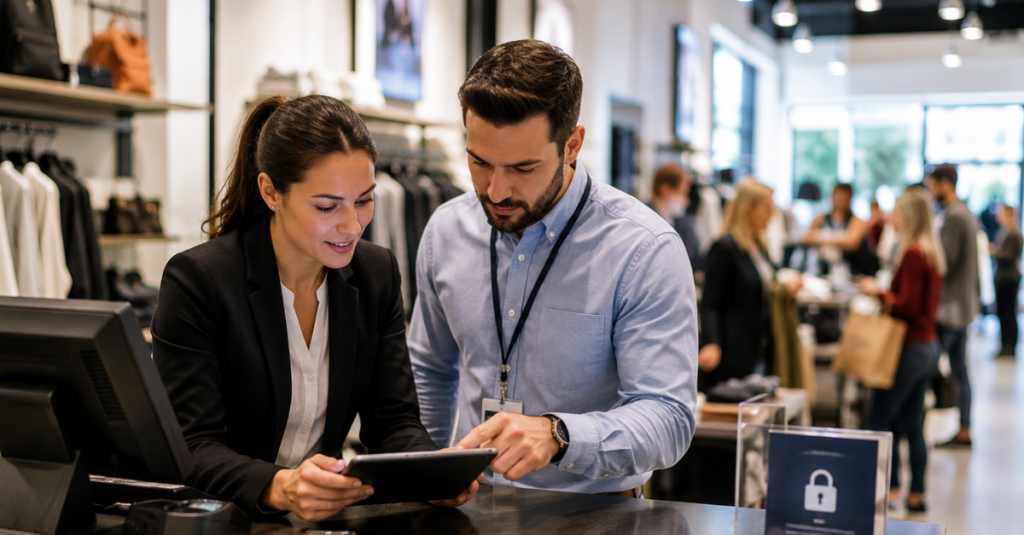
Nearly every retail business brings on temporary or seasonal staff to handle increased volume, and this staffing surge creates a specific and often underestimated security gap. New employees typically need system access quickly, which can mean less thorough vetting, rushed training, and broader access than their role actually requires.
Reducing Seasonal Staffing Risk
- Grant new employees only the specific system access needed for their exact role, nothing broader
- Require the same password and device security policies for seasonal staff as full time employees
- Provide basic security awareness training covering phishing and social engineering before granting system access
- Set access to automatically expire at the end of the employee’s scheduled employment period
Staff scheduling software that integrates with access management can help ensure that system permissions align automatically with actual employment dates, reducing the risk of access lingering long after a seasonal employee’s last shift.
Network Capacity and Reliability Under Pressure
A network that performs fine under normal conditions can behave very differently once peak season traffic arrives. Slowdowns and outages during high volume periods don’t just frustrate customers, they can also create security blind spots as IT staff focus entirely on keeping systems running rather than monitoring for unusual activity.
Preparing Network Infrastructure for Peak Demand
- Conduct a pre season security audit that includes network capacity testing under simulated peak load
- Confirm redundant internet connections are in place in case a primary connection fails during high traffic periods
- Ensure store to store communication systems remain reliable even under heavy simultaneous usage
- Verify that monitoring tools remain active and effective even during traffic surges, rather than being overwhelmed alongside the network itself
Protecting Customer Data Beyond Payment Information
Customer data at risk during peak season extends well beyond payment card numbers. Retailers collect names, addresses, email addresses, purchase histories, loyalty program details, and sometimes even personal preferences, all of which carry value to attackers and carry real consequences if exposed.
Data Categories Requiring Protection
- Customer contact and shipping information
- Loyalty program account details and point balances
- Purchase history and personal shopping preferences
- Customer service communication records, including chat and email support logs
Customer record protection through consistent, tested backup practices ensures this information isn’t lost due to a technical failure, and encryption practices ensure it isn’t exposed even if a breach attempt does occur. Downtime prevention strategies applied specifically to customer facing systems reduce the chance that a technical failure during peak season turns into a larger data exposure event.
Third Party Vendor Risk During High Volume Periods
Retail businesses rely on a web of third party vendors during peak season: payment processors, shipping and fulfillment partners, marketing platforms, and inventory management integrations. Each of these connections represents a potential entry point if the vendor’s own security isn’t adequate.
Managing Vendor Risk
- Confirm that all third party vendors meet appropriate security and compliance standards before peak season begins
- Limit vendor access to only the specific systems and data needed for their function
- Review vendor contracts for clear security and data handling obligations
- Monitor vendor integrations for unusual activity, particularly during high transaction volume periods
Verified technology alliances matter here, since the retailers with the fewest peak season vendor related incidents are consistently the ones who vetted their partners carefully rather than adding new integrations quickly under time pressure.
Building an Incident Response Plan Before You Need One
Even with strong preventive measures in place, retail businesses should have a clear incident response plan ready before peak season begins. Discovering a security incident during the busiest week of the year is a difficult enough situation without also having to figure out a response process from scratch.
Elements of a Solid Incident Response Plan
- Clear roles defining who is responsible for which actions during an incident
- A communication plan for notifying customers, staff, and relevant authorities if required
- A tested process for isolating affected systems quickly without shutting down the entire operation unnecessarily
- A relationship already established with a security provider who can respond quickly rather than starting from zero
A proactive monitoring approach, where potential issues are flagged and investigated before they escalate, dramatically reduces the likelihood that an incident response plan ever needs to be activated in the first place.
The Pre Season Security Checklist
Retail businesses preparing for peak shopping season benefit from a structured checklist rather than an informal, last minute review. A practical starting list includes:
- Complete a full pre season security audit covering POS systems, network infrastructure, and ecommerce platforms
- Update all software, firmware, and plugins across every customer facing and back office system
- Review and tighten access permissions across all systems, especially ahead of seasonal hiring
- Test backup and recovery processes for customer data, transaction records, and inventory systems
- Confirm payment compliance documentation is current and complete
- Establish or refresh an incident response plan with clearly assigned responsibilities
Seasonal readiness checklists and on demand training videos covering these exact topics can help store managers and staff understand their specific role in maintaining security throughout the busiest weeks of the year.
Why This Work Pays for Itself
Security preparation before peak season often gets deprioritized in favor of inventory planning, marketing campaigns, and staffing logistics. This is understandable, but it overlooks how expensive a single security incident can be during exactly the period when a business is generating the largest share of its annual revenue.
The True Cost of a Peak Season Incident
- Direct financial loss from fraud or a ransomware payment
- Extended downtime during the highest revenue period of the year
- Regulatory penalties for payment compliance violations
- Long term reputational damage affecting customer loyalty well beyond the season itself
A true cost breakdown of proactive security investment versus reactive incident response consistently favors preparation, particularly once lost sales during downtime and long term customer trust are factored into the comparison.
Getting Ready With the Right Support
Retail businesses without a dedicated internal security team benefit significantly from bringing in outside expertise well ahead of peak season rather than during it. Retail specific security solutions account for the particular mix of POS systems, ecommerce platforms, and seasonal staffing patterns that generic IT support often overlooks.
Retail support bundles allow businesses to scale up monitoring and support specifically during high volume periods, then adjust back down once the season ends, rather than paying for a flat level of support year round that doesn’t match actual seasonal demand. Trusted retail partner relationships, built over multiple seasons rather than established for the first time under pressure, tend to produce far smoother outcomes when problems do arise.
Don’t Overlook the Basics
With so much focus on payment systems and ecommerce platforms, it’s easy to overlook simpler risks hiding in plain sight. Overlooked office risks, such as unsecured printers holding sensitive customer order details or unattended back office computers left logged in during busy shifts, remain a surprisingly common source of data exposure in retail environments.
A comprehensive approach considers every point where customer data passes through a system, not just the obvious ones like the checkout counter or the online cart.
Practical Steps to Take Before the Season Begins
Retail leadership looking to act now can start with a short, high impact list:
- Schedule a pre season security audit at least six to eight weeks before your peak period begins
- Confirm POS software updates and password changes are complete across every terminal
- Review current seasonal hiring plans against your access control and training processes
- Test your data backup and recovery process for customer and transaction records
- Verify vendor security standards for any new payment, shipping, or marketing integrations added this year
Firm history overview, verified technology alliances, and retail client examples can give business owners a clearer sense of what a properly prepared peak season looks like, based on real outcomes rather than assumptions.
Conclusion
Peak shopping season puts more pressure on retail technology and security than any other time of year, and the businesses that come through it without incident are almost always the ones who prepared months in advance rather than reacting once volume already increased. Point of sale security, ecommerce protection, payment compliance, seasonal staffing controls, and a tested incident response plan all play a role in keeping customer data safe when it matters most.
CMIT Solutions of Plano & Garland helps local retail operators get ready for peak season with a clear, practical security plan built around how retail businesses actually operate. If your peak season security review hasn’t happened yet this year, there’s still time to get it right. Schedule a consultation to start preparing before the rush arrives.
Frequently Asked Questions