Why AI Governance Is Becoming a Business Priority for Small and Mid Sized Companies
Artificial intelligence has moved from an experimental tool to a core part of daily business operations. Small and mid sized companies are using AI for customer service, marketing, data analysis, scheduling, and even hiring decisions. This rapid adoption has created a new challenge that many business owners did not anticipate: governance. Without a clear framework for how AI tools are selected, monitored, and controlled, businesses expose themselves to data privacy issues, compliance violations, security gaps, and reputational damage.
AI governance is no longer a concern reserved for large enterprises with dedicated compliance departments. Smaller organizations are now expected to demonstrate the same level of accountability, often with far fewer resources. This shift is why AI governance has quickly become a business priority rather than an afterthought, and why many companies are turning to a managed IT solutions provider to help them build a structured approach before problems arise.
This article explains what AI governance actually means, why it matters so much right now, and what small and mid sized businesses should be doing to prepare.
What Is AI Governance and Why It Matters Now
AI governance refers to the policies, procedures, and oversight mechanisms a company puts in place to control how artificial intelligence tools are used across the organization. It covers everything from which tools employees are allowed to use, to how data is fed into AI systems, to how outputs are reviewed before they influence business decisions.
Governance is not the same as simply having an AI policy document sitting in a drawer. It is an ongoing practice that includes:
- Identifying which AI tools are already in use across departments
- Setting clear rules for what data can and cannot be shared with AI platforms
- Reviewing AI generated content, decisions, or recommendations for accuracy and bias
- Assigning accountability for AI related outcomes
- Auditing AI systems on a regular schedule
The reason this matters now, rather than five years ago, is simple. AI tools have become accessible, affordable, and easy to adopt without technical expertise. Employees are signing up for free AI tools on their own, often without informing leadership. This creates what many IT professionals call shadow AI, a parallel version of the shadow IT problem that has existed for years. A reliable IT support partner can help identify these unauthorized tools before they create bigger issues.
The Shift: Why Small and Mid Sized Businesses Can No Longer Ignore AI Governance
For years, governance conversations were dominated by large corporations with legal teams and compliance officers. That has changed for several reasons.
AI adoption has outpaced oversight. Small businesses adopted AI tools quickly because they are inexpensive and easy to implement. Oversight structures, however, did not keep pace. Many companies are using AI in marketing, finance, and operations without anyone formally reviewing how those tools handle sensitive information.
Clients and partners are asking questions. Larger clients working with smaller vendors increasingly want assurance that AI is being used responsibly, especially when contracts involve shared data. A company that cannot answer basic questions about its AI practices risks losing business relationships.
Insurance providers are paying attention. Cyber insurance carriers have started asking detailed questions about AI usage during underwriting. Businesses without a documented approach to AI oversight may face higher premiums or denied claims.
Regulatory attention is increasing. State and federal discussions around AI accountability continue to expand, and businesses that wait until rules are finalized often find themselves scrambling to catch up. Building a foundation with strategic IT guidance now puts a company ahead of that curve rather than behind it.
Small and mid sized companies that treat AI governance as optional are taking on risk that is disproportionate to their size, since they typically have less capacity to absorb a data breach, a compliance fine, or a public trust issue.
Key Risks of Operating Without an AI Governance Framework
Ignoring AI governance does not eliminate risk, it simply delays when that risk becomes visible. Some of the most common consequences include:
- Data leakage, where employees paste confidential client information into public AI chat tools, unintentionally exposing it outside the company network
- Inaccurate or biased outputs, particularly in hiring, lending, or customer service decisions influenced by AI without human review
- Compliance violations, especially in industries already governed by strict data handling rules
- Vendor risk exposure, where third party software with embedded AI features processes data in ways the business never approved
- Reputational harm, if customers discover their information was used in ways they did not consent to
- Operational disruption, if an AI tool is suddenly restricted or banned and the business has no backup process
Each of these risks tends to compound over time. A single unmonitored AI tool might seem harmless at first, but as usage spreads across departments without oversight, the exposure grows significantly. This is one reason companies often pair governance efforts with an emerging security threats review, since AI risk and cybersecurity risk frequently overlap.
Regulatory and Compliance Pressures Driving the Change
Regulatory frameworks around artificial intelligence are still developing, but the direction is clear. Businesses are increasingly expected to show accountability for automated decision making, transparency around data usage, and the ability to explain how AI influenced a particular outcome.
Industries that already operate under strict data handling requirements, such as healthcare, finance, and legal services, are seeing AI oversight folded directly into existing compliance obligations. Even businesses outside these regulated industries are affected indirectly, since customers and partners in regulated sectors often require their vendors to meet similar standards.
Common compliance pressures include:
- Data residency and storage requirements when AI tools process information through third party servers
- Consumer privacy expectations around how personal data is used to train or inform AI systems
- Documentation requirements proving that AI outputs were reviewed by a human before being acted on
- Industry specific rules around automated decision making in hiring, credit, or healthcare contexts
Businesses that want to stay ahead of these pressures often start with a compliance challenges 2026 review to understand where their current practices fall short. Partnering with a provider offering dedicated compliance support services makes it far easier to keep policies current as expectations shift.
Core Components of a Strong AI Governance Framework
A practical AI governance framework does not need to be overly complex, especially for a small or mid sized business. The goal is to create clear, repeatable processes that anyone in the organization can follow.
- An AI usage policy This document outlines which tools are approved, what data can be entered into them, and who is responsible for approving new AI tools before they are adopted.
- A tool inventory A running list of every AI tool in use across the organization, including free tools employees may have adopted independently. This is often uncovered through an comprehensive IT assessment.
- Data classification rules Clear guidance on what qualifies as sensitive information, and firm rules preventing that data from being entered into public or unvetted AI platforms.
- Human oversight checkpoints Defined moments where a person must review AI output before it becomes final, particularly in decisions affecting customers or employees.
- Regular audits Scheduled reviews of AI tools, their outputs, and their data handling practices to confirm they still align with company policy.
- Vendor evaluation criteria A standard checklist used before adopting any new software that includes AI features, ensuring the vendor’s data practices meet company standards.
- Incident response procedures A plan for what happens if an AI tool produces a harmful output, leaks data, or is compromised, similar to existing network support value planning already used for broader IT incidents.
Data Privacy and Security in the Age of AI
AI governance and cybersecurity are deeply connected. Many of the biggest risks tied to AI adoption are, at their core, data protection problems. When an employee enters client information into an AI chatbot to draft a quick email, that data may be stored, processed, or even used to train the underlying model, depending on the platform’s terms of service.
Strong data privacy practices in an AI context typically include:
- Restricting which categories of data can be entered into AI tools
- Using enterprise grade AI platforms with contractual data protections rather than free consumer versions
- Encrypting sensitive data both in transit and at rest
- Monitoring for unusual data movement that could indicate information is leaving the network through an unapproved channel
- Maintaining strong cybersecurity protection services that extend specifically to AI platforms and integrations
Because many AI tools rely on cloud infrastructure to function, businesses also need to evaluate how their secure cloud services provider handles data segmentation and access control. A governance framework that ignores the cloud layer leaves a significant gap in overall protection. Companies exploring this connection often review how AI driven protection tools are reshaping traditional security models altogether.
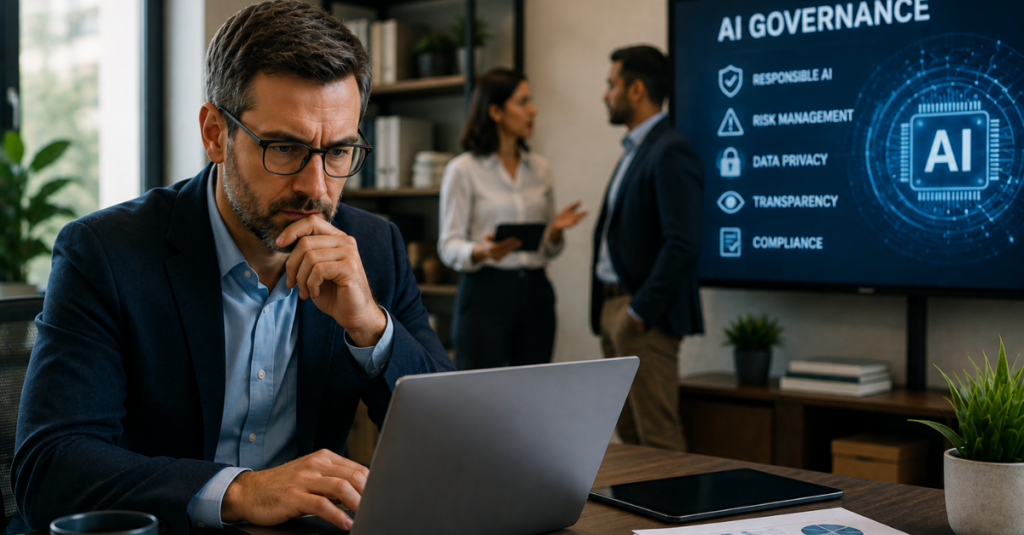
Building an AI Governance Policy: Step by Step
Creating a governance policy from scratch can feel overwhelming, but breaking it into stages makes the process manageable for a smaller team.
Step 1: Assess current AI usage. Survey departments to understand which tools are already in use, formally or informally. An AI readiness evaluation is a practical way to capture this picture accurately.
Step 2: Define acceptable use. Decide which tools are approved, what data can be shared with them, and what tasks are appropriate for AI assistance versus tasks that require full human control.
Step 3: Assign ownership. Someone in the organization, whether an internal leader or an outside partner, needs to own AI governance the same way someone owns cybersecurity or compliance.
Step 4: Train employees. Policies only work if people understand them. Training should cover practical examples of what is and is not acceptable when using AI tools at work.
Step 5: Monitor and audit continuously. Governance is not a one time project. Scheduled reviews ensure the policy keeps pace with new tools and evolving risks.
Step 6: Adjust based on findings. As new AI tools emerge or business needs change, the policy should be updated rather than left static.
Businesses that want a faster starting point often bring in outside expertise through AI integration services designed specifically to help smaller companies build these frameworks without needing an internal compliance department.
Role of a Managed IT Partner in AI Governance
Most small and mid sized businesses do not have the internal resources to build and maintain an AI governance program alone. This is where a managed IT partner becomes valuable, not just for technical support, but for structured oversight.
A capable partner typically helps with:
- Conducting a full inventory of AI tools already in use across the business
- Reviewing existing network management solutions to identify where AI tools connect into company systems
- Setting up monitoring to flag unauthorized AI tool usage
- Advising on which AI platforms offer appropriate data protection guarantees
- Coordinating governance policies with existing data backup solutions to ensure AI generated content and decisions are properly preserved for audit purposes
- Supporting ongoing training so employees understand acceptable AI use
This kind of partnership takes the burden off business owners who are already managing daily operations, sales, and customer relationships. It also means governance decisions are made with technical expertise rather than guesswork, reducing the chance of costly mistakes down the road.
Cloud Infrastructure and AI Governance
Nearly every modern AI tool depends on cloud infrastructure to store data, process requests, and deliver results. This makes cloud strategy an inseparable part of any serious AI governance effort.
Businesses should evaluate:
- Where their cloud provider physically stores data and whether that aligns with any regulatory requirements
- How access controls are configured to prevent unauthorized use of AI connected systems
- Whether cloud environments are properly segmented so that a breach in one area cannot spread across the entire network
- How backup and recovery processes account for AI generated data and decisions
Companies going through cloud modernization often review cloud migration trends alongside their AI governance planning, since the two efforts naturally intersect. Similarly, businesses scaling operations frequently look at cloud scaling benefits as part of a broader modernization strategy that includes responsible AI adoption from the start.
Employee Training and Internal AI Policies
Even the strongest governance framework fails if employees are not aware of it or do not understand why it matters. Training should be practical, ongoing, and tailored to how different departments actually use AI tools.
Effective training programs typically include:
- Clear examples of what information should never be entered into an AI tool
- Guidance on how to verify AI generated content before using it externally
- Instructions for reporting new AI tools before adopting them
- Reminders about how AI usage connects to broader productivity tools setup already in place across the organization
Training works best when it is treated as an ongoing conversation rather than a single meeting. Short refreshers every quarter, paired with updates whenever new tools or risks emerge, keep the policy relevant instead of something employees forget after the first week.
Vendor and Third Party AI Tool Risks
Many businesses unknowingly inherit AI risk through the software they already use. Customer relationship management platforms, accounting software, and communication tools have quietly added AI features, often without a clear explanation of how data is processed behind the scenes.
Before adopting or continuing to use any vendor with embedded AI features, businesses should ask:
- Does the vendor disclose how AI features process and store data
- Can the AI features be disabled if they do not meet company standards
- Does the vendor allow an opt out from having company data used to train their models
- What certifications or industry certifications partners does the vendor hold that demonstrate accountability
This vendor evaluation process becomes especially important when reviewing unified communication systems, since many platforms now include AI powered transcription, summarization, and analytics features that touch sensitive conversations. Businesses transitioning away from outdated systems often compare legacy phone systems against modern platforms specifically to understand these new AI related considerations.
Cost of Ignoring AI Governance vs Proactive Planning
Some business owners view governance as an unnecessary expense, but the cost comparison tells a different story. A single data exposure incident tied to unmonitored AI usage can result in client loss, legal fees, regulatory fines, and significant time spent on remediation.
Proactive governance, by comparison, is a relatively modest ongoing investment. Many businesses that already understand managed IT costs find that adding AI oversight to an existing managed IT relationship is far less expensive than building a program from scratch after an incident occurs.
Consider the comparison:
- Reactive cost: incident investigation, legal consultation, client notification, potential regulatory fines, and reputational repair
- Proactive cost: policy development, employee training, ongoing monitoring, and periodic audits
The proactive path is not only cheaper, it also protects the trust that clients and partners place in the business. That trust is often what separates a small competitor from a larger one, and losing it can be far more damaging than any direct financial cost.
How CMIT Solutions of Plano & Garland Supports AI Governance
Small and mid sized businesses in the Plano and Garland area do not need to navigate AI governance alone. CMIT Solutions of Plano & Garland works with local businesses to build governance frameworks that fit their size, industry, and risk tolerance, without the complexity typically associated with enterprise compliance programs.
Support typically includes:
- A full review of current IT upgrade trends affecting the business and how AI adoption fits into that broader picture
- Identifying unauthorized or shadow AI tools already in use
- Establishing data classification and acceptable use policies
- Coordinating governance with existing managed detection response systems already protecting the network
- Reviewing service package options to find the right level of ongoing support
- Sharing client success stories from other local businesses that have implemented similar frameworks
- Offering additional IT resources and helpful IT tools to help business owners evaluate their own AI risk exposure
- Hosting educational webinar sessions that break down governance concepts in plain language
Businesses that want to understand more about the broader philosophy behind this approach can review our proven approach or learn our story to see how local, hands on support differs from generic national providers.
Conclusion
AI governance has moved quickly from a niche compliance topic to a genuine business priority for small and mid sized companies. The tools driving productivity gains today are the same tools capable of creating serious data privacy, security, and compliance risks if left unmanaged. Businesses that build a clear governance framework now, covering tool inventory, acceptable use, data protection, and ongoing training, position themselves to use AI confidently rather than cautiously.
Waiting until a problem occurs is far more costly than building the right structure today. If your business is ready to put a practical AI governance plan in place, schedule a consultation with the team at CMIT Solutions of Plano & Garland to get started: schedule a consultation.
Frequently Asked Questions