Franchise businesses have a structural problem most owners never think about until it’s too late: they’re built for consistency in branding, service, and customer experience, but that same structure often creates enormous inconsistency in technology and security. A single franchise brand might have dozens of locations, each with its own local network, its own point-of-sale system, its own staff turnover, and sometimes its own informal approach to IT. Attackers have noticed, and they’ve adjusted their tactics accordingly.
This isn’t a theoretical risk. Franchise and multi-location businesses have become increasingly attractive targets precisely because of how they’re structured, not despite it. Understanding why requires looking past the brand-level marketing and into the messy technical reality of how most franchise networks actually operate behind the scenes.
Why Franchise Structure Creates Security Gaps by Design
At the corporate or franchisor level, security policies might look solid on paper. Written cybersecurity requirements, recommended vendors, and compliance checklists often exist in some form. The problem is what happens once those policies reach the individual franchisee level, where enforcement, budget, and technical expertise vary enormously from one location to the next.
- Inconsistent enforcement. A franchisor can publish security requirements, but without active oversight, individual locations often implement them loosely, partially, or not at all.
- Local ownership, local decisions. Franchisees frequently make their own IT purchasing decisions, leading to a patchwork of different software, hardware, and security tools across a single brand.
- Varying technical expertise. Some franchise owners have IT backgrounds or dedicated staff. Many don’t, and security often falls to whoever is available, not whoever is qualified.
- Budget disparities. A struggling location might cut corners on security spending long before it cuts corners on visible customer-facing expenses.
This pattern connects directly to what’s explored in discussions of multi location IT challenges, where rapid expansion often outpaces the technical infrastructure needed to support it safely.
The Weakest Link Problem, Multiplied
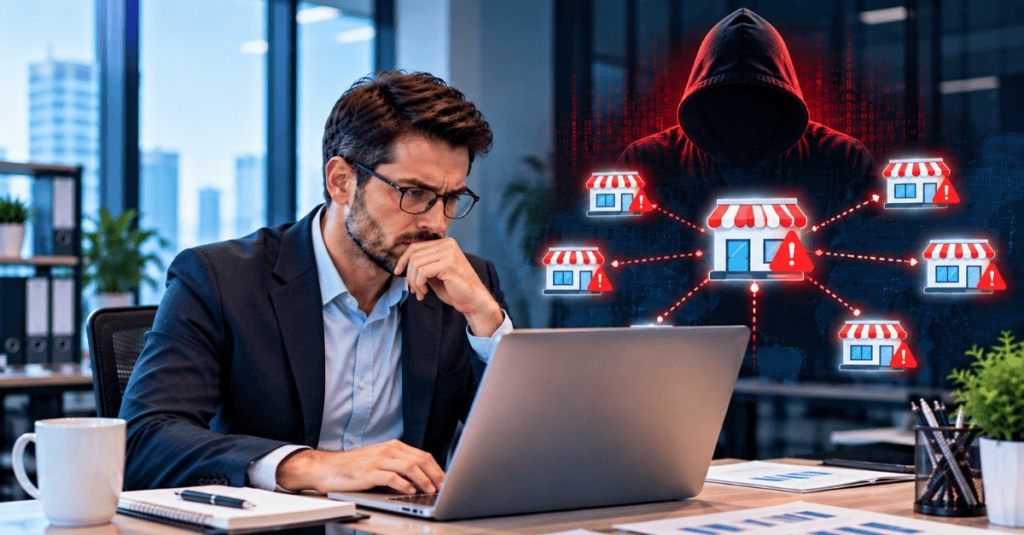
In any organization, security is often described as being only as strong as its weakest link. Franchise networks take that principle and multiply it across dozens or hundreds of locations, any one of which can become the entry point for an attack that affects the entire brand.
- A single unpatched point-of-sale system at one location can expose customer payment data across the network if systems are interconnected
- A phishing email opened by an untrained employee at one franchise can lead to credential theft that compromises shared corporate systems
- An unsecured local Wi-Fi network at one location can give attackers a foothold that eventually reaches centralized customer databases or financial systems
- A franchisee using outdated, unsupported software can introduce vulnerabilities that a fully updated corporate system would never have
This is precisely why multi location consistency has become such a central challenge for franchise brands trying to scale without accumulating security debt at every new location they open.
Why Attackers Specifically Target Franchise Networks
Cybercriminals don’t randomly stumble onto franchise businesses. Increasingly, they specifically look for them, for a few calculated reasons.
- One vulnerability, many targets. A weakness in a commonly used franchise software platform or vendor can potentially be exploited across every location using that same system, multiplying the payoff for a single successful attack.
- Valuable, centralized data. Franchise networks often centralize customer payment information, loyalty program data, and employee records, creating an appealing target even if individual locations seem small.
- Predictable technology stacks. Many franchise brands require or recommend the same point-of-sale systems, scheduling software, and management tools across all locations, meaning attackers who successfully breach one location often understand exactly how to breach the next.
- Lower security maturity than perceived. Attackers know that despite a recognizable, trusted brand name, the actual security posture at the individual location level is often far weaker than customers assume.
This trend lines up closely with the business model behind ransomware as a service, where attackers rent out tools and infrastructure specifically designed to scale across many similar, smaller targets rather than focusing effort on a single large enterprise.
Point-of-Sale Systems: A Franchise-Specific Vulnerability
Few technologies illustrate the franchise security gap as clearly as point-of-sale systems. These systems handle sensitive payment data every single day, across every location, and they’re frequently overlooked in broader security conversations that focus on office networks and email systems instead.
- Outdated POS software running unsupported versions with known vulnerabilities
- Default or weak administrative credentials left unchanged since installation
- POS systems connected to the same network as general business Wi-Fi, rather than properly segmented
- Inconsistent patching schedules across locations, since updates are often left to individual franchisees rather than centrally managed
Given how directly this touches customer trust, secure payment processing needs to be treated as a franchise-wide priority rather than something each location handles independently and inconsistently.
The Endpoint Sprawl Problem
Every franchise location adds new devices to the overall network: point-of-sale terminals, back-office computers, tablets for ordering or scheduling, security cameras, and increasingly, personal devices used by managers and staff. Each of these represents a potential entry point, and few franchise networks track them all consistently.
- Devices purchased locally without corporate IT involvement or oversight
- Personal devices used for scheduling, communication, or even payment processing
- Security cameras and other connected devices running default settings and rarely updated firmware
- Former employee accounts and device access that never gets properly revoked after staff turnover
This kind of unmanaged endpoint sprawl is exactly what’s described in discussions of overlooked endpoint threats, where the sheer number of connected devices across a franchise network often outpaces any centralized ability to monitor or secure them properly.
Staff Turnover as a Security Risk
Franchise locations, particularly in retail and food service, often experience high employee turnover. While this is a well-known operational challenge, its security implications are frequently underestimated.
- New employees are often trained quickly, with security awareness getting minimal attention compared to customer service and operational procedures
- Shared logins and generic accounts are common shortcuts at the location level, making it difficult to track who accessed what
- Departing employees don’t always have their access revoked promptly, leaving old credentials active far longer than they should be
- Seasonal or part-time staff may receive even less security training than full-time employees, despite having similar system access
This human element compounds the technical gaps already present, creating what’s often described as growing leadership blind spots, where corporate leadership assumes a level of security awareness and consistency at the location level that simply doesn’t match reality on the ground.
Vendor Sprawl Across a Franchise Network
Franchise brands often work with multiple technology vendors across payment processing, scheduling, marketing, inventory management, and more. Each additional vendor relationship introduces another potential point of failure, and few franchise networks maintain clear ownership over vendor security practices.
- Multiple vendors with access to different pieces of customer or operational data
- Inconsistent security standards required of vendors from one contract to the next
- Limited visibility into how thoroughly each vendor protects the data it handles
- No single owner responsible for auditing vendor security across the entire network
This exact dynamic is explored in depth in discussions of vendor sprawl ownership, where the accumulation of vendor relationships over time quietly erodes accountability, leaving nobody clearly responsible when something goes wrong.
The Compliance Complexity Franchise Networks Face
Depending on the industry, franchise businesses often carry compliance obligations tied to payment card data, customer privacy, and sometimes health or safety regulations. Managing this consistently across dozens of independently operated locations adds significant complexity.
- Payment Card Industry standards apply at every location processing customer payments, not just at the corporate level
- Data privacy regulations may apply differently depending on the states or regions where individual locations operate
- Documentation and audit readiness often exist at the corporate level but aren’t consistently replicated at the franchisee level
- A compliance failure at a single location can create legal and reputational exposure for the entire brand
This complexity is a major reason why compliance first strategies are becoming increasingly important for franchise brands trying to maintain consistent standards across every location they operate.
Why a Breach at One Location Threatens the Entire Brand
Perhaps the most underestimated risk in franchise cybersecurity is reputational. Customers rarely distinguish between individual franchise locations and the brand as a whole. A data breach at a single location, whether it involves stolen payment information or a public ransomware incident, becomes a story about the entire brand, not just that one address.
- News coverage of a breach typically references the brand name, not the specific franchisee
- Customers affected at one location may lose trust in the brand broadly, avoiding other locations entirely
- Franchisees at unaffected locations can suffer reputational and financial fallout from an incident they had no part in
- Franchisor relationships with other current or prospective franchisees can be damaged if the brand’s overall security reputation suffers
This shared exposure is exactly why escalating cyber risks need to be addressed at the network level, not left to individual franchisees to manage entirely on their own.
What Franchisors Can Do to Close These Gaps
Addressing franchise-wide cybersecurity risk requires more than publishing a policy document and hoping every location follows it. Franchisors that take this seriously tend to build structure and support directly into their operational model.
- Standardize core technology. Requiring consistent, vetted point-of-sale systems, network equipment, and security tools across all locations reduces the patchwork problem significantly.
- Centralize monitoring where possible. Even with independently owned locations, centralized visibility into security events across the network catches problems faster than relying on each location to self-report.
- Build security into onboarding. New franchisee onboarding should include clear, enforced technology and security requirements, not optional suggestions.
- Offer ongoing support, not just initial setup. Security requirements that aren’t actively supported over time tend to erode as staff change and equipment ages.
- Audit regularly, not just once. Periodic security reviews across locations catch drift before it becomes a serious vulnerability.
Franchise brands that partner with an experienced managed IT services provider often find it far easier to maintain this kind of consistency across multiple locations than trying to coordinate it entirely through internal, often stretched-thin corporate IT resources.
What Individual Franchisees Can Do Right Now
Waiting for corporate-level policy changes isn’t the only option available to individual franchise owners concerned about their own location’s exposure. Several steps can meaningfully reduce risk at the local level.
- Ensure point-of-sale and back-office systems are running current, supported software versions
- Separate customer-facing Wi-Fi networks from internal business systems entirely
- Require unique logins for each employee rather than shared or generic accounts
- Revoke access immediately when an employee leaves, without delay
- Invest in basic employee security awareness training, even brief, regular refreshers
- Work with network management services that understand the specific technical needs of a retail or service location environment
The Case for Zero Trust in a Franchise Environment
Because franchise networks are inherently distributed, with many independently managed locations connecting to shared brand resources, the traditional idea of a trusted internal network breaks down quickly. A device or user shouldn’t be automatically trusted just because it’s connected to a particular location’s network.
Applying a zero trust security model across a franchise network means verifying every device and user attempting to access shared systems, regardless of which location they’re connecting from. This approach is particularly well suited to franchise structures, where the number and diversity of connection points make blind trust in any single network segment especially risky.
Modern Detection Matters More in Distributed Networks
Traditional antivirus software, installed individually at each location with no centralized visibility, struggles to keep pace with how quickly modern attacks spread across interconnected systems. Franchise networks benefit significantly from centralized, continuous monitoring that can catch unusual activity at any location in near real time.
This is where modern MDR solutions offer a meaningful advantage over the patchwork antivirus approach many franchise locations still rely on independently. Centralized detection means a suspicious login attempt or unusual data transfer at one location can be caught and investigated before it spreads to others, an advantage reflected in broader conversations about replacing traditional antivirus with detection systems built for exactly this kind of distributed environment.
Identity Verification Across a Distributed Workforce
With staff constantly rotating across shifts, locations, and sometimes even between franchise units, verifying identity rather than relying on network location or device trust becomes especially important. Franchise networks benefit from embracing identity first security principles, supported by biometric MFA solutions that reduce reliance on shared passwords, which are notoriously common and difficult to track across high-turnover retail and service environments.
Managing Personal Devices Across Locations
Many franchise employees, particularly managers, use personal phones or tablets for scheduling, communication, or even payment processing during busy periods. Without clear policy and technical safeguards, this creates yet another inconsistent entry point across the network. Establishing secure BYOD policies that apply consistently across every location, rather than being left to individual manager discretion, closes a gap that’s easy to overlook amid the daily pressures of running a location.
Why Preparation Matters More Than Reaction in Franchise Networks
Given how quickly a security incident at one location can spread reputational and financial damage across an entire brand, franchise networks benefit enormously from proactive ransomware readiness planning built at the network level rather than assuming each location will handle its own preparation independently. Waiting for an incident to expose these gaps almost always costs significantly more, in both money and trust, than addressing them proactively.
This proactive posture also helps counter the quiet accumulation of digital fragility risks that tend to build up across sprawling, inconsistently managed networks until a single incident exposes just how fragile the underlying infrastructure really was.
Building a Consistent Security Foundation Across Every Location
Ultimately, closing the franchise security gap comes down to treating technology and security as core parts of the franchise model, not an afterthought left entirely to individual owners. This includes standardized cybersecurity services applied consistently across locations, centralized compliance management services that keep every location audit ready, and reliable IT support services available to franchisees who may not have dedicated technical staff of their own.
How CMIT Solutions of Austin Downtown West Supports Franchise Networks
Franchise businesses need a security approach that scales with them, not one that has to be rebuilt from scratch at every new location. CMIT Solutions of Austin Downtown West works with franchise owners and multi-location businesses to build consistent, centrally supported technology and security practices, backed by strategic IT guidance that accounts for the unique operational realities of running multiple locations under one brand.
Whether it’s standardizing point-of-sale security, closing endpoint gaps, or building consistent compliance practices across every location, CMIT Solutions of Austin Downtown West helps franchise networks reduce the kind of inconsistency that attackers count on to find their way in.
Final Thoughts
Franchise businesses aren’t more vulnerable to cyberattacks because of anything inherently wrong with the franchise model itself. They’re vulnerable because rapid growth, distributed ownership, and inconsistent enforcement create exactly the kind of gaps attackers are looking for. Closing those gaps requires treating security as a shared, network-wide responsibility rather than something left entirely to individual locations to figure out on their own.
If your franchise network wants a clearer picture of where security consistency might be breaking down across locations, schedule a consultation to review your current setup before an attacker finds the weakest link first.
Frequently Asked Questions