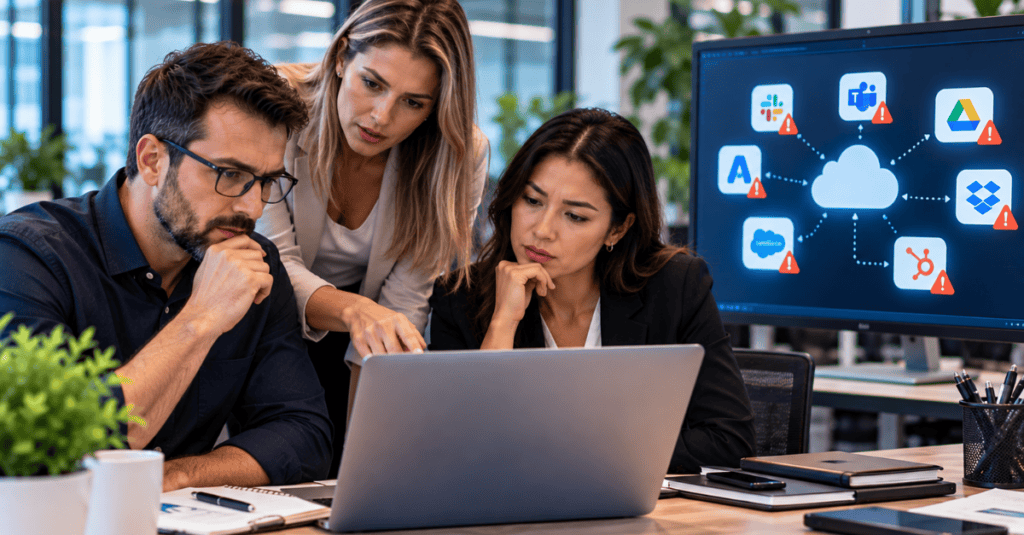
Most businesses have far more software running across their organization than their IT team actually knows about. A marketing employee signs up for a free trial of a design tool to finish a project quickly. A sales rep connects a scheduling app to their calendar without asking anyone. A finance team member starts using an AI writing assistant to draft reports, pasting client data in along the way. None of these decisions feel risky in the moment, but together they create a sprawling network of unmanaged software quietly holding company data outside of any central oversight.
This is the reality of SaaS sprawl in 2026, and it has become one of the more overlooked cybersecurity blind spots facing small and midsize businesses. Cloud-based software is easier than ever to sign up for, often requiring nothing more than a work email address and a credit card, which means employees can bypass IT entirely without any bad intent. The problem is not that people are trying to create risk. It is that the tools have made it effortless to introduce risk without realizing it.
What makes this especially difficult to manage is that traditional security tools were largely built to protect a defined network perimeter, not a scattered collection of independently adopted cloud subscriptions each with their own login, their own data storage practices, and their own security track record. A firewall cannot flag a risky SaaS signup the same way it can flag a suspicious file download, which means many of the tools businesses already rely on for protection simply were not designed to catch this particular category of exposure. For businesses in Plano and Garland, understanding where this sprawl comes from and how to bring it under control has become a genuinely important part of protecting company data.
What Actually Counts as Unmanaged SaaS
Unmanaged SaaS, often called shadow IT, refers to any cloud application being used for business purposes without formal approval, visibility, or oversight from the IT team. This covers a wider range of tools than most business owners initially assume, and the category has grown considerably as more everyday tasks have moved to browser-based platforms.
Common examples include:
- File sharing and storage tools used to move documents outside approved company systems
- Free project management or note-taking apps adopted by individual teams without company-wide review
- Browser extensions that request access to email, files, or browsing activity
- Personal AI chat tools used for work tasks without any data handling agreement in place
- Communication platforms set up informally for a single project and never decommissioned
None of these tools are inherently malicious, and many genuinely help employees get work done faster. The risk comes from the fact that nobody responsible for security knows these tools exist, which means nobody is verifying how they store data, who else has access to it, or what happens to that data if the vendor experiences a breach of their own.
Why SaaS Sprawl Has Exploded
A few forces have combined to make this problem far bigger than it was even a couple of years ago. Software vendors have made signup frictionless, often offering generous free tiers specifically designed to get individual users hooked before ever involving a procurement process. Remote and hybrid work has also normalized employees choosing their own tools to solve immediate problems, since there is rarely a colleague physically nearby to notice or question the decision.
Reviewing broader growing cyber risks shows that attackers have taken notice of this trend, increasingly targeting smaller, less secure SaaS platforms as a way to reach the larger organizations connected to them. A vendor with weak security practices handling data for hundreds of small businesses represents an efficient target for criminals looking for a single point of entry into many organizations at once.
Budget pressure plays a role too. Departments under pressure to move quickly often find it faster to expense a fifteen dollar monthly subscription than to wait for a formal IT procurement process, especially in businesses where that process feels slow or bureaucratic. The result is a steady, largely invisible accumulation of tools that nobody set out to create but that now represents real exposure.
The Hidden Risks of Unapproved Apps
The consequences of unmanaged SaaS rarely show up immediately, which is part of why the problem persists for so long in most organizations. Instead, the risks tend to surface later, often during an incident, an audit, or a vendor’s own breach disclosure that suddenly reveals company data was stored somewhere nobody expected.
Some of the most common risks include:
- Sensitive data stored on platforms with weak or unknown security practices
- No visibility into who still has access after an employee leaves the company
- Data residency issues, where information ends up stored in locations that violate client contracts or regulatory requirements
- Increased phishing risk, since each additional login represents another opportunity for credential theft
- Duplicate or conflicting versions of important documents scattered across disconnected platforms
A zero trust principles approach helps address some of this by requiring continuous verification regardless of which platform a login is coming from, but it works best when paired with actual visibility into what platforms exist in the first place. You cannot apply consistent security controls to tools you do not know are being used.
Data Exposure Through Disconnected Tools
One of the more subtle risks of SaaS sprawl involves how data moves between approved systems and unmanaged ones without anyone tracking it. An employee might export a client list from an approved CRM into a personal spreadsheet tool to build a quick report, then forget to delete that export once the report is finished. Multiply that pattern across dozens of employees over months or years, and businesses end up with sensitive data copies living in places far removed from any centralized protection.
This kind of exposure is particularly difficult to catch because it does not look like a security incident from the outside. Nothing was hacked, and no alarm went off. The data simply moved to a place where it is no longer protected by the same access controls, encryption standards, or backup procedures that the original system had in place. Establishing approved productivity software standards, combined with clear guidance on how data should and should not move between platforms, closes much of this gap before it becomes a habit employees fall back on repeatedly.
Compliance Implications of Shadow SaaS
Regulated businesses face a sharper version of this problem, since compliance frameworks generally require organizations to know exactly where sensitive data lives and to demonstrate that appropriate protections are in place. Unmanaged SaaS tools make that demonstration nearly impossible, since by definition nobody responsible for compliance knew the tool was in use in the first place.
Working through compliance risk management as part of a broader SaaS governance program helps businesses close this gap before an audit reveals it. Reviewing the must have safeguards that regulators and cyber insurance carriers increasingly expect shows that SaaS visibility and vendor risk management are becoming standard requirements rather than optional best practices, particularly for firms handling financial, health, or legal data.
Building a SaaS Discovery and Governance Process
Bringing unmanaged SaaS under control does not require banning every tool employees have adopted on their own. A more realistic goal is establishing visibility and a lightweight approval process that employees will actually follow rather than work around.
A workable discovery and governance process typically includes:
- Conducting a full inventory of SaaS tools currently in use across the organization
- Reviewing network and identity logs to identify applications employees are logging into with company credentials
- Categorizing discovered tools by risk level based on the type of data they can access
- Establishing a simple, fast approval path for new tools so employees are not tempted to bypass the process
- Setting a recurring review cycle to catch new tools before they become deeply embedded in daily workflows
A SaaS stack audit often surfaces more than just security gaps too, frequently revealing redundant subscriptions and unused licenses that are quietly costing the business money every month alongside the security exposure they create.
Vendor Risk Management for Approved Applications
Bringing a tool into the approved category does not mean the risk conversation is over. Every SaaS vendor represents a third-party risk that needs periodic review, since a vendor’s security posture can change over time, and a tool that was reasonably secure at adoption may not stay that way without ongoing attention. Understanding cloud adoption trends across the industry helps businesses evaluate whether their current vendor list still reflects best practices or whether newer, more secure alternatives have emerged.
A practical vendor review process should look at how each provider handles data encryption, where data is physically stored, what their breach notification process looks like, and whether they undergo independent security audits. Businesses handling particularly sensitive data should weight this review more heavily toward vendors with established compliance certifications relevant to their industry, rather than choosing tools based purely on features or price.
The Employee Habits That Quietly Drive Shadow IT
Understanding why employees turn to unapproved tools in the first place makes it much easier to fix the underlying problem rather than just policing the symptoms after the fact. In most cases, shadow IT emerges from a genuine effort to solve a real problem quickly, not from any intent to create risk. An employee frustrated by a slow, clunky approved tool will often find a faster alternative on their own within minutes.
This points to a practical lesson for businesses building out governance programs. If the approved toolset does not actually meet employee needs, shadow IT will keep reappearing no matter how strict the written policy sounds. Investing in proactive monitoring benefits alongside a genuinely responsive process for evaluating new tool requests addresses the root cause far more effectively than a policy document alone ever could.
Cloud and Network Visibility as the First Line of Defense
Discovering unmanaged SaaS tools requires actual visibility into network and identity activity, not just relying on employees to self-report what they are using. Businesses that lack this visibility are essentially guessing at what exists in their environment, and guessing is not a reliable foundation for security decisions involving sensitive data.
Strong cloud security oversight paired with network visibility tools gives IT teams the ability to see which applications employees are actually connecting to, often surfacing dozens of tools that were never part of any formal conversation. This kind of visibility also supports a more responsive network security audit process, since new tools can be caught and reviewed shortly after adoption rather than discovered months or years later during an unrelated investigation.
Backup Gaps Created by Scattered SaaS Tools
Every additional SaaS platform in use represents another place where important company data lives, and most of these platforms are not covered by a business’s central backup strategy. If a project management tool an employee started using independently gets deleted, suspended, or breached, there is often no backup at all protecting the data stored there, since it was never included in the organization’s formal backup planning.
This gap becomes particularly relevant when considering how many businesses already misunderstand backup coverage for tools they do use officially. The subscription backup gap affecting well-known platforms like Microsoft 365 is only magnified across the dozens of lesser-known tools that make up a typical organization’s shadow IT footprint. Ensuring automated data protection extends to every approved platform, and not just the handful of core systems everyone thinks of first, closes a gap that often goes unnoticed until data is already lost.
AI Tools Adding a New Layer to the Sprawl Problem
Artificial intelligence tools have added an entirely new dimension to shadow IT over the past couple of years. Employees experimenting with free AI writing assistants, image generators, or chatbots often paste real company data into these platforms without a second thought, unaware of how that data might be stored, used to train future models, or exposed through the vendor’s own security gaps.
Establishing responsible AI policies as part of the broader SaaS governance effort addresses this specific risk directly, giving employees clear guidance on which AI tools are approved for business use and what types of data should never be entered into any AI platform, approved or otherwise. Reviewing available AI powered tools through an AI adoption assessment helps businesses offer employees legitimate, secure alternatives rather than leaving them to find their own AI tools independently, which is often exactly how this category of shadow IT begins in the first place.
Building an Ongoing SaaS Security Program
Bringing SaaS sprawl under control is not a one-time project. New tools appear constantly, and a governance program that is not maintained will quietly drift back toward the same blind spots within months. A sustainable program includes:
- Quarterly reviews of newly discovered applications through network and identity monitoring
- Clear off-boarding procedures ensuring departing employees lose access to every platform, not just core company systems
- Regular vendor risk reassessments for tools already on the approved list
- A simple, well-communicated process for employees to request new tools without long delays
- Periodic training reminding staff why the process exists and how it protects both the company and their own work
Businesses managing this kind of ongoing effort often benefit from tiered support packages that scale monitoring and governance alongside the business as its software footprint grows, rather than trying to build and maintain this capability entirely in-house.
Why Plano and Garland Businesses Need a Partner for SaaS Governance
Managing SaaS sprawl requires a combination of technical visibility tools and ongoing human attention that many internal IT teams, particularly at smaller businesses, simply do not have the bandwidth to sustain alongside everything else on their plate. This is exactly the kind of gap where outside support makes a measurable difference.
CMIT Solutions of Plano & Garland helps local businesses discover the unmanaged software already running across their organization, bring it under proper governance, and build a sustainable process for reviewing new tools going forward. This includes outsourced IT management that treats SaaS discovery as an ongoing responsibility rather than a one-time cleanup project, along with vendor procurement oversight that keeps new software purchases aligned with existing security and compliance standards from the start. The team at CMIT Solutions of Plano & Garland also provides technology strategy guidance to help leadership understand where SaaS risk sits alongside other technology priorities.
Businesses weighing their options can review our service background supporting local organizations through this exact kind of technology governance work, or explore what makes for a dependable technology partner capable of handling both the technical discovery work and the ongoing policy conversations that keep SaaS sprawl from creeping back in. A regional IT partner with direct experience across Plano and Garland businesses understands the specific software patterns common to local industries, which speeds up the discovery process considerably compared to starting from scratch.
SaaS Governance Fits Into a Larger Security Picture
Unmanaged software rarely exists in isolation from the rest of a business’s technology environment, which is why SaaS governance tends to work best as part of a broader security program rather than a standalone initiative. Comprehensive threat protection that already monitors for unusual login activity and credential misuse naturally extends to catch many of the warning signs shadow IT tends to create, since the underlying risk patterns overlap considerably.
Day-to-day support also plays a role here. Dedicated helpdesk services give employees a fast, easy place to request a new tool through proper channels, which removes much of the temptation to sign up independently just to avoid a slow process. Understanding the true managed IT ROI of this kind of support often includes the reduced risk and license waste tied directly to reining in SaaS sprawl, even though that connection is not always obvious at first glance.
The network itself deserves attention too. Recognizing network backbone importance helps businesses understand why consistent monitoring across every connected system, not just the handful everyone thinks of first, is what actually catches shadow IT before it becomes deeply embedded. Consolidating collaboration through unified team collaboration platforms further reduces the number of scattered tools employees might otherwise reach for individually. Even overlooked physical risks matter here, since office equipment risks tied to connected devices are frequently left out of software-focused security conversations entirely, despite representing another entry point into the same network that SaaS tools connect to.
Bringing It All Together
SaaS sprawl has quietly become one of the more significant blind spots in business cybersecurity, not because any single unapproved tool is especially dangerous, but because the accumulated total across an organization represents far more exposure than most leadership teams realize. Bringing this under control does not require banning innovation or making employees jump through unnecessary hoops. It requires real visibility, a lightweight approval process people will actually use, and ongoing attention as the software landscape keeps shifting month to month.
Getting a clear picture of what is actually running across your organization is the first step toward closing this gap, and it does not have to be a disruptive process. Plano and Garland businesses ready to uncover their unmanaged software footprint and build a sustainable governance process around it can start with a conversation about where things currently stand. Schedule a consultation to get a clear picture of your SaaS environment and a practical plan for securing it.
Frequently Asked Questions