Passwords have been the default way to log into business systems for decades, and they have also been the leading cause of account takeovers for just as long. Weak passwords, reused passwords, and stolen passwords sit behind a huge share of the breaches reported every year, no matter how many complexity rules or reset reminders companies add on top. That track record is why passkeys have moved from a niche security experiment to something major platforms like Microsoft, Google, and Apple are now pushing businesses to adopt directly.
Passkeys replace the traditional username and password combination with cryptographic key pairs tied to a physical device, removing the shared secret that criminals have exploited for years. There is nothing to phish, nothing to guess, and nothing sitting in a leaked database waiting to be reused somewhere else. For small and midsize businesses in Plano and Garland, this shift represents one of the more practical security upgrades available right now, since it reduces risk without necessarily requiring a complete overhaul of existing systems.
What makes this moment different from earlier passwordless attempts is that the underlying technology is now genuinely mature and widely supported. Earlier efforts at removing passwords often relied on proprietary hardware tokens or clunky software that never gained real traction outside of large enterprises. Passkeys, by contrast, are built on an open standard supported across nearly every major operating system and browser, which means the barrier to adoption for a typical small business has dropped dramatically compared to just a few years ago. This guide walks through how passkeys work, why businesses are adopting them, and what a realistic transition away from passwords actually looks like.
Why Passwords Have Failed as a Security Model
Passwords were never designed for the world businesses operate in today. A password created in 2010 assumed a person would remember one or two of them for a handful of systems. Today’s employees juggle dozens of logins across cloud platforms, internal tools, vendor portals, and personal accounts, which naturally leads to shortcuts like reusing the same password everywhere or storing it somewhere insecure.
Attackers have built entire business models around this weakness. Credential stuffing tools automatically test stolen username and password combinations against thousands of websites in minutes, and phishing kits are sold as ready-made templates that require almost no technical skill to deploy. Even strong, unique passwords remain vulnerable to phishing pages designed to capture them the moment someone types them in.
A few numbers explain why this problem has not gone away on its own:
- The vast majority of confirmed data breaches still involve some form of stolen or weak credentials
- Password reset requests remain one of the most common and costly help desk tickets for growing businesses
- Multi-factor authentication helps but does not fully stop real-time phishing attacks that intercept one-time codes
Reviewing emerging cyber threats makes it clear that credential theft remains one of the most consistent entry points attackers rely on, which is exactly the weakness passkeys are designed to remove entirely.
The financial impact of this problem is not limited to the moment a breach occurs. Businesses often underestimate the ripple effects of a single compromised account, including the hours spent investigating how far an intruder moved through connected systems, the cost of notifying affected clients or partners, and the reputational damage that can linger long after the technical issue is resolved. Password-based security failures rarely stay contained to a single system once an attacker gains a foothold, which is part of why the shift toward passwordless methods has picked up so much momentum across businesses of every size.
What Are Passkeys and How Do They Work
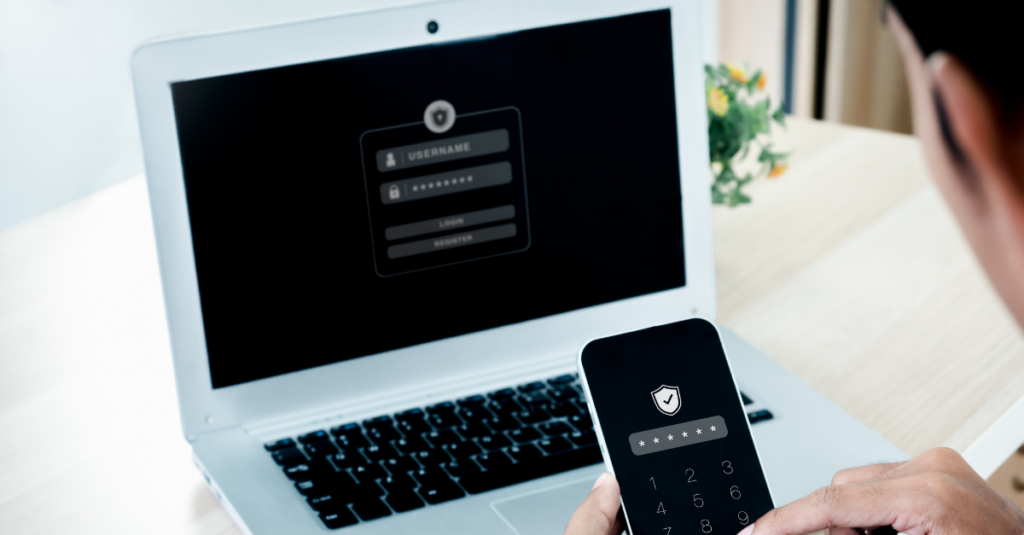
A passkey is a pair of cryptographic keys generated when a user sets up an account on a device. One key stays private and never leaves the device, stored securely in hardware like a phone’s secure enclave or a computer’s trusted platform module. The other key is public and gets shared with the website or application during setup. When a person logs in later, the device proves ownership of the private key without ever transmitting a password or secret over the internet.
This is a meaningful shift from how authentication has traditionally worked. Instead of typing something a server checks against a stored value, the device performs a cryptographic handshake that confirms identity without exposing anything an attacker could steal and reuse elsewhere. Unlocking the passkey itself typically relies on a fingerprint, face scan, or device PIN, meaning the authentication factor never leaves the physical device in the first place.
Because there is no shared secret transmitted during login, phishing a passkey is significantly harder than phishing a password. Even if someone tricks an employee into visiting a fake login page, there is no password to capture, and the cryptographic exchange simply will not complete against an illegitimate site. This directly addresses the kind of AI powered protection gap that traditional password-based phishing defenses have struggled to close as attacks have grown more convincing.
The Business Case for Going Passwordless
Security is the headline reason businesses are exploring passkeys, but the operational benefits matter just as much for many organizations. Password-related help desk tickets, ranging from resets to lockouts, consume a disproportionate amount of IT support time for a problem that passkeys largely eliminate. Employees also benefit directly, since logging in with a fingerprint or face scan is faster and less frustrating than remembering and typing a complex password correctly on the first try.
The efficiency gains extend beyond individual login moments. Fewer credential-related security incidents mean fewer hours spent on investigation, containment, and recovery, freeing internal teams and outside providers to focus on more strategic work. Businesses evaluating IT service upgrades for the year ahead are increasingly including passwordless authentication on that list, recognizing it as a practical improvement rather than a purely theoretical one.
Some of the most commonly cited business benefits include:
- Fewer help desk tickets tied to forgotten or expired passwords
- Faster login times that reduce daily friction for employees
- Significantly reduced exposure to phishing-based credential theft
- Lower risk of the account takeover incidents that often precede larger breaches
- Better audit trails, since passkey logins are tied directly to a specific registered device
How Passkeys Fit Into a Zero Trust Framework
Passkeys work particularly well alongside a broader zero trust framework, which assumes no login attempt should be automatically trusted regardless of where it originates. Rather than relying on a single password as the sole gate protecting an account, zero trust environments continuously evaluate context such as device health, location, and behavior alongside the authentication method itself.
Because passkeys are device-bound, they naturally strengthen this model. An attacker cannot simply steal a password from a data breach and use it from an unfamiliar device, since the private key required to complete authentication never leaves the legitimate device it was created on. This makes conditional access policies more effective, since the authentication method itself is already resistant to the kind of remote credential theft that undermines password-based systems.
Layering passkeys into a broader identity strategy also supports the kind of network security oversight businesses need as they add more cloud applications and remote access points to their environment. Rather than treating authentication as a single checkbox, passkeys become one part of a continuously verified access model.
Passwordless Authentication and Compliance
Regulatory frameworks across industries increasingly expect businesses to demonstrate strong authentication controls, and passwordless methods are gaining explicit recognition in updated guidance from standards bodies. Moving away from static passwords also simplifies certain audit requirements, since passkeys eliminate common findings like weak password policies, credential reuse across systems, and unclear password rotation practices that auditors frequently flag.
Businesses working through regulatory compliance assistance programs often find that adopting passkeys strengthens their overall audit posture, since strong, phishing-resistant authentication is increasingly viewed as a baseline expectation rather than an advanced security measure. This is particularly relevant for businesses in regulated industries handling sensitive client data, financial records, or protected health information, where authentication strength is scrutinized closely during audits and assessments.
Cybersecurity insurance carriers are also paying closer attention to authentication practices when underwriting policies. Reviewing the cybersecurity package features that carriers now expect as standard shows that phishing-resistant authentication methods like passkeys are becoming a factor in coverage terms and premium pricing, not just a nice-to-have security upgrade.
Common Concerns Businesses Have About Passkeys
Despite the clear benefits, many businesses hesitate before adopting passkeys, often due to misunderstandings about how the technology actually works in practice. Addressing these concerns directly tends to speed up adoption significantly.
- What happens if an employee loses their device? Most passkey systems support account recovery through backup devices, secondary passkeys registered on other hardware, or administrator-assisted recovery processes, similar to how lost phone recovery already works for many cloud accounts.
- Do passkeys work across different device types? Modern passkey implementations sync across a user’s registered devices through the operating system’s built-in credential manager, and cross-platform standards allow passkeys created on one device type to be used for login approval from another when configured correctly.
- Is switching over to passkeys a massive IT project? For businesses already using modern cloud platforms like Microsoft 365 or Google Workspace, passkey support is often already built in and simply needs to be enabled and rolled out with proper employee guidance rather than built from scratch.
- What about older systems that do not support passkeys? Legacy applications that cannot yet support passkeys can typically continue using strong password policies paired with multi-factor authentication until they are updated or replaced, allowing a gradual transition rather than an all-or-nothing switch.
A Realistic Implementation Roadmap for Adopting Passkeys
Businesses do not need to switch every system to passkeys overnight, and attempting to do so often creates more confusion than security benefit. A phased rollout tends to produce better adoption rates and fewer support headaches.
- Start with an inventory of which business applications already support passkey authentication natively
- Pilot the rollout with a small group of employees before expanding company-wide
- Pair passkey adoption with a broader full IT evaluation to identify which systems are ready and which need updates first
- Provide clear, simple setup instructions rather than assuming employees will figure it out unassisted
- Maintain a fallback authentication method for systems that have not yet been transitioned
- Monitor adoption rates and address friction points quickly before employees revert to old habits
Businesses looking to modernize more broadly often pair this rollout with other digital transformation trends already underway across their organization, treating authentication as one piece of a larger technology refresh rather than an isolated project.
Cloud and Productivity Platforms Driving Passkey Adoption
Major cloud providers have made passkey support a priority feature rather than an afterthought, which is a big part of why adoption is accelerating so quickly across businesses of every size. Platforms supporting cloud infrastructure services now widely include native passkey options, meaning businesses already using mainstream productivity suites often have the underlying capability available without needing a separate purchase or complex integration project.
This built-in support extends to everyday workplace productivity tools that employees use throughout the day, making the transition far less disruptive than earlier generations of authentication upgrades that required entirely separate hardware tokens or specialized software. Guides covering Microsoft 365 adoption increasingly include passkey setup as a standard step, reflecting how mainstream the technology has already become within everyday business software.
Data Protection Still Matters Beyond the Login Screen
Passkeys dramatically reduce the risk of credential theft, but they are one layer within a broader security strategy rather than a complete replacement for it. Businesses still need secure data backup protecting critical files from ransomware, hardware failure, or accidental deletion, since strong authentication alone does not protect data that is already compromised through other means such as malware or insider mistakes.
Continuous monitoring also remains essential even after passkeys are in place. Understanding network support value as part of a layered defense helps businesses catch issues that authentication improvements alone cannot address, such as unusual internal network traffic or vulnerable third-party software connected to the environment. Passwordless login closes one major door for attackers, but a complete security strategy still requires watching the rest of the house.
Employee Training for a Smooth Passwordless Transition
Technology alone rarely drives successful adoption. Employees need clear, simple explanations of why the change is happening and how it actually benefits them personally, not just the organization’s security posture. Framing the transition around convenience, faster logins and no more forgotten passwords, tends to generate far more enthusiasm than framing it purely as a mandatory security requirement.
Training should walk through the setup process step by step, address backup and recovery procedures clearly, and give employees a simple point of contact if something goes wrong during the transition. Businesses that have already gone through similar technology shifts often reference lessons learned from broader proactive support benefits programs, where clear communication and readily available support made the difference between smooth adoption and widespread frustration.
AI and the Future of Identity Verification
Artificial intelligence is beginning to influence authentication in ways that go beyond passkeys alone. Behavioral biometrics, which analyze typing patterns, mouse movement, and even how someone holds their phone, are being layered on top of passkey authentication to add continuous verification throughout a session rather than just at the initial login moment. This means a system can flag unusual activity even after a legitimate login has already occurred, catching scenarios like a stolen unlocked device being used by someone other than its owner.
At the same time, businesses need clear internal guidance around how AI tools interact with identity and access systems generally. Establishing sound AI governance priorities ensures that as AI becomes more embedded in daily operations, including identity verification, it is deployed with appropriate oversight rather than introducing new risks the organization has not fully evaluated. Understanding the true managed services ROI of pairing modern authentication with managed monitoring also helps business owners see the full financial picture rather than viewing security spending purely as a cost center.
Why Plano and Garland Businesses Are Making the Switch Now
Local businesses across Plano and Garland are increasingly recognizing that passwordless authentication is not a distant, futuristic concept but a practical upgrade available today. Industries handling sensitive client information, including those relying on modern threat detection approaches to replace outdated antivirus-only strategies, are among the earliest adopters, since the combination of stronger authentication and active monitoring closes gaps that either approach alone would leave open.
CMIT Solutions of Plano & Garland helps local businesses evaluate which systems are ready for passkeys today, which need updates first, and how to roll out the change without disrupting daily operations. This kind of hands-on guidance from a locally based team, familiar with the CMIT Solutions of Plano & Garland service area, tends to produce far fewer rollout surprises than a purely self-managed transition. This includes reviewing flexible service plans that scale alongside a business as more systems transition away from passwords, along with ongoing ongoing technology guidance to keep the rollout on track as new tools and standards continue to emerge. Businesses evaluating their options often start by reviewing what makes for an experienced technology provider before committing to a long-term authentication strategy.
Passkeys as Part of a Broader Technology Strategy
Authentication upgrades rarely happen in isolation, and the businesses that get the most value from moving to passkeys usually treat the change as one piece of a wider technology strategy rather than a standalone project. A Plano Garland IT provider familiar with the local business landscape can help map out where passwordless login fits alongside everything else already running in the environment, from daily productivity tools to longer-term infrastructure planning.
This wider view matters because authentication touches nearly every other system a business relies on. Reliable on demand IT support makes the rollout smoother for employees who run into setup questions, while dedicated cybersecurity protection services ensure the rest of the security stack is keeping pace with the authentication upgrade rather than lagging behind it. Businesses exploring artificial intelligence solutions for other parts of their operations often find that a completed AI readiness evaluation naturally surfaces authentication gaps as well, since identity and access controls tend to be one of the first things reviewed before expanding AI tools across a team.
Coordinating this kind of change also touches procurement and communication systems that many businesses overlook. Thoughtful smart technology procurement practices prevent businesses from purchasing overlapping tools that duplicate authentication features already available elsewhere, while secure business communication platforms give teams a verified channel to coordinate the rollout and troubleshoot issues without relying on easily spoofed email threads. Businesses curious about the people behind this kind of coordinated approach can review our team experience supporting local organizations through similar technology transitions.
Bringing It All Together
Passwords have quietly been one of the weakest links in business security for years, and passkeys represent a genuine, practical way to close that gap rather than another temporary patch. The technology is mature, widely supported across major platforms, and increasingly expected by regulators, insurers, and clients alike. Businesses that start the transition now, even gradually, position themselves ahead of a shift that is quickly becoming the new standard rather than an optional upgrade.
Making the move away from passwords does not have to mean tackling every system at once, and it does not have to happen without guidance. Plano and Garland businesses ready to explore whether passkeys are the right fit for their organization, and how to roll them out without disrupting daily work, can start with a conversation about where current authentication practices stand today. Schedule a consultation to build a passwordless roadmap suited to your specific systems and team
Frequently Asked Questions