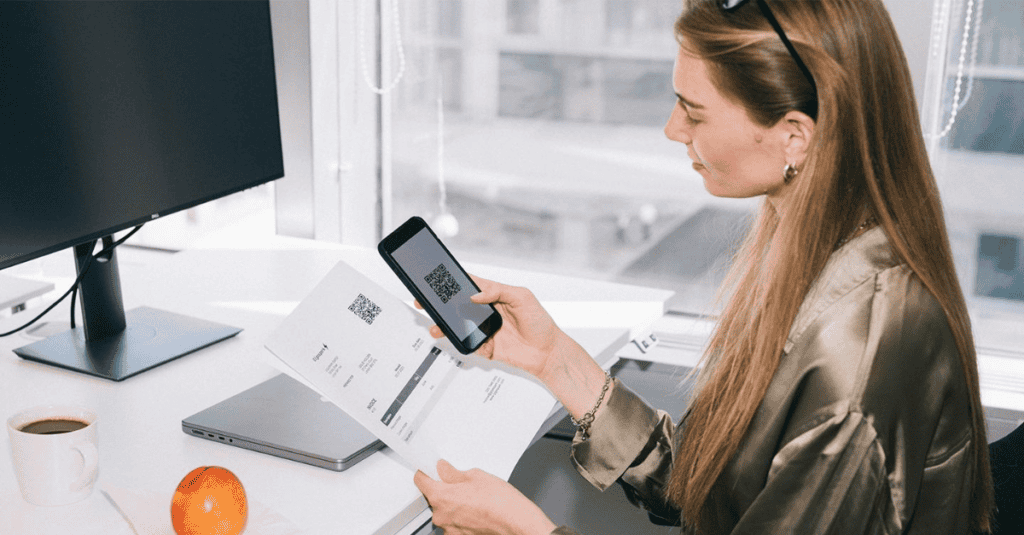
A QR code on an invoice looks harmless. It sits quietly in the corner, offering a convenient way to pay a bill or verify a document, and most people scan it without a second thought. That casual trust is exactly what makes QR codes an increasingly popular tool for scammers targeting businesses. Unlike a suspicious link flagged by emerging cyber threats monitoring in an email, a QR code cannot be hovered over to preview where it leads. The destination stays hidden until a phone’s camera has already opened it, and by then the scam has already done its job.
Documented in emerging cyber threats research, this technique, often called quishing, has grown quickly because it slips past many of the defenses businesses already have in place. Email security filters, part of typical cybersecurity package essentials, are built to scan text-based links, not images embedded in a PDF invoice. Employees trained through cybersecurity package essentials to spot a suspicious email link may have never been told to apply the same caution to a scannable code. Understanding how this scam actually works is the first step toward closing a gap that most businesses have not yet accounted for in their security awareness training.
How QR Code Phishing Actually Works
The mechanics of a QR code scam are simple, which is part of why the technique has spread so quickly across email-based fraud campaigns.
- An attacker, exploiting gaps in zero trust framework coverage, generates a QR code that links to a fake login page or payment portal
- The code gets embedded into a convincing document, most commonly a fake invoice or vendor notice
- The document is sent through email, sometimes spoofing a known vendor or internal department
- An employee scans the code using their personal phone, often bypassing company network protections entirely
- The linked page, a tactic covered under identity based attacks, prompts for login credentials, payment details, or both
- Captured credentials or payment information are used immediately or sold to other criminal groups
The use of a personal phone to scan the code is a critical detail. Many businesses have email filtering, network management services, and monitoring in place on company devices, but a personal phone scanning a QR code operates entirely outside that protected environment. The scam is specifically designed to route around the defenses a business has already invested in.
Why Invoices Are the Perfect Delivery Method
As covered in financial services cybersecurity reviews, fake invoices have long been a favored tool for business email compromise, but QR codes have made the scam more effective by adding a layer of legitimacy and urgency that plain text links lack.
- Invoices create a natural sense of obligation, since ignoring a bill feels like a real consequence
- A QR code feels more official than a plain hyperlink, mimicking legitimate vendor payment systems
- Finance and accounts payable staff process invoices in high volume, increasing the chance of a rushed decision
- Attackers can spoof real vendor names, a risk outlined in managed detection response guidance, and formatting, making the fake document visually convincing
- QR codes bypass text-based email filtering, a gap tied to AI driven protection coverage, that would otherwise flag a suspicious embedded link
An accounts payable employee processing dozens of invoices a day is far more likely to scan a code that looks routine than to carefully inspect where every embedded image actually leads. That volume and routine nature is precisely what attackers count on.
Why Traditional Email Security Misses This Threat
Most email security tools, addressed further under compliance management support, were built during a period when phishing links were plain text URLs embedded directly in message content. QR code phishing exploits a gap in how that technology evolved.
- Text-based URL scanning tools cannot read a destination encoded inside an image
- QR codes embedded in a PDF attachment add another layer of separation from email body scanning
- Sandboxing and link-rewriting protections, part of managed IT support offerings, often do not extend to embedded QR images
- Personal devices used to scan the code, an issue covered under IT support packages, typically fall outside corporate mobile device management policies
- Employees frequently perceive scanning a code as a lower-risk action than clicking a link, even though the underlying risk is identical
This combination of technical blind spots, discussed in cloud services solutions reviews, and a mismatch in employee risk perception is exactly why QR code phishing has grown as quickly as it has. The attack does not need to be technically sophisticated. It simply needs to exploit gaps that most existing security programs were never designed to cover.
What a Real QR Code Phishing Attempt Looks Like
A realistic scenario helps illustrate how this plays out in practice. An accounts payable coordinator, working with Microsoft 365 adoption tools, receives an email that appears to come from a long-standing vendor, referencing a specific project the company is genuinely working on. The email includes a PDF invoice with a QR code positioned where a payment portal link would normally appear, accompanied by a note about a recently updated payment system. The coordinator scans the code with their phone, lands on a page that closely resembles the vendor’s actual branding, and enters company banking credentials to “verify” the account before completing payment. Those credentials are now in the attacker’s hands, and the fraudulent invoice itself may still get paid through the normal process, since the QR code interaction and the actual invoice payment were treated as separate steps.
Warning Signs Employees Should Watch For
Recognizing the specific signals tied to QR code scams, similar to guidance in why law firms are moving beyond legacy tools, gives employees a practical way to apply caution without needing to treat every single code with suspicion.
- Unexpected invoices referencing a payment system change or urgent account verification
- Pressure language suggesting immediate action is required to avoid a penalty or service disruption
- A QR code replacing what would normally be a clickable link or a phone number to call directly
- Vendor communications arriving from a slightly altered domain, a concern raised in top compliance challenges coverage, that looks close to the real one
- Requests to enter banking credentials or payment details after scanning, rather than simply viewing information
- QR codes appearing in unusual places, such as embedded directly in an email body rather than an attachment
None of these signals alone confirms a scam with certainty, but a combination of two or more is a strong reason to verify the request through a separate, previously known contact method before taking any action.
Building Organizational Defenses Against QR Code Phishing
Closing this gap requires a combination of technical controls, employee awareness, and process changes around how invoices and payment requests get handled.
Technical Controls
- Deploy email security tools, guided by technology procurement planning, specifically capable of scanning and analyzing embedded QR codes
- Extend mobile device management policies, similar to unified communications systems coverage, to cover QR code scanning behavior where feasible
- Require multi-factor authentication, a step outlined in passkey authentication trends, on all financial and vendor portal accounts to limit damage from stolen credentials
- Monitor for newly registered domains, part of proactive IT support practices, that closely resemble known vendor names
Employee Awareness
- Update security awareness training, backed by ransomware survival playbook lessons, specifically to include QR code risks, not just traditional phishing links
- Train accounts payable and finance staff specifically, given their elevated exposure highlighted in managed IT costs research, to invoice-based scams
- Encourage employees to use a company device or a QR scanning tool that previews the destination URL before opening it
- Reinforce that scanning a code carries the same risk as clicking a link, despite feeling more casual
Process Changes
- Require verification of any payment system change, part of IT consulting guidance, through a separate, previously established contact method
- Implement a policy that vendor banking detail changes always trigger a phone call to a known contact before processing
- Separate the person who approves an invoice, an approach covered in business continuity planning, from the person who executes the payment, reducing single-point-of-failure risk
- Maintain an updated list of verified vendor contacts, supported by data backup solutions, independent of whatever contact information appears on an incoming invoice
Why This Threat Is Likely to Grow
Discussed further in cloud automation future coverage, QR codes have become genuinely useful for legitimate business purposes, from contactless menus to event check-ins to real payment systems, and that legitimate adoption is exactly what gives the scam its cover. As QR codes become a more normal part of everyday business interactions, employee skepticism toward them naturally decreases, which works directly in an attacker’s favor. Attackers also benefit from the relative novelty of this technique, similar to trends in agentic AI security coverage, compared to traditional phishing, since security awareness training at many organizations has not yet caught up to include it as a standard topic.
CMIT Solutions works with businesses across Plano and Garland, supported by trusted IT services, to update security awareness programs and email defenses specifically to account for QR code based threats, closing a gap that many existing security programs were never designed to cover in the first place.
How QR Code Phishing Compares to Traditional Business Email Compromise
Business email compromise has been a persistent threat for years, and QR code phishing is best understood as an evolution of that same underlying goal rather than a completely separate category of attack. The end objective, whether stealing credentials, redirecting a payment, or gaining a foothold for a larger fraud scheme, remains largely unchanged. What has shifted is the delivery mechanism and the way it evades detection.
- Traditional business email compromise often relies on urgency and authority, impersonating an executive or known contact directly in the message text
- QR code phishing adds a technical evasion layer on top of that same social engineering foundation, since the malicious destination is hidden inside an image
- Both techniques exploit routine business processes, particularly around payments, invoices, and account changes
- Both rely on the target acting quickly without verifying through an independent channel
- QR code phishing specifically benefits from the assumption that images are inherently safer than clickable text
Security teams that have already built strong defenses against classic business email compromise sometimes assume those defenses automatically extend to QR code variants. In practice, the technical scanning tools and the employee training built around plain text links often need direct updates to specifically address image-based threats, since the underlying detection mechanisms are not always transferable.
The Role of Vendor Impersonation in Making These Scams Convincing
A generic phishing attempt is relatively easy to dismiss. A QR code scam that convincingly impersonates a real, known vendor is far more dangerous, since it exploits an existing trusted relationship rather than trying to build trust from nothing.
- Attackers often research a target company’s actual vendor relationships before crafting a fake invoice
- Publicly available information, including a company’s own website or social media, can reveal vendor names and project details
- A previous data breach involving either party can supply enough detail to make the impersonation highly specific
- Attackers sometimes monitor compromised email accounts for a period before sending a fake invoice, timing it to align with a real, expected payment
- The more specific and accurate the details in a fake invoice, the less likely an employee is to question it
This level of preparation means that generic advice like “watch for spelling errors” or “check for a suspicious sender name” is no longer sufficient on its own. A well-researched attack can pass both of those basic checks while still being entirely fraudulent, which is exactly why independent verification through a separate, previously established contact method remains the most reliable defense regardless of how convincing a request appears.
What to Do If Your Business Falls Victim to This Scam
Even with strong defenses in place, no organization is completely immune to a well-executed scam. Having a clear response plan ready reduces how much damage occurs and how quickly the business can recover.
- Immediately change passwords on any account accessed through the fraudulent page
- Contact the bank if any payment was redirected, since some fraudulent transfers can still be reversed if caught quickly
- Notify the actual vendor being impersonated, since they may be unaware their name is being used in an active scam
- Review recent email activity for signs of a broader account compromise beyond the single incident
- Document the incident thoroughly for insurance purposes and any required regulatory notifications
- Communicate internally so other employees are aware and can watch for similar attempts
Speed matters significantly in the immediate aftermath. A fraudulent wire transfer caught and reported within hours has a meaningfully better chance of recovery than one discovered days or weeks later, once funds have moved through multiple accounts and become far harder to trace.
Building a Culture Where Questioning Requests Feels Normal
Beyond technical controls and formal policy, the organizations that handle this threat best tend to share a cultural trait: employees feel comfortable pausing and asking questions about an unusual request, rather than feeling pressured to act quickly to avoid seeming difficult or slow.
- Leadership should openly acknowledge that verifying an unusual request is expected, not an inconvenience
- No employee should face criticism for delaying a payment to confirm its legitimacy first
- Sharing real examples of attempted scams, even unsuccessful ones, helps normalize vigilance across the team
- Finance and accounts payable staff in particular benefit from knowing leadership backs their caution, even under deadline pressure
This cultural piece is often overlooked in favor of purely technical solutions, but it consistently makes a measurable difference. A well-trained employee who feels empowered to pause and verify a request is one of the most effective defenses a business can have, regardless of how technically sophisticated the scam attempting to bypass them happens to be.
Final Thoughts
QR code phishing succeeds precisely because it looks so unremarkable. A code on an invoice does not trigger the same instinctive caution a suspicious link does, even though the underlying risk is identical or worse, given how many existing security tools cannot inspect it. Closing this gap requires updating both the technology stack and the awareness training that employees rely on daily, since neither alone fully addresses the problem. CMIT Solutions helps businesses across Plano and Garland stay ahead of exactly this kind of evolving threat, before it turns into a costly incident.
If your business has not yet updated its security awareness training to cover QR code based scams, schedule a consultation and close that gap before an attacker finds it first.
Frequently Asked Questions