The phishing emails people picture are the badly written ones with an odd greeting and a foreign prince. Those still go out, and almost nobody falls for them.
The ones that work look ordinary. They arrive at a moment when the request makes sense, they ask for something small, and they land in front of a competent person who is moving fast. Here are five that we see land on capable teams.
The reply inside a thread you started
An attacker gets into one mailbox, reads the conversations already running, and replies inside one of them. The subject line is familiar, the history is real, and the new message asks you to look at an attached document. Nothing about the shape of it feels wrong because most of it is not wrong.
The invoice from a vendor you really use
This one arrives during a busy week from a supplier whose name your bookkeeper recognizes. The amount is plausible. The only thing that changed is the bank account on the remittance page.
Forhospitality and retail businesses heading into the fall season, this is the one worth raising at a staff meeting now, becausevendor traffic goes up and invoices get approved faster than usual.
The Microsoft 365 sign-in page
A message says a shared file is waiting, or that a password is about to expire, and the link opens a login page that looks correct because it was copied pixel for pixel. Someone types theircredentials, the page forwards them to a real document, and nothing appears to have gone wrong.
The short text message from the owner
It arrives on a phone, not in email. It is brief and friendly, it says the sender is stuck in a meeting, and it asks for a quick favor, often gift cards or a same-day payment. It works because it compresses two things: the appearance of authority and the pressure of time. In a business where the owner really does text the team, it works even better.
The shared document notification
Afile-sharing notice from a name your team knows, sometimes from a real account that has been taken over at another local company. The notification format is one your staff sees ten times a week, which is exactly why it gets clicked.
The pattern underneath all five
None of these ask the reader to do something strange. They ask for one small, reasonable action at a moment when that action fits. That is a design problem, not an intelligence problem, and it is why blaming the person who clicked is both unfair and unhelpful.
Two habits handle the whole category. First, any request that moves money or changes access gets verified on a different channel before anyone acts, using a phone number your business already has on file. Second, reporting a suspicious message has to be easy and consequence-free, because the useful report is the one that comes in ten minutes after a click, not the one that never comes at all.
review what is reaching your inbox and where your current setup has gaps.
CMIT Solutions of San Marcos and New Braunfels supports businesses across San Marcos, New Braunfels, Kyle, Buda McQueeney, and Seguin. If you want an honest read on what is reaching your team and what your current setup would catch, a free 30-minute assessment covers it.
Schedule a free 30-minute IT assessment at cmitsolutions.com/sanmarcos-tx-1047/contact-us/ or call (830) 515-4151.
Frequently Asked Questions
1. What is phishing? +
Phishing is a scam in which an attacker pretends to be a trusted person or company to trick someone into sharing passwords, sending money, or opening a harmful file. It commonly arrives by email but can also appear through text messages, phone calls, or shared document links.
2. Why do smart, experienced people still fall for phishing emails? +
Modern phishing messages are designed to look routine rather than obviously suspicious. They often arrive when a request seems reasonable, ask for one small action, and target busy employees who are working quickly. A successful phishing message says more about the quality of the deception than the intelligence of the person receiving it.
3. Are phishing attacks only a problem for large companies? +
No. Small and mid-sized businesses are common targets because they handle real money, vendor payments, customer information, and valuable account credentials while often having fewer dedicated security resources than larger organizations.
4. What is the difference between phishing and spear phishing? +
Traditional phishing is often sent to many people at once. Spear phishing targets a specific employee or business and may use real names, vendors, projects, job titles, or recent events to make the message more believable.
5. What are the warning signs of a phishing email? +
Warning signs can include unexpected urgency, requests to move money or change account information, unfamiliar links or attachments, and sender addresses that are slightly different from the real address. Because sophisticated phishing may contain none of these obvious signs, requests involving money or access should always be verified separately.
6. How can I tell if a reply inside an existing email thread is fake? +
It can be difficult because the previous conversation may be genuine. Treat any unexpected attachment, payment request, account change, or unusual instruction inside an existing thread with caution and confirm it with the sender by phone or another trusted method.
7. How should we handle a vendor invoice with new bank details? +
Do not verify the change using contact information contained in the email or invoice itself. Call the vendor using a phone number already stored in your own records and confirm the new banking information before making a payment.
8. Can phishing happen over text messages? +
Yes. Text-message phishing, commonly called smishing, may imitate an owner, manager, bank, delivery company, or other trusted source. These attacks often rely on urgency and can bypass the protections businesses have in place for email.
9. How do fake Microsoft 365 sign-in pages work? +
Attackers create a page that closely resembles the real Microsoft 365 sign-in screen and send a link claiming that a document is waiting or an account needs attention. Credentials entered into the fake page are captured by the attacker, and the victim may then be redirected elsewhere so the theft is not immediately obvious.
10. Should I click a link that says my password is about to expire? +
Avoid using the link in the message. Instead, open a new browser window and navigate directly to the official account or sign-in page. If you are unsure whether the warning is legitimate, contact your IT team.
11. Does multi-factor authentication stop phishing? +
Multi-factor authentication can significantly reduce the damage caused by stolen passwords, but it does not eliminate phishing. Strong protection combines MFA with email filtering, secure authentication settings, suspicious sign-in alerts, and employee awareness.
12. Why are shared document notifications so effective as phishing scams? +
Employees receive legitimate document-sharing notifications regularly, so another one may not seem unusual. Attackers can also send malicious sharing messages from compromised accounts, making them appear even more trustworthy.
13. What should I do if I clicked a suspicious link? +
Report it immediately, even if nothing appears to have happened. If you downloaded or opened a suspicious file, follow your organization’s incident procedures and contact your IT team quickly so they can investigate and contain any potential damage.
14. What if I entered my password on a fake page? +
Tell your IT team immediately and change the password using a trusted device. Your IT team can also review recent sign-in activity, revoke active sessions, check multi-factor authentication settings, and look for suspicious mailbox rules or other account changes.
15. Who should employees report suspicious messages to? +
Choose one clear reporting path, such as an IT provider, security team, or internal manager, and make sure every employee knows how to use it. Reporting should be fast and simple, such as through a dedicated email address or one-click reporting button.
16. Should employees be disciplined for clicking a phishing link? +
Usually, the priority should be fast reporting and learning rather than punishment. Employees who fear consequences may delay reporting an incident, while immediate reporting gives the IT team a better chance to contain the problem quickly.
17. How can a business reduce its phishing risk? +
Use multiple layers of protection. Verify requests involving money or account access through a separate channel, make suspicious messages easy to report, use strong email filtering, enable multi-factor authentication, monitor unusual sign-ins, and provide regular employee training.
18. How often should staff receive security awareness training? +
Short, regular training sessions are generally more effective than relying only on one annual presentation. Quarterly refreshers, combined with timely updates about new scam techniques or seasonal threats, can help keep security awareness current.
19. What is a verification callback policy? +
A verification callback policy requires employees to confirm requests involving money, banking details, or sensitive access by calling a trusted phone number already held in company records. Contact information contained in the suspicious message should not be used for verification.
20. How can a managed IT provider help with phishing? +
A managed IT provider can configure and monitor email security, enforce multi-factor authentication, review suspicious sign-in activity, provide security awareness training, and respond quickly when an employee reports a phishing attempt. The goal is to combine technology, clear processes, and employee awareness so one convincing message is less likely to become a larger security incident.
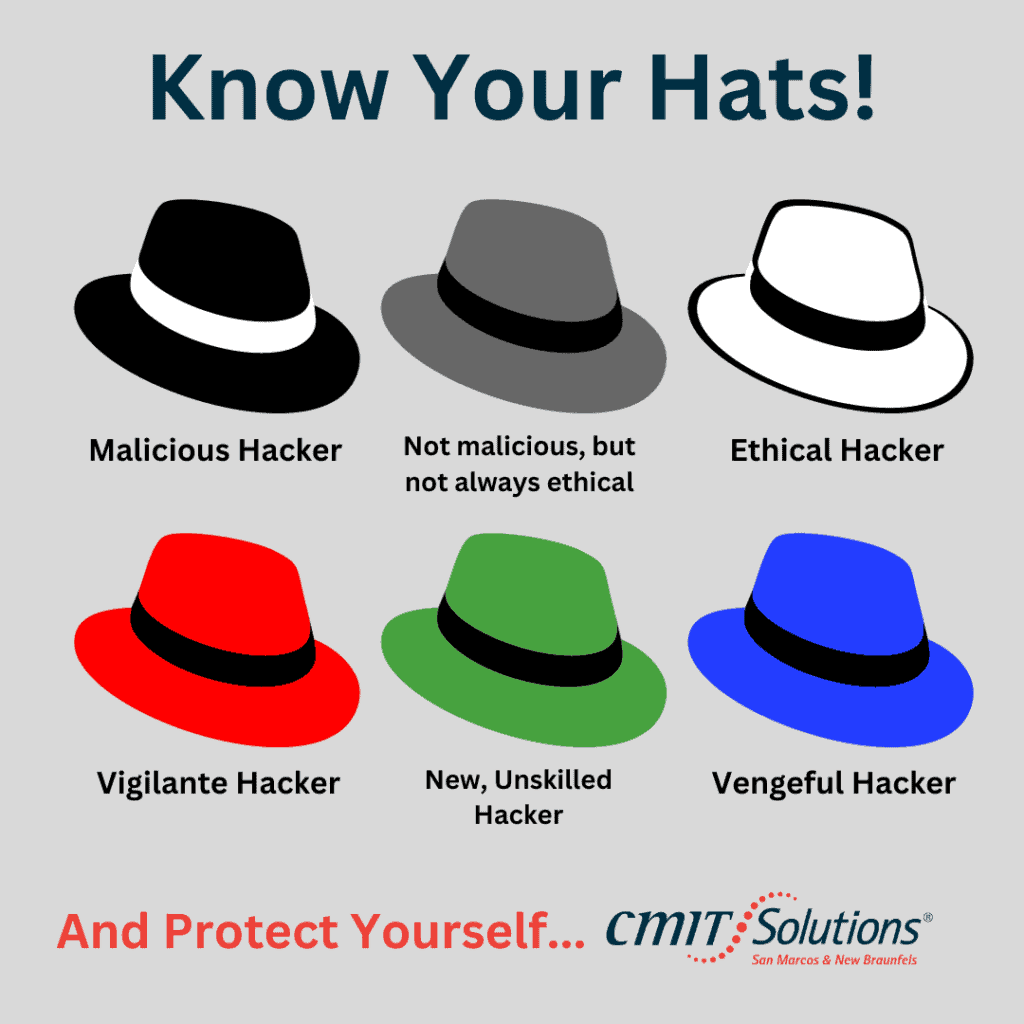
Do you ever wonder who is behind all those cyberattacks that steal private information or cause mayhem online? Well, there are many different types of hackers out there, from black hats to red hats and everything in between.