Cybersecurity Awareness Month: The Four Things That Actually Protect a Small Business
Every October, small business owners get a lot of cybersecurity advice at once. Chambers send reminders, vendors send checklists, and the volume of it can make a well-run business feel like it is behind on forty things.
It usually is not behind on forty things. For a company running 15 to 60 people in San Marcos, New Braunfels, Seguin, or Kyle, a small number of controls do most of the protective work. If you only have the attention for one conversation this month, have it about these four.
1.Multi-factor authentication on email and remote access
A password alone is one piece of information, and information getsreused, guessed, and typed into the wrong login page. Multi-factor authentication adds a second proof that the person signing in is actually your employee, usually an approval prompt on their phone.
Start with email and any remote access into your network. Those are the two doors that open the most other doors. Payroll and banking tools come next.
2. Updates that happen without anyone remembering to do them
Software vendors publish fixes constantly. The gap between a fix being available and a fix being installed on the laptop at your front desk is where a lot of avoidable trouble lives.
The practical question is not whether your team believes in updates. It is whether patching is somebody’s assigned job with a record of what got applied and what did not. On amanaged setup, that happens on a schedule and produces a report you can actually look at.
3. Backups that somebody has restored from
Most businesses have a backup. Fewer havewatched someone restore a file from it recently. Those are different levels of confidence, and the difference only becomes visible on the day it matters.
A useful standard: you know where yourbackups live, you know how far back they go, you know how long a restore takes, and somebody has tested that in the last quarter.
4. A rule about who can move money or change access
This one is a process control rather than a technology control, and it prevents the losses that technology cannot catch. If a request arrives by email to change a vendor’s bank details, release a payment, or add a new user with admin rights, somebody verifies it on a second channel before acting. A phone call to a number already on file is enough.
Write it down, tell the team it applies to requests that look like they came from you, and make it clear that pausing to verify is never going to get anyone in trouble.
What to do with this in October
You do not need to install all four this month. The useful exercise is narrower: sit down for twenty minutes and mark each one as in place, partly in place, or not yet. Plenty of growing businesses find they are solid on two, halfway on one, and have not looked at the fourth in a while.
That list is worth more than another article. It tells you what to budget for in the next quarter, and it gives you something concrete to hand to whoever asks about yoursecurity posture, whether that is an insurer, a client, or your board.
Want this as a conversation instead of an article?
We are happy to walk a local chamber, Rotary club, or business group through these four over lunch, at no cost. It runs about thirty minutes with time for questions, and it is a plain-English session rather than a sales presentation.
CMIT Solutions of San Marcos and New Braunfels works with businesses across San Marcos, New Braunfels, Kyle, Buda, McQueeney, and Seguin.A free 30-minute assessment covers these four plus your backups, yourMicrosoft 365 setup, and yournetwork, and you get a written summary with priorities and plain pricing.
1. What is Cybersecurity Awareness Month, and why should a small business care?+
Cybersecurity Awareness Month happens every October and brings a wave of reminders, checklists, and advice from chambers and vendors. It is a useful prompt to review your basics once a year, even if you only act on a few things.
2. Which security controls matter most for a small business?+
Four do most of the protective work: multi-factor authentication on email and remote access, updates that happen automatically, backups that have been tested with a real restore, and a rule for verifying requests to move money or change access. Most small businesses are stronger on some of these than others, and finding the gaps is the first step.
3. What is multi-factor authentication (MFA)?+
MFA adds a second proof of identity on top of a password, usually an approval prompt on an employee’s phone. Even if a password is guessed, reused, or typed into a fake login page, the second step can stop the sign-in.
4. Where should we turn on MFA first?+
Start with email and any remote access into your network, since those two open the most other doors. Payroll and banking tools come next.
5. Will MFA frustrate my employees?+
It adds a few seconds to a sign-in, and most prompts take a single tap. Explaining why you are doing it, and that it protects them as much as the business, goes a long way toward acceptance.
6. Why do software updates matter so much?+
Vendors publish fixes constantly, and the time between a fix being released and installed on every device is where avoidable problems tend to occur. Closing that gap reduces risk without requiring anyone to be a security expert.
7. How do we make sure updates actually get done?+
Make patching someone’s assigned job, and keep a record of what was applied and what was not. A managed setup runs updates on a schedule and produces a report you can review.
8. How do I know my backups will work when I need them?+
Check four things: you know where backups live, how far back they go, how long a restore takes, and that someone has restored from them recently. Having a backup and having proven a restore are very different levels of confidence.
9. How often should we test our backups?+
Once a quarter is a sensible minimum. Test more often if your data changes quickly or your business cannot afford much downtime.
10. What is the difference between having a backup and being able to recover?+
A backup is a stored copy of your data. Recovery is being able to get that data, and the systems that use it, working again in a time your business can live with. Testing a restore is how you find out which one you actually have.
11. What is a payment and access verification rule?+
It is a written process requiring a second-channel check before certain requests are acted on, such as changing a vendor’s bank details, releasing a payment, or adding a user with admin rights. A phone call to a number already on file is enough.
12. Why does a verification rule matter if our technology is up to date?+
Some losses start with a convincing email rather than a technical break-in. Technology cannot always catch a request that looks legitimate, but a human pause at the right moment can.
13. How do we get staff to follow the rule, even when the request seems to come from the boss?+
Write it down and state clearly that it applies to requests that look like they came from you. Make it equally clear that pausing to verify will never get anyone in trouble.
14. Do we need to put all four controls in place this month?+
No. Spend about twenty minutes marking each control as in place, partly in place, or not yet. That list tells you what to prioritize and budget for next quarter.
15. How can I show an insurer, client, or board that we take security seriously?+
A clear status list of what is in place, what is partial, and what is planned is concrete and easy to share. A written summary from an outside assessment adds credibility.
16. Are small businesses really at risk, or is this mostly a big-company problem?+
Small businesses face the same everyday threats, such as phishing, reused passwords, and unpatched devices, often with fewer people watching for them. The good news is that a few well-chosen controls address a large share of that risk.
17. What does the free 30-minute IT assessment cover?+
It covers the four controls in this article plus your backups, your Microsoft 365 setup, and your network. You get a written summary with priorities and plain pricing.
18. Is the assessment a sales presentation?+
No. It is a plain-English review of where you stand, designed to give you a clear priority list.
19. What is the free lunch-and-learn, and who can book one?+
It is a no-cost session of about thirty minutes, with time for questions, for a local chamber, Rotary club, or business group. It walks through these four controls in plain English. Call (830) 515-4151 to book.
20. Does CMIT Solutions require a long-term contract, and which areas do you serve?+
There are no long-term contracts. CMIT Solutions of San Marcos and New Braunfels works with businesses across San Marcos, New Braunfels, Kyle, Buda, McQueeney, and Seguin. Call (830) 515-4151 and we respond within 2 business hours.
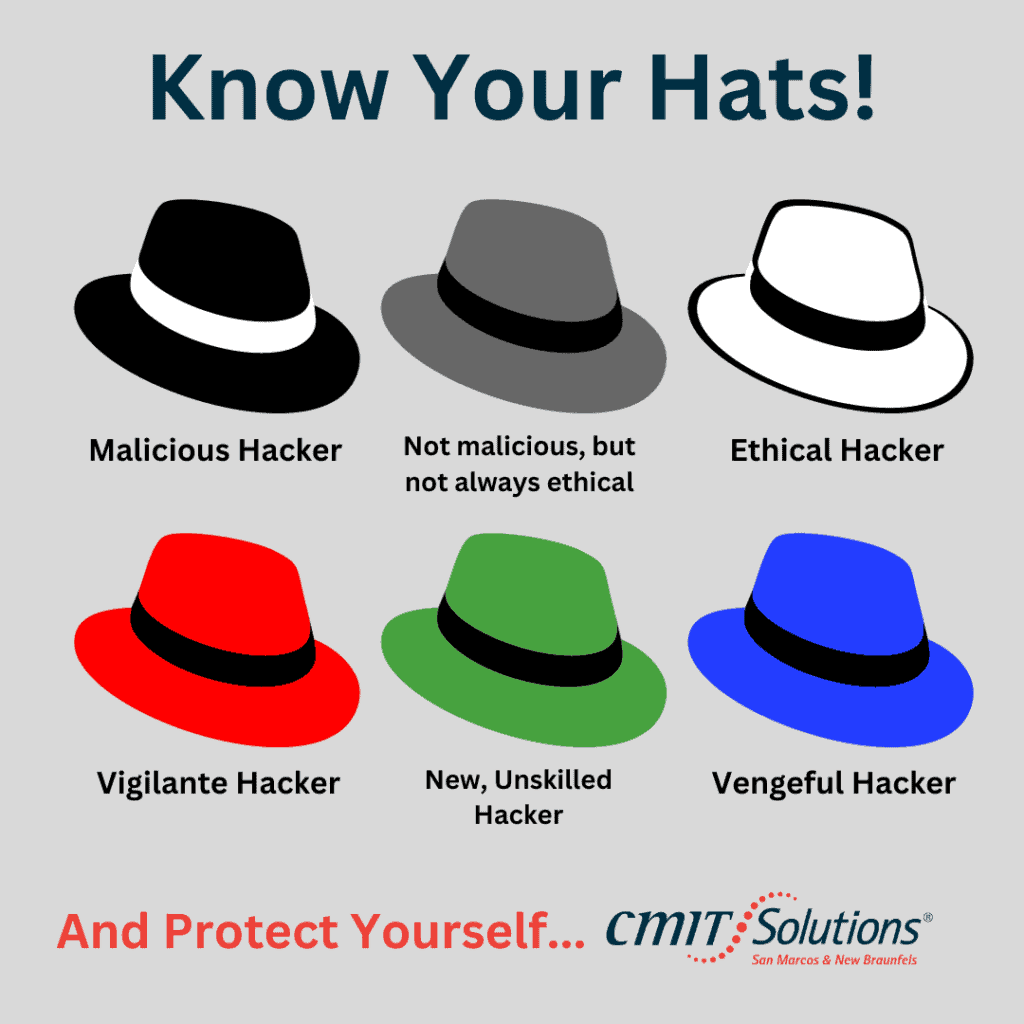
Do you ever wonder who is behind all those cyberattacks that steal private information or cause mayhem online? Well, there are many different types of hackers out there, from black hats to red hats and everything in between.