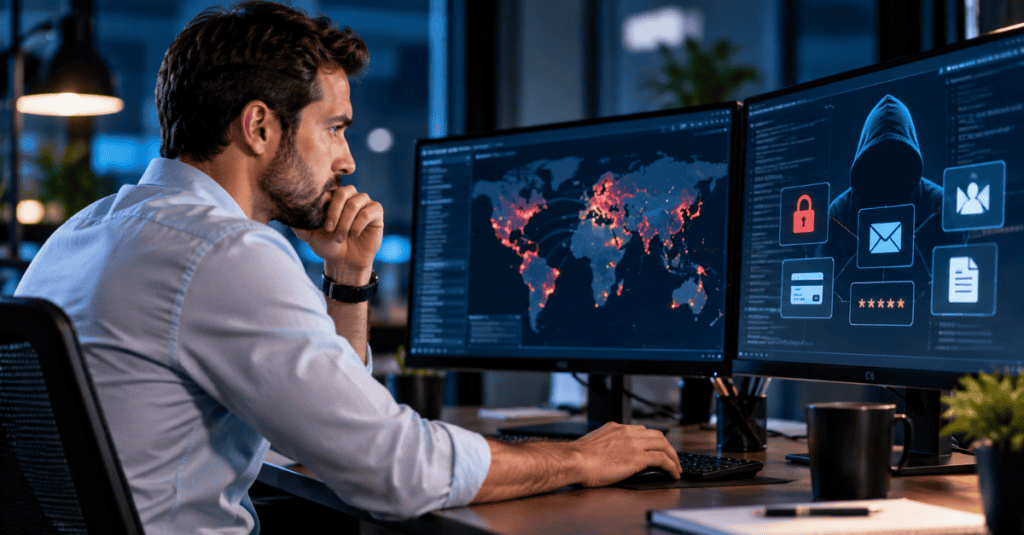
Most business owners never expect to hear their company’s name mentioned in a criminal marketplace. Yet every day, stolen usernames, passwords, customer records, and internal documents are bought, sold, and traded in hidden corners of the internet. By the time a company learns about a breach through a suspicious login, a fraudulent wire request, or a ransom note, the stolen data may have been circulating for weeks or even months.
At CMIT Solutions of Austin Downtown and West, we talk with local business leaders about this problem regularly, and the same questions keep coming up. What exactly is the dark web? What can monitoring actually find? Does it stop attacks, or only report them? This guide answers those questions in plain language. You will learn how dark web monitoring works, what types of data it detects, where its limits are, and how it fits into a broader security program supported by a trusted Austin IT partner.
The Short Answer
Dark web monitoring is a service that continuously searches criminal forums, marketplaces, leak sites, and breach databases for your company’s exposed data, then alerts you so you can act before criminals do. It matters because stolen credentials remain one of the easiest ways for attackers to break in. Monitoring will not stop a breach by itself, and it cannot delete stolen data, but it shortens the time between exposure and response. That gap is often the difference between a simple password reset and a major incident.
What Is the Dark Web?
The internet has layers, and the terms are often confused:
- Surface web: Content that search engines index, such as news sites, company websites, and public social media.
- Deep web: Content behind logins or paywalls that search engines do not index, such as email inboxes, banking portals, and internal company systems. Most of it is perfectly legitimate.
- Dark web: A small portion of the internet that requires special software, such as the Tor browser, to access. It offers anonymity, which has legitimate uses for privacy and journalism, but it also hosts criminal marketplaces and forums.
The dark web is not illegal to visit, and not everything on it is criminal. The concern for businesses is narrow and practical. Criminals use these anonymous spaces to sell stolen data, advertise access to compromised networks, and publish information taken during ransomware attacks. Because these spaces are hidden from ordinary search tools, you cannot check them yourself with a quick search. Browsing criminal marketplaces on your own is also risky, both for your devices and for your legal exposure.
What Is Dark Web Monitoring?
Dark web monitoring is a security service that scans hidden sources for information tied to your organization. Instead of waiting for a breach to reveal itself, it looks for early signals that your data is already in criminal hands.
A typical service tracks items you provide, such as:
- Company email domains
- Employee email addresses
- Executive names and titles
- Customer identifiers where appropriate
- Brand names, product names, and IP ranges
- Payment card or account details you choose to protect
When the service finds a match, it generates an alert describing what was exposed, where it was found, and how urgent the risk appears. The value of the service depends on how quickly you receive that alert and how well your team responds.
What Dark Web Monitoring Actually Finds
Understanding the types of findings helps you understand the value. Common discoveries include:
- Compromised credentials: Email and password pairs from breaches of third-party sites where employees used their work email. This is the most frequent finding.
- Infostealer logs: Data harvested by malware that quietly collects saved passwords, browser cookies, and session tokens from infected devices.
- Personal information: Names, addresses, phone numbers, dates of birth, and government identifiers belonging to employees or customers.
- Financial data: Payment card numbers, bank details, and invoice information.
- Intellectual property: Source code, contracts, designs, pricing sheets, and internal documents.
- Access for sale: Listings from criminals who sell remote access to corporate networks, often called initial access brokers.
- Ransomware leak posts: Announcements naming a victim and publishing stolen files when a ransom is not paid.
- Brand and executive mentions: Discussion of targeting your company, impersonating your leaders, or planning fraud against your customers.
A single exposed password may look minor. In practice, criminals combine small pieces. An email address from one breach, a reused password from another, and a job title from a public profile can be enough to craft a convincing attack.
How Your Data Ends Up on the Dark Web
Data does not reach criminal markets by accident. It usually arrives through one of these paths:
- Third-party breaches: An employee signs up for an outside service using a work email. That service is breached, and the credentials are dumped online.
- Phishing: Deceptive messages trick users into entering passwords on fake login pages. Attackers increasingly use automation to write persuasive messages, which is why AI phishing emails are harder to spot than the clumsy scams of the past.
- Infostealer malware: Malicious software on a personal or work device captures saved logins and session cookies.
- Direct network intrusions: Attackers who break into a network copy files and then sell or publish them.
- Vendor exposure: Misconfigured storage, careless sharing, or a supplier with weak controls leaks information that belongs to you.
- Social engineering: Attackers manipulate staff by phone, text, or chat, and the growth of AI social engineering makes these approaches more believable.
Notice that many of these paths involve human behavior and personal devices, not just company servers. That is why monitoring works best alongside training and device controls.
Why Dark Web Monitoring Matters for Your Business
Exposed data becomes dangerous quickly. Here is what can follow:
- Account takeover: Criminals test stolen passwords across email, cloud, banking, and vendor portals. This technique, called credential stuffing, succeeds because people reuse passwords.
- Business email compromise: With access to a mailbox, attackers watch conversations, then send fraudulent payment instructions that look legitimate.
- Ransomware entry: Stolen access often becomes the first step in a larger attack. The rise of ransomware targeting SMBs shows that smaller firms are no longer overlooked.
- Customer harm and liability: If client data is exposed, you may face notification duties, legal claims, and lost trust.
- Regulatory exposure: Industries handling health, financial, or legal data face strict expectations about protecting information.
- Reputation damage: Clients rarely distinguish between a breach caused by your system and one caused by a vendor. They remember that their data was exposed.
The threat landscape keeps shifting, and growing cyber risks put more pressure on lean teams every year. Early awareness is usually far less costly than responding to a full incident, and understanding ransomware recovery timelines shows how much disruption a single missed warning can create.
A Hypothetical Example
Consider a 40-person professional services firm. A bookkeeper signs up for an online design tool using her work email and a password she also uses for her company mailbox. Months later, the design tool suffers a breach, and her credentials appear in a criminal forum.
Without monitoring, nobody notices. An attacker tries the password against the firm’s email system, gets in, and quietly reads invoice threads for two weeks. Then a client receives a message with new bank details, and a payment goes to the wrong account.
With monitoring, the credential exposure triggers an alert within hours or days. The firm resets the password, revokes active sessions, checks the mailbox for suspicious rules, and confirms that no one accessed the account. The incident ends as a routine ticket instead of a financial loss. The technology did not prevent the third-party breach, but it created the window that let the firm respond first.
How Dark Web Monitoring Works
Behind the alerts, most services follow a similar process:
- Collection: Automated tools and human analysts gather data from forums, marketplaces, chat channels, paste sites, leak sites, and breach dumps.
- Matching: The service compares collected data against your monitored domains, accounts, and identifiers.
- Verification: Analysts or algorithms reduce false positives by checking whether the data looks genuine and recent.
- Alerting: You receive a notification that describes the exposure and its severity.
- Guidance: Better services recommend next steps, such as forced password resets or session revocation.
Quality varies widely. Some tools simply check public breach lists, while stronger platforms combine automated collection with human intelligence on closed communities. Monitoring is most valuable when it is not a standalone dashboard but part of continuous cybersecurity monitoring that connects alerts to real response actions.
What Dark Web Monitoring Cannot Do
Honest expectations prevent disappointment. Dark web monitoring has clear limits:
- It cannot remove stolen data. Once information is published, it is copied and redistributed.
- It cannot prevent the original breach. It detects exposure after the fact.
- It cannot see everything. Invitation-only forums and encrypted chat groups may be out of reach.
- It may lag. Data can circulate privately before it reaches a place that monitoring covers.
- It may generate noise. Old breaches can trigger alerts about credentials that no longer work.
- It does not fix the underlying cause. An alert about a reused password does not change password habits.
Think of monitoring as a smoke detector. It tells you something is wrong quickly, but it does not put out the fire, and it does not replace the sprinklers.
What to Do When an Alert Arrives
A monitoring alert is only useful if someone knows what to do with it. A practical response looks like this:
- Confirm the exposure. Identify which account, system, or data set is affected and whether the credential is still active.
- Reset credentials immediately. Force a password change and revoke active sessions and tokens, because stolen cookies can bypass passwords.
- Enforce multi-factor authentication. Stolen passwords lose much of their value when a second factor is required.
- Review recent activity. Check sign-in logs, mailbox rules, forwarding settings, and file access for suspicious behavior.
- Scan the source device. If infostealer malware is suspected, isolate and clean the affected device.
- Check for reuse. Ask whether the same password was used elsewhere and reset those accounts too.
- Notify the right people. Inform leadership and, where needed, legal counsel, insurers, or affected clients.
- Document and learn. Record what happened and update policies to prevent repeats.
Speed matters most in the first hours, and a prewritten playbook removes guesswork when pressure is high. When employees report something odd, responsive IT support ensures that a report becomes action instead of a forgotten email.
Which Businesses Face the Most Risk?
Every business holds data that criminals want, but some sectors face extra pressure:
- Law firms: Client confidences and case files are valuable, which explains why law firm cybersecurity is a growing concern.
- Healthcare practices: Patient records are rich in personal detail, and patient data protection is central to both trust and compliance.
- Financial and accounting firms: Tax records, account numbers, and payment information make attractive targets, so financial data security needs consistent attention.
- Real estate and title companies: Wire transfer details and closing timelines invite payment fraud.
- Construction and engineering firms: Bids, blueprints, and vendor payment details are useful for fraud and competitive espionage.
- Startups and professional services: Rapid hiring and many cloud tools create a wide credential footprint.
Small and midsize companies are often targeted precisely because attackers assume their defenses are thinner. If your firm fits any of these categories, monitoring is not a luxury. It is a practical check on risks you already carry.
Building a Layered Defense Around Monitoring
Monitoring works best as one layer in a broader program. Consider how these pieces fit together:
- Strong authentication: Deploy biometric MFA solutions so stolen passwords alone do not grant access.
- Least privilege access: Apply a zero trust model that verifies every user and device before granting access.
- Identity controls: Adopt an identity security approach that centralizes accounts, permissions, and offboarding.
- Threat detection and response: Use modern MDR solutions so suspicious activity is investigated around the clock.
- Device protection: Close endpoint security gaps by managing patches, encryption, and antivirus on every device.
- Personal device policies: Reduce BYOD security risks with clear rules for employee-owned phones and laptops.
- Human awareness: Build employee cyber awareness through short, regular training and phishing simulations.
- Recoverability: Maintain reliable data backup with tested restores so a breach does not become a shutdown.
Cloud accounts are common targets, so secure cloud services with conditional access and logging are essential. Email and collaboration suites hold enormous amounts of sensitive data, so configuring business productivity applications securely closes many easy doors. Voice, video, and chat tools also carry credentials, which means your unified communications platform deserves the same controls. Segmentation and monitoring from network management solutions limit how far an intruder can move if one account is compromised.
A provider of cybersecurity protection services can bundle many of these layers into a single program, while proactive managed IT keeps patching, monitoring, and user management consistent day to day. Frameworks give structure to all of it. Many Austin businesses use the NIST cybersecurity framework to organize identify, protect, detect, respond, and recover activities so nothing is left to chance.
The Compliance Angle
Dark web findings can trigger legal and contractual duties. Depending on your industry, exposed data may involve state breach notification laws, HIPAA obligations, client agreements, or cyber insurance conditions. Documenting how you detected an exposure and how quickly you responded demonstrates due diligence.
Compliance support services help translate these obligations into written policies, incident response plans, and audit-ready evidence. With those pieces in place, an alert becomes a managed event rather than a legal surprise.
How to Choose a Dark Web Monitoring Solution
Not every monitoring service is equal. Ask these questions before you buy:
- What sources are covered, including forums, marketplaces, leak sites, and infostealer logs?
- Are alerts verified by analysts or purely automated?
- How quickly are new findings reported?
- Can the service track executives and key accounts, not just the main domain?
- What guidance and remediation support come with each alert?
- How does it integrate with your identity, endpoint, and ticketing tools?
- What reporting can you share with clients, auditors, or insurers?
- Is pricing predictable as your headcount grows?
Buying decisions also involve licensing and vendor coordination. IT procurement support helps compare options, avoid overlapping tools, and negotiate fair terms.
Common Mistakes to Avoid
- Treating alerts as informational: An alert without an owner and a deadline is just noise.
- Monitoring only the main domain: Executives, finance staff, and administrators need extra attention.
- Ignoring old breaches: Passwords from years ago may still be reused in current accounts.
- Relying on monitoring alone: Detection without prevention leaves gaps.
- Skipping multi-factor authentication: This single control blunts many stolen credential attacks.
- Forgetting vendors: A supplier’s breach can expose your data even if your systems are secure.
- Never testing the response: A plan that has not been practiced tends to fail under stress.
A Simple 30-Day Starting Plan
- Week 1, Scope: List your domains, key accounts, and critical systems. Assign an owner for alerts and decide who approves urgent changes.
- Week 2, Baseline: Turn on monitoring, review the first findings, and reset any exposed credentials.
- Week 3, Harden: Enforce multi-factor authentication, review administrator accounts, and remove unused access.
- Week 4, Train and rehearse: Brief employees on phishing and password habits, then run a short tabletop exercise using a sample alert.
If you want help turning the plan into a longer roadmap, IT guidance services can connect monitoring to budgets, priorities, and long term security goals.
Turning Dark Web Awareness Into Real Protection
Dark web monitoring will not make headlines, but it quietly solves a hard problem: knowing when your information has already left your control. It reveals exposed credentials, leaked files, and access for sale, and it gives you time to act before a small exposure becomes a costly incident. Its real power appears when it connects to strong authentication, trained employees, tested backups, and a clear response plan.
The team at CMIT Solutions of Austin Downtown and West helps local businesses put these layers in place, from monitoring and response to compliance-ready policies and everyday IT support. If you want to know what criminals may already have about your company and how to close the gaps, schedule a consultation and get a practical plan built around your business.
“`html
Frequently Asked Questions