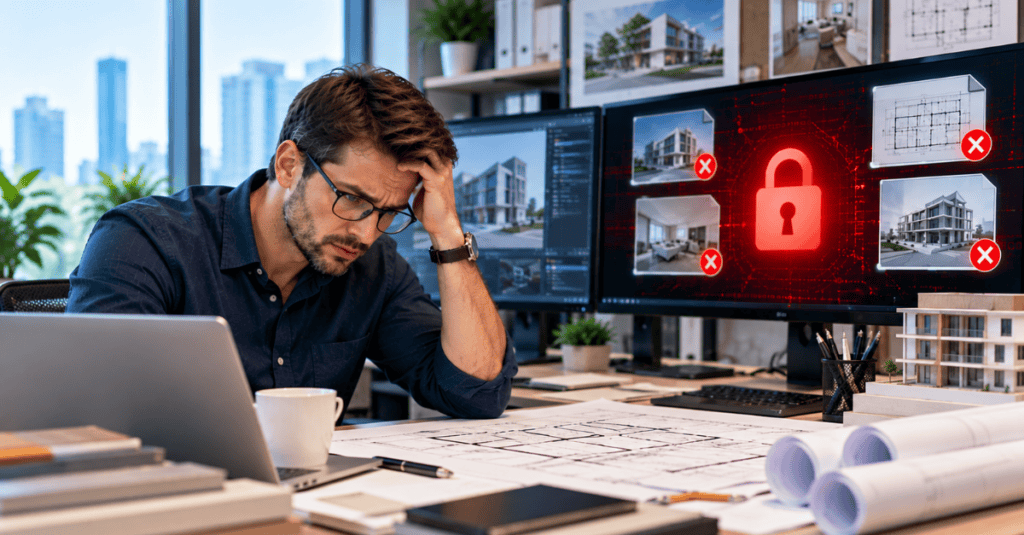
It starts with something small. A file will not open. Then another. Within minutes, an entire folder of client renderings, floor plans, and vendor specifications displays a ransom note instead of the work a team spent weeks producing. For most businesses, a ransomware attack is a disruption. For a design firm, it can feel like watching months of creative and financial investment disappear in real time.
Design firms are uniquely vulnerable to the fallout of a ransomware incident because so much of what they produce cannot simply be recreated from memory. A rendering package reflects specific client conversations, revisions, and creative decisions made over weeks or months. A locked project folder the night before a client presentation is not just an inconvenience. It can mean losing the client relationship entirely. This guide walks through exactly what happens when a design firm loses access to its project files, what the first hours and days actually look like, and how firms can prepare so that an attack becomes a manageable disruption rather than a business-ending event.
Understanding How Ransomware Actually Reaches a Design Firm
Ransomware rarely arrives through some dramatic, sophisticated breach. Most attacks start with something mundane: an employee clicking a link in a convincing email, a compromised password reused across multiple accounts, or an outdated piece of software with a known vulnerability nobody patched. Understanding evolving ransomware tactics helps explain why these attacks continue to succeed even against firms that consider themselves reasonably careful.
Design firms face specific exposure points that other businesses may not think about as often. Contractor and vendor collaboration tools, personal devices used to review renderings from a client site, and large file-sharing platforms that were never fully vetted for security all create additional entry points beyond the firm’s core network.
The broader trend behind small business ransomware risk shows that attackers increasingly target smaller firms specifically because they assume, often correctly, that security defenses will be weaker than at a large enterprise.
The First Hour: What Actually Happens
When a ransomware attack hits, the first hour sets the tone for everything that follows. Files begin displaying error messages or become visibly renamed with unfamiliar extensions. A ransom note typically appears, either as a text file scattered across folders or as a full-screen message demanding payment in exchange for a decryption key.
For a design firm, this moment often coincides with the worst possible timing. It might be the morning of a client presentation, the week before a major installation deadline, or during an active collaboration with a fabricator waiting on final specifications. The initial instinct is often panic, but the decisions made in this first hour matter enormously for how the rest of the incident unfolds.
The right first steps include:
- Disconnecting affected devices from the network immediately to prevent further spread
- Avoiding the temptation to power off infected machines completely, since this can sometimes destroy forensic evidence needed later
- Notifying whoever manages the firm’s IT and security response, whether internal staff or an outside partner
- Documenting what was observed, including any ransom note details, without deleting anything
The First Day: Assessing the Damage
Once the immediate spread is contained, the real assessment begins. This is where the difference between a firm with tested backups and one without becomes painfully clear. A firm with reliable, tested backup systems can begin planning a restoration timeline almost immediately. A firm without one faces a much harder set of decisions.
Key questions that need answers quickly include:
- Which specific project folders and files were affected
- Whether backups exist for those files, and how recent the most recent clean backup actually is
- Whether there is any indication that data was copied or stolen before encryption occurred, not just locked
- Which active client deadlines are at risk based on what was affected
This is also the point where many firms realize that having backup gaps overlooked for months or years turns what should be a manageable recovery into a genuine crisis. A backup system that was never tested is essentially an unknown quantity at exactly the moment a firm needs certainty most.
The Uncomfortable Question: To Pay or Not to Pay
Every firm facing a ransomware attack eventually confronts the question of whether to pay the ransom. This decision carries legal, financial, and ethical complexity, and there is no universally correct answer. What is clear is that paying does not guarantee file recovery, and it does not undo any data that may have already been copied and could still be leaked regardless of payment.
Firms with strong, tested backups are in a far better negotiating position, even if they choose not to negotiate at all, because restoration from backup removes the pressure to pay simply to regain access to files. This is exactly why bouncing back from attacks planning matters so much before an incident occurs, rather than being figured out for the first time under active pressure.
What Gets Lost Beyond the Files Themselves
The direct loss of project files is only part of the damage a ransomware incident causes. Design firms in particular face several layers of secondary impact that are easy to underestimate.
- Client trust erodes quickly if a firm cannot explain what happened or when work will resume
- Vendor and contractor relationships strain when specifications or timelines are delayed without clear communication
- Staff productivity drops significantly during recovery, even for projects not directly affected by the attack
- Reputational damage can spread through referral networks, which matter enormously in design industries that rely heavily on word of mouth
- Recovery costs, including any outside forensic or recovery specialists, add up quickly even without a ransom payment
Firms sometimes ask themselves too late what would actually happen if they got hacked tomorrow. Working through that scenario honestly, before it happens, reveals gaps that are far easier to fix in advance than during an active crisis.
Why Some Firms Never Fully Recover
Not every business survives a serious ransomware incident. Research on why firms are sometimes one cyberattack away from closing shows that the combination of direct recovery costs, lost client relationships, and operational disruption can be enough to permanently damage a small firm’s financial stability.
Design firms are not immune to this risk simply because their product is creative rather than transactional. In some ways, the risk is higher, since the specific, custom nature of design work makes lost files harder to recreate quickly compared to more standardized business data.
Why Human Error Makes This Risk Even Higher
It is tempting to think of ransomware purely as an external attack, but human error factor considerations matter just as much. A single employee clicking a convincing phishing link, reusing a password across personal and business accounts, or plugging in an infected personal device can be enough to trigger an incident that no firewall could have prevented.
This is particularly relevant for design firms with a mix of full-time staff, freelancers, and contractors, each bringing their own devices and habits into contact with firm systems. A firm that has not reviewed its technology setup recently may be carrying more risk than realized, a pattern explored in research on outdated design firm IT practices that quietly accumulate over years of incremental decisions.
Building Backup Systems That Actually Work When Needed
The single most important defense against the worst outcomes of a ransomware attack is a backup system that has been properly built and, critically, tested. Many firms assume their backups work simply because a backup job appears to run on schedule. The only way to actually know is through regular restore testing.
A resilient backup strategy for design firms includes:
- Backups stored completely separate from the primary network, so an attack that spreads across connected drives cannot reach them
- Multiple recovery points, allowing restoration to a specific point before the attack occurred rather than just the most recent save
- Automated, frequent backup schedules that account for how quickly active project files change
- Documented, tested restore procedures that staff can execute quickly under pressure
Reliable data backup solutions built specifically around large creative files give firms genuine confidence that a ransomware incident, while still disruptive, does not have to mean permanent loss of project work.
Detecting Threats Before They Spread
The best outcome in any ransomware scenario is catching the threat before it encrypts anything at all. This requires moving beyond basic antivirus software toward genuine, ongoing visibility into network activity. Many attacks sit quietly inside a network for days or weeks before activating, similar to the pattern described in silent office threats research, where the most damaging risks rarely announce themselves clearly.
Modern constant threat monitoring systems flag unusual file activity, such as a large number of files being renamed or encrypted in a short window, giving firms a chance to isolate the threat before it spreads across the entire project archive.
Keeping Systems Stable Reduces Overall Risk
A well-maintained, properly patched network is inherently harder to compromise than one running outdated software with known vulnerabilities. Firms benefit from eliminating network downtime practices that keep systems updated and monitored continuously, rather than only addressing problems after something has already gone wrong.
This proactive approach also pays off in everyday operations, not just during a crisis. Firms focused on reducing costly downtime tend to catch smaller technical issues before they compound into larger vulnerabilities that an attacker could eventually exploit.
Shifting From Reactive to Predictive Security
Firms that treat cybersecurity as something to think about only after an incident occurs are consistently the ones hit hardest when an attack finally happens. A more effective approach involves a genuine shift toward a predictive IT approach, where potential issues are identified and addressed before they escalate into a full incident.
This mirrors the broader industry recognition reflected in ongoing work around staying resilient 2026 planning, where resilience is treated as an ongoing operational discipline rather than a one-time project completed and forgotten.
Managing the Growing Number of Tools and Access Points
Design firms often work with a wide range of outside vendors, fabricators, and collaboration platforms, each representing a potential entry point for an attack. This connects to the broader challenge of growing vendor sprawl, where the number of connected tools and accounts expands faster than most firms can realistically track or secure.
Regularly reviewing which vendors and contractors still have active access to shared project systems, and removing access as soon as it is no longer needed, closes off entry points that firms often forget even exist.
Evaluating Cloud Security Before Trusting It Fully
Many design firms have moved large portions of their project files to cloud storage platforms, which offer real benefits but require proper configuration to avoid becoming a new vulnerability. Running through a monthly cloud checklist helps ensure that the platforms holding sensitive client renderings and specifications are actually configured with the security settings they are capable of providing.
Firms growing their project volume also benefit from scaling cloud resources in a way that keeps pace with increasing file sizes and collaboration needs, since a strained, improperly scaled system is often more vulnerable than one built with adequate capacity from the start.
Preparing Now for the Next Disruption
Firms that have never experienced a ransomware attack sometimes assume it will not happen to them. This assumption is increasingly risky given how broadly attackers now target small and mid-sized businesses. Reviewing what smart firms are doing to preparing next disruption scenarios shows a consistent pattern: firms that invest in preparation before an incident recover significantly faster and at lower cost than those figuring it out for the first time during an active crisis.
Design firms handling client deposits and vendor payments should also stay alert to related risks, including the rise of AI fraud escalation schemes that sometimes accompany or follow a broader security incident, particularly when attackers use stolen information to impersonate the firm or its vendors.
Building an Incident Response Plan Before It Is Needed
A written incident response plan turns a chaotic, high-stress situation into a series of clear, practiced steps. Every design firm, regardless of size, benefits from having one in place before an attack occurs rather than improvising during the actual event.
An effective plan should include:
- A clear chain of command defining who makes decisions during an active incident
- Contact information for outside IT, legal, and insurance resources, kept accessible even if primary systems are down
- Client communication templates prepared in advance, ready to adapt to the specific situation
- A documented backup restoration procedure staff can follow without needing to figure it out under pressure
- A post-incident review process to identify exactly how the attack occurred and close that specific gap
How a Managed IT Partner Changes the Outcome
Firms working with a dedicated technology partner consistently recover faster and with less damage than those managing security entirely on their own. A managed IT services relationship provides ongoing monitoring, patching, and backup management that significantly reduces the odds of a successful attack in the first place.
Dedicated cybersecurity service solutions extend that protection specifically toward the threats most likely to target creative and project data, while responsive reliable IT support ensures a firm has somewhere to turn immediately if something does go wrong, rather than scrambling to find help during an active incident.
A stable network management solutions environment supports the kind of continuous monitoring needed to catch threats early, and modern productivity application tools bring built-in security and permission features that reduce risk compared to older, disconnected file-sharing methods. For firms that need reliable communication with clients and vendors during any disruption, unified communication systems keep essential conversations running even if primary systems are affected.
Firms investing in new equipment as part of a broader security upgrade benefit from IT procurement services that ensure new purchases align with the firm’s overall protection strategy. Those unsure of the right level of ongoing support can review available IT service packages to find a plan matched to their size and risk exposure.
Bringing It All Together
A ransomware attack does not have to mean the end of a design firm’s most important client relationships or the permanent loss of months of creative work. The firms that recover well are the ones that prepared before an incident occurred, with tested backups, continuous monitoring, and a clear response plan already in place. CMIT Solutions of Dallas works with design and creative firms to build exactly this kind of preparation, protecting the project files and client relationships that represent a firm’s real value.
If your firm has not recently tested how it would actually recover from a ransomware incident, schedule a consultation to walk through a preparedness plan built around your specific project files and client deadlines.
Frequently Asked Questions