HIPAA requires a risk analysis
The HIPAA Security Rule calls for an accurate, documented risk analysis of electronic protected health information.
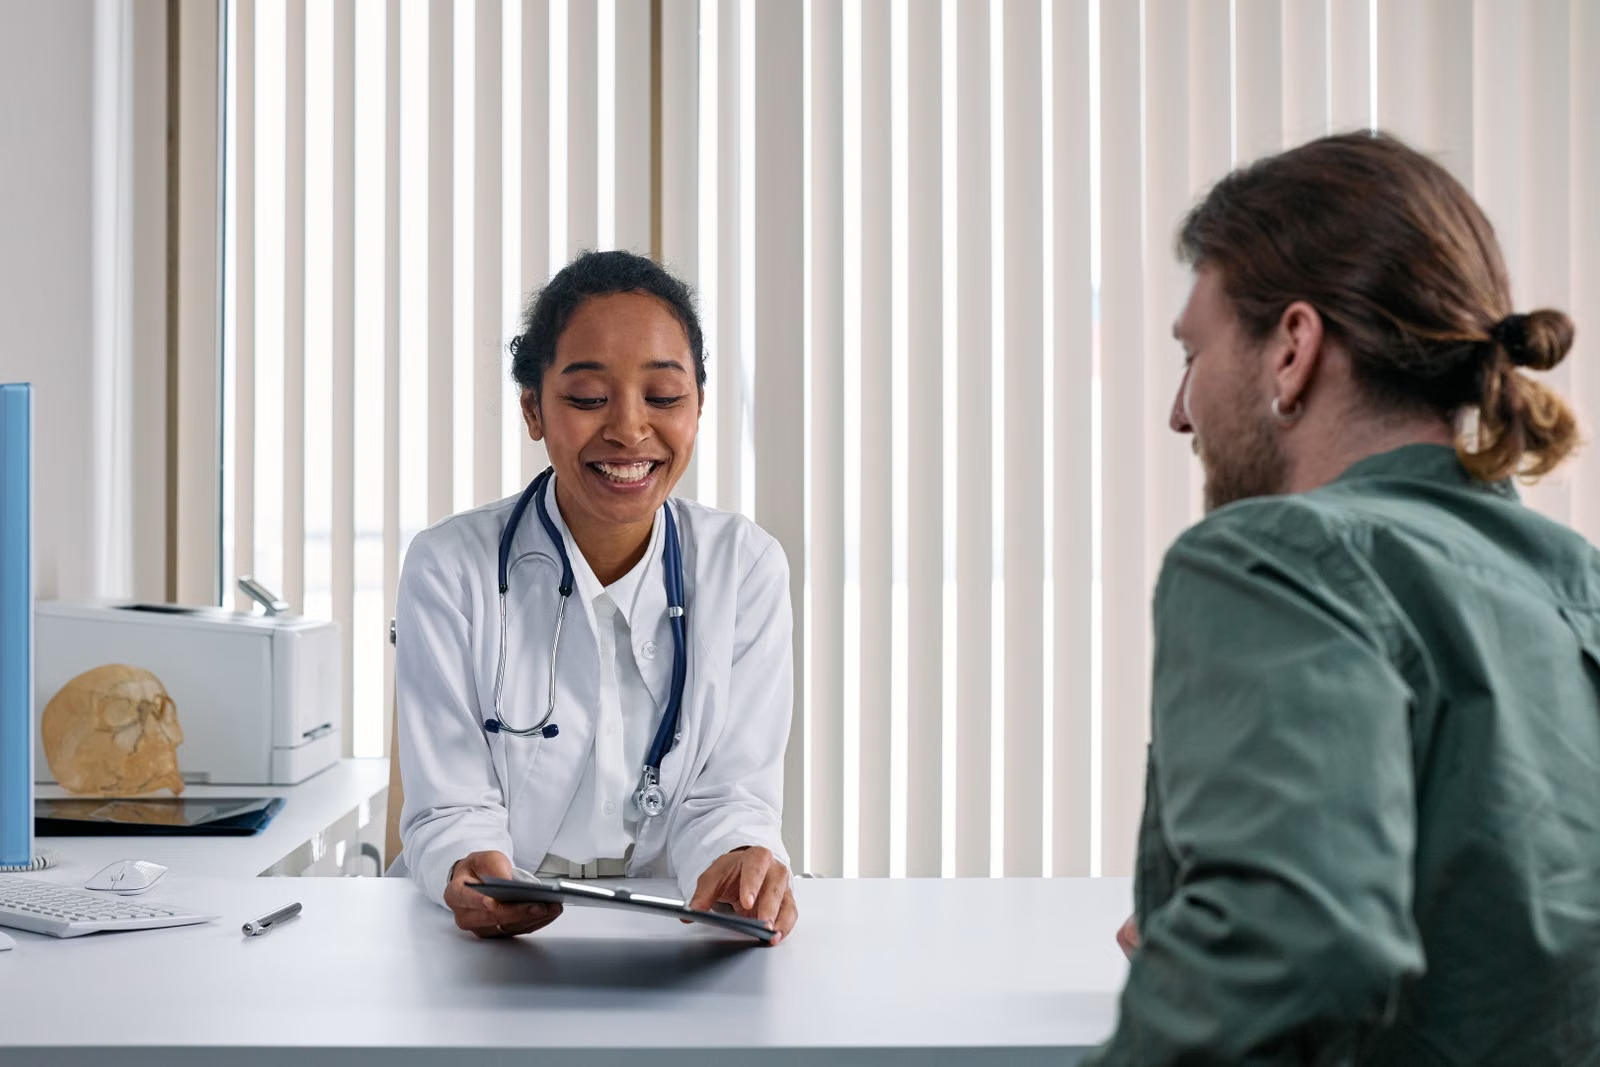
CMIT Solutions Silicon Valley supports medical, dental, behavioral health and specialty practices with managed IT, EHR infrastructure support and security focused on protecting patient information.
Managed IT for a healthcare practice covers monitoring and help desk support, EHR and practice-management infrastructure support, HIPAA Security Rule safeguards such as access management, encryption and audit logging, security risk analysis support, encrypted backups, secure email for protected health information, and vendor agreement coordination where applicable.
Healthcare organizations must protect patient information while keeping clinical systems available and supporting the workflows teams rely on every day.
The HIPAA Security Rule calls for an accurate, documented risk analysis of electronic protected health information.
Disruption to patient records and clinical systems can interfere with appointments and care delivery.
Slow or unavailable records, scheduling and billing systems can interrupt the daily workflow.
Billing services, labs and software vendors need appropriate safeguards and agreements where required.
Before recommending tools, we learn how your practice operates, which systems handle patient information, where the risks are and what a disruption could mean for your staff and patients.
“We strive to be the trusted technology advisor for our clients.”CMIT Solutions Silicon Valley

Our leadership learns your business structure and goals first, so IT becomes part of your strategy instead of an afterthought.

Access to enterprise-grade partners and products through the CMIT Solutions network of 300+ locations and 900+ professionals.

High-quality, proactive service at a predictable monthly price that fits organizations with 5 to 200 users.
One technology partner for practice systems, security, compliance support and planning.
Proactive monitoring and maintenance for workstations, servers and practice networks.
Keep clinical, scheduling and billing systems supported by reliable infrastructure.
Layered protection for patient information across devices, email and cloud systems.
Document security risks, remediation priorities and evidence to support your HIPAA program.
Protect important practice data and prepare to restore systems after disruption.
Design and manage networks that support clinical systems and protect practice traffic.
Every managed IT plan includes these protections, so the basics are covered.
 EDREndpoint detection and response on every device
 Email securityFiltering for phishing, malware and impersonation
 DNS filteringBlocks malicious and unwanted websites
 Access managementControlled accounts, permissions and directories
 Backup validationBackups checked so restores actually work
 Disaster recovery planA written plan to get you running again
Your practice is responsible for its compliance program. Technical safeguards, documentation and vendor oversight can support that program; the requirements that apply depend on your organization and activities.
| Standard | What it asks of you | IT controls that may support it |
|---|---|---|
| HIPAA Security Rule | Administrative, physical and technical safeguards for electronic protected health information, including a documented risk analysis. | Risk analysis support, access control, audit logging, encryption and workforce security measures. |
| HITECH breach notification | Notification obligations may apply after a breach of unsecured protected health information. | Incident response planning, system logs, backup controls and support for evidence gathering. |
| 42 CFR Part 2 | Additional confidentiality requirements may apply to records maintained by covered substance use disorder programs. | Role-based access, permission reviews and careful handling of applicable records. |
| California Civil Code § 1798.82 | California data-breach notification requirements may apply when qualifying personal information is breached. | Security controls, logging, incident-response planning and support for response documentation. |
Applicability depends on your practice, data and circumstances. CMIT supports technical safeguards and documentation; it does not provide legal advice or certify HIPAA compliance.
 Secure AI
A managed approach to AI adoption can help healthcare teams evaluate approved tools, set data-handling rules and reduce the risk of exposing sensitive patient or business information. Review each tool and workflow before entering protected health information.
Healthcare case studies from across the CMIT Solutions network.

After cycling through IT providers, a North Carolina practice found support that kept up with patient care.

A medical clinic highlights the importance of proactive protection and reliable technology support.

A medical society works with a single IT partner to support physician members and their patients.

Maitjian and Todd Welke bring enterprise technology experience to Bay Area businesses through managed IT, cybersecurity, consulting and compliance support. CMIT Solutions Silicon Valley has served the area since 2009 and combines local service with the resources of the wider CMIT network.
CMIT Solutions Silicon Valley has served growing and emerging businesses in the Bay Area since 2009.
Local service is backed by more than 250 CMIT locations and 900 technology practitioners.
Technical safeguards and documentation can help regulated organizations work toward their security and compliance requirements.
Changes are scheduled around your busiest hours so work keeps moving.
We learn your business and measure your exposure.
A written, prioritized roadmap in plain language.
Changes made outside your busiest hours, with clear communication.
Monitoring, help desk and regular business reviews.
Straight answers to questions healthcare practices ask before changing IT providers.
Talk to our team about your practice's IT, security and support needs.
Ask our teamor call (408) 872-1577Where applicable, business associate agreements should be in place before a service provider handles protected health information. We can review the systems and vendor relationships involved and coordinate the required documentation before work begins.
We can help inventory systems that hold electronic protected health information, assess threats and vulnerabilities, document risks and build a prioritized remediation plan. The covered entity remains responsible for its HIPAA compliance program.
We support the workstations, networks, scanners and integrations EHR systems depend on, and coordinate with the EHR vendor when application-specific support is needed.
We can support medical, dental, behavioral health, physical therapy and specialty practices with managed IT, security and infrastructure support. Additional rules may apply to certain behavioral health records.
Managed IT pricing is agreed after assessing the practice's users, devices, systems and service requirements. The service scope and fees should be confirmed in writing.
The assessment can review networks, devices, backups, Microsoft 365 and existing security controls. Findings are used to identify risks and prioritize practical next steps.
We can help assess and implement relevant technical controls, such as multi-factor authentication, endpoint protection, backups and security documentation, based on the insurer's requirements.
CMIT Solutions Silicon Valley advertises 24/7 help desk and system monitoring for managed services clients. On-site arrangements depend on the issue and service agreement.
CMIT Solutions Silicon Valley serves businesses in San Jose, Campbell, Palo Alto, Stanford, Menlo Park, Redwood City, Pleasanton and surrounding Bay Area communities. The local office is at 900 East Hamilton, Suite 100, Campbell, CA 95008.
Find out where your organization is exposed and exactly what it would take to protect it, in plain language.
Prefer to talk?(408) 872-1577
Visit us900 East Hamilton, Suite 100, Campbell, CA 95008
Short on time?Take the 2-minute risk self-assessment