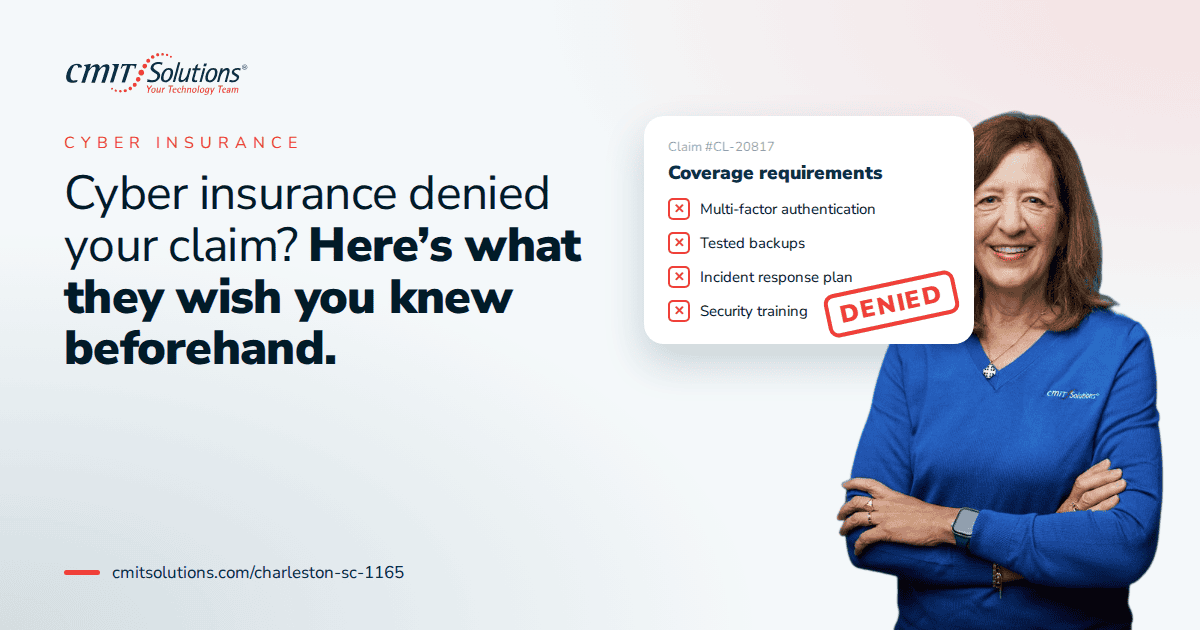
You paid the premium. You checked the box confirming you had security measures in place. Then the breach happened, the claim was filed, and the denial letter arrived instead of the payout. For a lot of business owners, this is the second gut punch of a cyberattack: discovering that the safety net they thought they had wasn’t actually there.
Cyber insurance denials are becoming more common, not because insurers are being unreasonable, but because the gap between what businesses claim on their applications and what’s actually in place has grown too large to ignore. Understanding why claims get denied before you ever need to file one is the only real way to avoid this exact situation.
Why Cyber Insurance Denials Are on the Rise
A few years ago, getting a cyber insurance policy was relatively simple. A short questionnaire, a signature, and coverage was in place. That era is over. Insurers have paid out enormous sums on claims tied to preventable incidents, and they’ve responded by scrutinizing every application and every claim far more closely.
Several factors are driving stricter enforcement:
- Rising frequency and cost of ransomware attacks across every industry
- Insurers discovering that many businesses misrepresented their security posture on applications
- Increased regulatory pressure requiring documented, verifiable security practices
- A broader shift toward treating cybersecurity requirements the same way property insurers treat fire suppression systems
This shift means that a policy purchased two or three years ago, under looser requirements, may no longer reflect what’s actually needed to secure a payout today.
The Most Common Reasons Claims Get Denied
Insurance companies don’t deny claims arbitrarily. Nearly every denial traces back to a specific gap between what was promised on the application and what was actually in place at the time of the incident.
- Misrepresentation on the application. Claiming MFA was enabled company-wide when it was only partially deployed
- Outdated or unpatched systems. Running software long past its supported lifecycle without documented justification
- Missing or untested backups. No proof that backups were regularly tested and verified as recoverable
- Lack of employee training records. No documentation showing staff received security awareness training
- Delayed incident reporting. Waiting too long to notify the insurer after discovering a breach
- Inadequate access controls. Former employees or unnecessary accounts retaining access to sensitive systems
Each of these gaps often traces back to the same underlying issue explored in reactive IT problems, where security practices exist informally but were never properly documented, tested, or enforced.
The Application Process: Where Most Problems Begin
Denials often trace back not to the incident itself, but to how the original insurance application was completed months or years earlier. Business owners, sometimes without full visibility into their own IT environment, answer security questionnaires optimistically rather than accurately.
Common application mistakes include:
- Checking boxes for security measures that were planned but never fully implemented
- Relying on outdated information from an IT vendor who is no longer engaged
- Not involving anyone with technical knowledge in reviewing the application before submission
- Assuming basic antivirus software satisfies broader endpoint protection requirements
Getting an accurate picture of your actual security posture before applying, or renewing, is one of the simplest ways to avoid this problem entirely. A reliable IT support partner can help verify exactly what’s in place before it’s put in writing on an insurance application.
Multi-Factor Authentication: The Requirement That Trips Up the Most Businesses
Almost every modern cyber insurance policy requires multi-factor authentication across critical systems, and it’s one of the most common points of denial when claims are investigated. The problem usually isn’t that MFA is completely absent. It’s that it’s inconsistently applied.
Common MFA gaps that lead to denied claims include:
- MFA enabled for email but not for remote access or administrative accounts
- Legacy systems or older applications excluded from MFA requirements entirely
- Employees given the option to skip MFA for convenience, undermining the policy’s requirements
- No documentation proving MFA was actually enforced at the time of the incident
Attackers have also adapted to basic MFA, using techniques that exploit human patience rather than technical weaknesses, a growing threat covered in threat exposure management. Insurers increasingly want to see not just that MFA exists, but that it’s configured to resist these newer bypass methods.
Backup Requirements: What Insurers Actually Expect
Backups are another area where the gap between assumption and reality causes real problems during a claim investigation. Many businesses assume having backups is enough, without realizing insurers expect proof of testing, isolation, and recoverability.
Insurers typically want to see:
- Backups stored in a location physically and logically separate from the primary network
- Regular, documented testing confirming data can actually be restored
- Immutable backup copies that can’t be altered or deleted by an attacker with network access
- A clear recovery time objective demonstrating how quickly operations could resume
The difference between adequate and inadequate backup strategies is covered in more detail in cloud backup options, where insurers increasingly favor businesses that can demonstrate a tested, layered approach rather than a single backup copy sitting on a local drive.
Why Documentation Matters as Much as the Security Itself
One of the most frustrating realities for business owners is discovering that having good security practices in place isn’t enough on its own. Insurers need proof, and proof requires documentation that many businesses simply never created.
Documentation that insurers commonly request includes:
- Written security policies covering password requirements, access controls, and data handling
- Records of employee security awareness training, including dates and completion rates
- Logs showing patch management and update schedules for critical systems
- Incident response plans outlining specific roles and procedures
- Vulnerability assessment or penetration testing results from qualified providers
Without this paper trail, even a business with genuinely strong security practices can struggle to prove it during a claims investigation. This is where a structured compliance support services approach becomes valuable, turning informal good habits into documented, defensible practices.
The Patch Management Problem
Outdated, unpatched software is one of the most common technical findings during a claims investigation, and it’s often the easiest gap to avoid with proper planning. Insurers frequently ask specific questions about patch management timelines, and inconsistent answers can raise red flags during a review.
Common patch management issues include:
- Critical security patches delayed for weeks or months due to operational disruption concerns
- No centralized system tracking which devices have received which updates
- End-of-life software still running in production without a documented transition plan
- No prioritization framework distinguishing critical security patches from minor updates
Systems running outdated platforms face compounding risk, a concern explored in Windows 11 optimization, where both security and insurance implications increase the longer outdated systems remain in use.
Employee Training: The Requirement Businesses Underestimate
Many cyber insurance applications now include specific questions about employee security training programs, yet this remains one of the most commonly overlooked requirements until a claim is being reviewed.
Insurers generally want evidence of:
- Regular, recurring training sessions, not a single onboarding presentation
- Simulated phishing tests measuring how employees actually respond to real-world scenarios
- Documented completion rates showing consistent participation across the organization
- Updated training content reflecting current attack methods, not outdated material
Since human error remains one of the leading causes of successful cyberattacks, insurers view training records as a meaningful indicator of overall risk. Ongoing security awareness training provides exactly the kind of documented, recurring program insurers are looking for.
Access Control Gaps That Trigger Denials
Insurers pay close attention to who had access to what during an incident, and unnecessary or forgotten access is a frequent finding during claims investigations. A former employee with active credentials, or a vendor account nobody remembered to remove, can be enough to complicate or deny a claim entirely.
Access control practices insurers expect to see include:
- Regular reviews removing access for former employees and unused accounts
- Role-based permissions limiting access strictly to what each position requires
- Separate, more tightly controlled credentials for administrative accounts
- Documented processes for granting and revoking access as roles change
Gaps in cloud application permissions specifically tend to surface during investigations, a risk explored in hidden cloud risks, where forgotten access across scattered platforms often goes unnoticed until it becomes a liability.
Email Security: A Frequent Point of Failure
Email compromise remains one of the most common incident types insurers investigate, and gaps in email security controls frequently surface as contributing factors in denied or reduced claims.
Insurers typically look at:
- Whether email filtering tools were actively catching and blocking phishing attempts
- Whether unusual login activity on email accounts was being monitored
- Whether employees had received specific training on recognizing email-based scams
- Whether financial transaction approval processes required verification beyond email alone
Strengthening these practices is covered in detail in email security tips, where layered email protection significantly reduces both the likelihood of an incident and the risk of a claim dispute afterward.
Timely Reporting: A Requirement Businesses Often Miss
Many policies include strict timelines for reporting an incident to the insurer, and missing these deadlines, even by a few days, can jeopardize an otherwise valid claim. Business owners focused on immediate recovery sometimes delay insurer notification without realizing the consequences.
Best practices for timely reporting include:
- Notifying the insurer as soon as an incident is confirmed, not after recovery is complete
- Understanding the specific reporting deadlines outlined in the policy before an incident happens
- Designating a specific person responsible for insurer communication during a crisis
- Avoiding any public statements or unnecessary system changes before the insurer’s forensic team is involved
Having this process mapped out in advance as part of a broader incident response plan avoids costly delays during an already stressful situation, a gap discussed further in IT outage impact.
How Compliance Requirements Overlap With Insurance Expectations
For businesses in regulated industries, cyber insurance requirements often closely mirror existing compliance obligations. Meeting one set of standards frequently satisfies much of the other, but only if the underlying practices are genuinely in place and documented, a connection covered in audit ready compliance.
Businesses in healthcare, finance, or legal services should confirm:
- Data encryption requirements align with both compliance and insurance standards
- Breach notification procedures satisfy both regulatory and policy timelines
- Access control documentation supports both audit and claims review processes
- Third-party vendor requirements are consistent across compliance and insurance obligations
Network Security Gaps That Complicate Claims
Insurers investigating a claim often look closely at network architecture to understand how far an attack was able to spread and why. Poor segmentation or outdated infrastructure can raise questions about whether reasonable precautions were actually in place.
Key network considerations include:
- Whether the network was properly segmented to limit how far an attack could spread
- Whether firewalls and routers received regular firmware updates
- Whether unusual traffic patterns were being actively monitored before the incident
- Whether remote access points were properly secured and monitored
A properly maintained network management services setup not only reduces the likelihood of a serious incident but also strengthens the documentation available if a claim needs to be filed.
Choosing the Right Security Model for Insurance Requirements
Many insurers now specifically ask about the type of detection and response capabilities a business has in place, distinguishing between basic antivirus, managed detection and response, and broader security platforms. Understanding these differences matters both for actual protection and for satisfying increasingly specific policy requirements, a comparison covered in right security model.
A comprehensive cybersecurity protection services strategy that layers multiple tools together tends to align much more closely with what insurers expect than a single, basic antivirus solution ever could.
Cloud Environments and Insurance Scrutiny
As more business operations move to cloud platforms, insurers have started asking more detailed questions about cloud security specifically, rather than treating it as an extension of traditional on-premises protection.
Areas of increasing insurer scrutiny include:
- Whether cloud backups are configured and tested separately from primary storage
- Whether administrator accounts across cloud platforms carry stronger authentication requirements
- Whether file-sharing permissions are reviewed regularly across every connected application
- Whether the business has full visibility into every cloud tool currently in use
A centralized cloud services solutions approach makes it significantly easier to maintain and document consistent security practices across every platform, which directly supports both prevention and future claims if an incident occurs.
Remote Work Policies and Insurance Requirements
With distributed teams now standard for many businesses, insurers increasingly ask specific questions about how remote access is secured and monitored. Gaps here can complicate a claim just as easily as gaps in traditional office security.
Insurers typically want to confirm:
- Remote access tools require strong, monitored authentication
- Personal devices used for work meet documented minimum security standards
- Remote login activity is actively monitored, not just permitted by default
- Employees have clear policies for handling sensitive data outside the office
Reliable unified communications tools that centralize remote collaboration make it easier to enforce and document these policies consistently across a distributed team.
What to Do Before Your Next Policy Renewal
Rather than waiting for a denied claim to reveal these gaps, businesses can take a proactive approach before their next renewal. A structured review well ahead of the renewal date gives time to close gaps instead of scrambling under deadline pressure.
Steps to take before renewal include:
- Request a full security assessment to verify what’s actually in place versus what’s assumed
- Review the previous application line by line to confirm accuracy against current systems
- Test backups and document the results rather than assuming they work
- Confirm MFA is consistently enforced across every critical system, not just select accounts
- Update incident response and training documentation to reflect current practices
Working with a partner who can provide strategic IT guidance before renewal season helps ensure the application reflects reality, reducing the risk of a denied claim down the road.
Why Bundled IT Support Makes This Easier to Manage
Keeping up with evolving insurance requirements alongside daily IT operations can feel overwhelming for a small business without dedicated staff. Bundled support that combines monitoring, security, backup management, and documentation in one place removes much of that burden, an approach outlined in custom IT packages.
Why Local Expertise Matters When Preparing for Cyber Insurance
Insurance requirements can vary based on industry, region, and specific risk factors, and a generic, one-size-fits-all approach often misses details that matter for businesses operating in a specific market. Local businesses benefit from a partner who understands both the regional threat landscape and the practical realities of running a small or mid-sized company.
CMIT Solutions of Charleston works with businesses across the region to close the exact gaps that lead to denied claims, from MFA configuration to documented backup testing to employee training records. The goal isn’t just passing an application questionnaire. It’s making sure the protection is real, documented, and ready to hold up if it’s ever tested.
Getting ahead of this starts with an honest assessment of where your current setup stands against what your policy actually requires, well before a claim depends on it.
The Bottom Line
A denied cyber insurance claim rarely comes as a random decision. It almost always traces back to a specific, identifiable gap between what was represented on an application and what was actually in place when the incident occurred. MFA that wasn’t fully enforced, backups that were never tested, training that was never documented. Each of these gaps is preventable with the right planning.
The businesses that avoid this outcome aren’t the ones with perfect security. They’re the ones who took the time to verify, document, and maintain what their policy actually requires, long before they ever needed to file a claim.
If you’re not confident your current security practices would hold up during a claims investigation, it’s worth finding out now rather than after an incident. Schedule a consultation to get a clear assessment of where your setup stands against your policy requirements.
Frequently Asked Questions