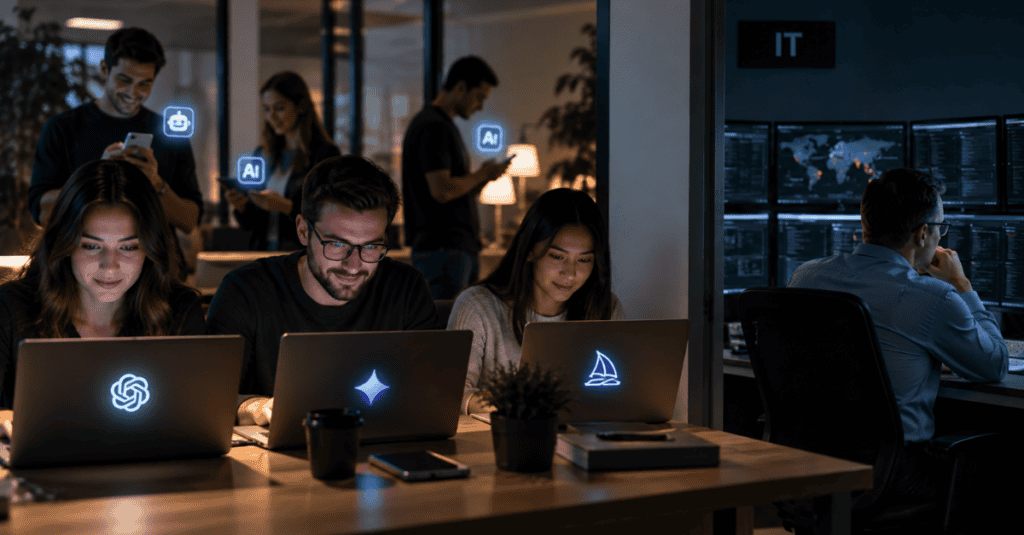
Somewhere in almost every office right now, an employee is pasting a client contract into a free AI tool to get a quick summary. Someone in marketing is using an AI image generator that was never reviewed by anyone in IT. A project manager is running meeting notes through a browser extension that promises to write follow-up emails automatically. None of these tools were approved, budgeted, or even mentioned to leadership. This is shadow AI, and it is spreading through businesses far faster than most IT departments realize.
Shadow AI is the natural evolution of a problem companies have dealt with for years: employees adopting tools outside official channels because they are fast, free, and immediately useful. What makes this wave different is the sheer volume of sensitive data these AI tools can quietly absorb, and how invisible that activity is to the people responsible for protecting company information. This guide breaks down what shadow AI actually looks like, why it has grown so quickly, and what businesses can realistically do about it.
What Shadow AI Actually Means
Shadow AI refers to any artificial intelligence tool or platform used by employees without formal approval, oversight, or visibility from the IT department. It is a subset of a much older concept called shadow IT, which covers any unauthorized software or service running inside a business. The AI version of this problem is growing faster and carrying more risk because these tools often process, store, or learn from whatever data gets fed into them.
Common examples include:
- Free chatbot tools used to draft emails, summarize documents, or answer client questions
- Browser extensions that transcribe and summarize meetings automatically
- AI writing assistants used to edit or generate marketing content and proposals
- Image and design generation tools used without any data handling review
- Personal AI accounts used to analyze spreadsheets or financial data
None of these tools are inherently malicious. Most employees using them are simply trying to work faster. The problem is that almost none of these tools were evaluated for how they store data, whether they train on user input, or what happens to sensitive information once it is submitted.
Why Shadow AI Is Spreading So Quickly
A few forces are converging to make shadow AI far more common than earlier waves of shadow IT ever were.
AI tools are free and instantly accessible. Unlike enterprise software that requires a purchase order and setup process, most popular AI tools can be accessed through a browser in seconds with no cost and no approval needed.
Productivity pressure rewards fast results. Employees under deadline pressure will use whatever tool gets the job done, especially when leadership is simultaneously pushing teams to work faster and do more with the same headcount. This tension is part of the broader shift covered in AI daily operations research, where automation is increasingly expected as a baseline rather than a bonus.
There is no clear line between personal and professional AI use. Many employees already use AI tools in their personal lives and simply carry that habit into work without thinking twice about whether it is appropriate for company data.
Leadership is sending mixed signals. Companies are publicly encouraging AI adoption to stay competitive, covered extensively in discussions around AI business competitiveness, while simultaneously having no formal policy about which tools are safe to use. Employees fill that gap with whatever is convenient.
Why IT Departments Cannot See It Coming
Traditional IT security tools were built to monitor software installations, network traffic, and approved applications. Shadow AI slips past most of these controls for a few specific reasons.
- Many AI tools run entirely in a browser, leaving no software footprint on company devices
- Traffic to popular AI platforms is often encrypted and indistinguishable from normal web browsing
- Employees frequently use personal accounts rather than company-issued logins, making usage invisible to identity management systems
- There is no procurement trail, since most of these tools are free and require no purchase approval
- New AI tools launch constantly, faster than security teams can evaluate and add them to blocklists
This visibility gap connects directly to a challenge many growing companies already face described as vendor sprawl problem, where the number of tools connected to company data grows faster than anyone can realistically track. Shadow AI accelerates that sprawl dramatically, since new tools appear on a near-weekly basis.
The Real Risks Behind Unapproved AI Use
It is tempting to dismiss shadow AI as a minor productivity shortcut, but the risks compound quickly once sensitive information is involved.
Data Leakage and Loss of Control
Once information is submitted to a third-party AI tool, a business generally loses control over where that data goes. Some platforms retain user input to improve their models, meaning proprietary business information, client details, or financial data could end up influencing a system used by competitors or the public. This is a modern version of a risk long documented under accidental data loss, except now the loss happens through a well-meaning employee trying to save time rather than a careless mistake.
Compliance and Regulatory Exposure
Businesses handling regulated data, whether financial records, health information, or client contracts, face serious exposure when that data passes through unapproved tools. This creates compliance risk gaps that often go unnoticed until an audit or incident forces a closer look. A company might have strong data handling policies on paper while shadow AI use quietly undermines them in practice.
Intellectual Property and Confidentiality Risk
Feeding a proprietary business process, a client’s strategic plan, or an internal financial model into a public AI tool can effectively hand that information to a third party outside the protection of any confidentiality agreement. For firms bound by NDAs or client confidentiality requirements, this is a direct contractual risk, not just an internal policy concern.
AI-Enhanced Phishing and Social Engineering
Shadow AI is not just about employees using tools carelessly. Attackers are using the same category of tools to craft far more convincing scams. The trend covered in AI phishing attacks shows how generative tools have made fraudulent emails and messages nearly indistinguishable from legitimate communication, making employee awareness more important than ever.
Fraud Risk Tied to AI-Generated Content
Beyond phishing, businesses are seeing a rise in more sophisticated impersonation attempts, sometimes involving AI-generated voice or writing style mimicry. Understanding how AI driven fraud schemes operate helps businesses train staff to recognize red flags rather than assuming a familiar-sounding request is automatically legitimate.
Why Banning AI Outright Does Not Work
Some businesses respond to these risks by attempting to block AI tools entirely. In practice, this approach rarely succeeds and often backfires. Employees who find a tool genuinely useful will simply find a way around a blanket ban, often by switching to personal devices or personal accounts that are even harder for IT to monitor. This pushes the activity further into the shadows rather than eliminating it.
A more effective approach treats AI adoption the way businesses have learned to treat cloud adoption over the past decade: with structure, visibility, and approved alternatives, rather than prohibition. Companies exploring AI IT management approaches are finding that giving employees a sanctioned, secure AI tool actually reduces shadow AI use, since it removes the incentive to seek out unapproved alternatives.
Building a Shadow AI Governance Framework
A practical governance approach does not require a massive policy document. It requires a few clear, enforceable steps.
- Inventory current AI use. Survey teams honestly about which AI tools they already use, since most shadow AI activity is not malicious and employees will often disclose it if asked directly rather than punitively.
- Define approved tools and use cases. Identify which AI platforms have been reviewed for data handling and security, and clearly communicate which are safe to use for which types of work.
- Set clear boundaries for sensitive data. Establish specific rules about what can never be entered into an AI tool, such as client financial details, health information, or proprietary source code.
- Provide sanctioned alternatives. Employees are far less likely to seek out unapproved tools if a fast, capable, approved option already exists.
- Monitor for new tool adoption. Regularly review network and account activity to catch new AI tools being adopted before they become widespread.
- Update policy on a recurring basis. The AI landscape changes too quickly for a policy to be written once and forgotten. Quarterly reviews are far more effective than an annual policy refresh.
Businesses working through this process often benefit from outside strategic IT guidance to build a framework that fits their specific industry and risk profile rather than adopting a generic template that does not reflect how the business actually operates.
The Role of Data Quality and Trustworthy AI Adoption
Shadow AI is partly a symptom of a bigger gap: many businesses have not yet built a clear, trustworthy path for adopting AI the right way. Before rolling out any sanctioned AI tool, it helps to understand AI data quality requirements, since poor data hygiene undermines even a well-chosen, approved AI platform.
Businesses further along in adoption are also exploring more advanced applications, such as agentic AI insights that automate data analysis tasks. These systems can deliver real value, but they also require even tighter data governance than a simple chatbot, since agentic tools often take autonomous action on the data they access.
Any business unsure of where it currently stands should honestly assess business AI journey progress before assuming shadow AI is not a problem. Even companies that have not formally adopted any AI tools almost certainly have employees using them informally already.
Detecting Shadow AI Without Overreaching
Detecting unauthorized AI use does not require invasive surveillance of every employee action. A layered approach works better and respects reasonable privacy boundaries.
- Reviewing network traffic patterns to identify connections to known AI platforms
- Auditing browser extensions installed across company devices
- Monitoring for large or unusual data transfers to external web services
- Reviewing identity and access logs for accounts connecting to AI services using company credentials
- Encouraging open reporting rather than punitive discovery, since employees are more likely to disclose tool use when they are not afraid of consequences
Modern real-time threat monitoring systems increasingly incorporate the ability to flag traffic to known AI platforms, giving security teams visibility that older monitoring tools simply were not built to provide.
Identity, Access, and the Shadow AI Connection
A significant part of the shadow AI risk ties directly back to identity management. Employees using personal accounts to access AI tools bypass every access control a business has built around its official identity systems. This connects to a larger shift described in digital identity trends research, where businesses are moving toward stronger, more centralized identity verification precisely because so much modern software, including AI tools, now touches sensitive data outside traditional network boundaries.
Requiring single sign-on for any approved AI platform gives businesses at least partial visibility into usage patterns, something that is impossible when employees log in with a personal email address nobody in IT ever sees.
Compliance Considerations Businesses Often Overlook
For businesses operating under specific regulatory frameworks, shadow AI introduces compliance risk that is easy to miss until it becomes a real problem. A useful starting point is reviewing a cloud compliance explained overview, since many of the same principles that apply to cloud data storage apply equally to data submitted into AI platforms hosted in the cloud.
More broadly, businesses should treat growing data protection commitments as inseparable from AI governance rather than as a separate initiative. A data protection policy that does not explicitly address AI tool use is already out of date.
Employee Training Matters More Than Technology
Technical controls alone cannot solve the shadow AI problem, because most unauthorized AI use comes from employees trying to be helpful and efficient, not from malicious intent. Training needs to go beyond a single onboarding session and become part of ongoing security awareness.
Effective training programs typically cover:
- What categories of data should never be entered into any unapproved tool
- How to recognize when a task might involve sensitive client or financial information
- Where to find the list of currently approved AI tools
- How to request evaluation of a new tool an employee wants to use
- What to do if they realize, after the fact, that sensitive data was already entered into an unapproved tool
Businesses in industries facing frequent scrutiny, such as those reviewing cybersecurity challenges dallas firms regularly encounter, benefit from tying AI-specific training directly into their broader security awareness program rather than treating it as a separate, standalone topic.
Building Toward Long-Term Resilience
Shadow AI is not a problem that gets solved once and then goes away. New tools launch constantly, and employee habits shift as quickly as the technology itself. Businesses that treat this as an ongoing part of their overall constant threat resilience strategy are far better positioned than those that address it once and move on.
It also helps to recognize that shadow AI often hides in plain sight, much like the broader pattern described in silent IT threats research, where the biggest risks are frequently the ones nobody is actively looking for because they do not resemble a traditional attack.
How a Managed IT Partner Helps Close the Gap
Most businesses do not have the internal resources to continuously monitor for new AI tools, evaluate their data handling practices, and update policy on an ongoing basis. This is where a managed IT services partnership becomes valuable, providing ongoing oversight rather than a one-time policy document that quickly becomes outdated.
A strong technology partner also brings dedicated cybersecurity service solutions that extend visibility into AI tool usage alongside traditional threats, giving businesses a single, coordinated view of their risk rather than treating AI as a separate, disconnected problem.
For businesses ready to formally adopt AI tools rather than leaving employees to find their own, a well-chosen productivity application tools suite often already includes AI features that have been properly vetted for business use, reducing the temptation to seek out unapproved alternatives entirely.
Ongoing compliance support services also help businesses keep AI governance policies aligned with whatever regulatory requirements apply to their specific industry, since these requirements continue to evolve alongside the technology itself.
Day-to-day, having access to reliable IT support means employees have somewhere to turn when they are unsure whether a tool is safe to use, rather than defaulting to whatever is fastest and most convenient in the moment. A stable, well-managed network management solutions setup also gives security teams the visibility needed to detect unusual traffic patterns tied to unauthorized AI use in the first place.
Businesses evaluating new tools and platforms as part of a formal AI strategy also benefit from IT procurement services that properly vet vendors before adoption, rather than discovering data handling issues after a tool is already embedded in daily workflows. Reliable data backup solutions round out the picture, ensuring that even if sensitive data is mishandled through an AI tool, the business retains clean, recoverable copies of its critical information.
Firms unsure where to start can review available IT service packages to find a support level that matches the scale of their AI governance needs without overcommitting budget to services they are not ready to use.
Bringing It All Together
Shadow AI is not a distant, theoretical risk. It is already happening inside most businesses today, quietly, without malicious intent, and largely invisible to traditional IT security tools. The businesses that manage this well are not the ones that ban AI outright, but the ones that build clear policy, provide safe alternatives, and maintain ongoing visibility into how these tools are actually being used. CMIT Solutions of Dallas works with growing businesses to build exactly this kind of practical, sustainable AI governance framework, one that supports innovation without leaving sensitive data exposed.
If your business is ready to get a clearer picture of how AI tools are actually being used across your team, schedule a consultation to talk through a governance approach built around how your business actually operates.
Frequently Asked Questions