Cyber insurance used to be a simple purchase. A business filled out a short application, answered a handful of general questions, and received a policy within days. That era is over. Insurers have paid out enormous claims tied to ransomware, business email compromise, and data breaches over the past several years, and the industry has responded by tightening underwriting standards dramatically. Today, getting approved for a policy, or renewing one at a reasonable premium, depends heavily on the strength of a company’s actual security posture.
For business owners across Greenville, this shift means cyber insurance is no longer just a financial safety net. It has become a mirror held up to the organization’s technology environment. CMIT Solutions of Greenville works with local businesses navigating this new reality every day, helping them close the gaps that insurers now look for before they will even quote a policy.
This article breaks down why the underwriting landscape changed, what insurers specifically look for, and how businesses can position themselves for approval, better pricing, and fewer denied claims down the road.
The Shift From Simple Applications to Rigorous Underwriting
A decade ago, cyber insurance was a relatively small and loosely regulated corner of the insurance market. Premiums were low, coverage limits were generous, and underwriting was minimal. That changed as ransomware attacks surged and insurers began paying out claims far larger than they had priced for.
Several trends forced the shift:
- Ransomware payouts climbed into the millions for mid-sized businesses, far exceeding original actuarial assumptions
- Business email compromise losses grew steadily as attackers refined social engineering tactics
- Regulatory fines tied to data breaches added new layers of financial exposure
- Supply chain attacks demonstrated that even well-protected businesses could be compromised through vendors
Insurers responded the way any industry does when losses outpace pricing: they raised premiums, lowered coverage limits, and became far more selective about who they insure. What used to be a checkbox exercise is now closer to a security audit.
Why Insurers Care So Much About Security Controls Now
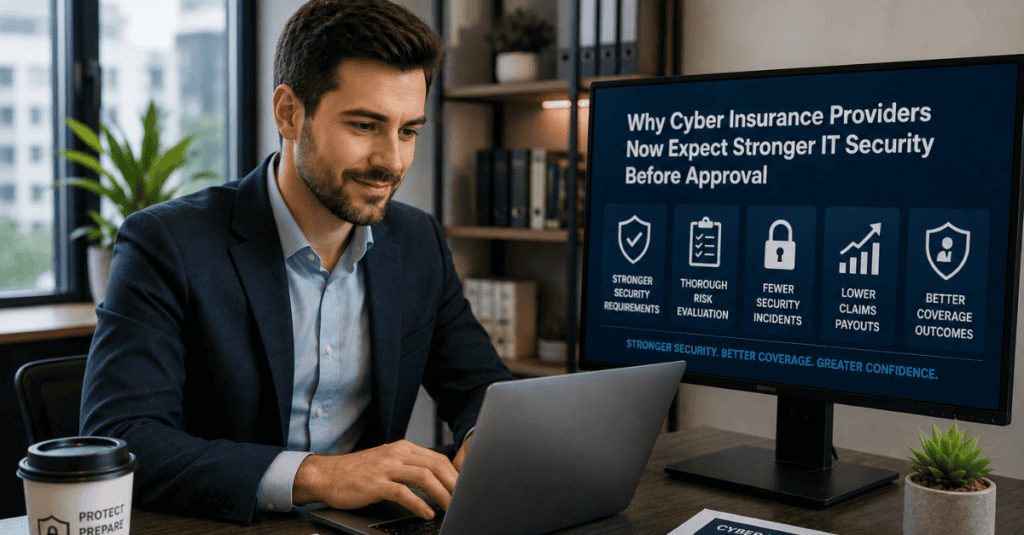
From an insurer’s perspective, cyber risk is directly tied to a company’s technical maturity. A business with outdated software, no formal monitoring, and untrained employees represents a statistically higher chance of a costly claim than one with layered defenses in place. Underwriters have adjusted their models accordingly, and many now require documented evidence of specific controls before they will issue or renew a policy.
This is not simply about avoiding paperwork. Insurers have learned that certain controls dramatically reduce both the likelihood and the severity of claims. A business that can demonstrate strong prevention and recovery capabilities is simply a better financial risk, and insurers price accordingly.
The Core Security Controls Insurers Now Require
While requirements vary by carrier and policy size, most cyber insurance applications now ask detailed questions about the following areas.
Multi-Factor Authentication
Multi-factor authentication (MFA) has become close to a universal requirement, particularly for email accounts, remote access, and administrative logins. Insurers view MFA as one of the single most effective controls against account takeover, and many carriers will deny coverage outright if it is not in place across critical systems.
Endpoint Detection and Response
Traditional antivirus software is no longer considered sufficient. Insurers increasingly expect endpoint detection and response (EDR) tools that can identify and contain suspicious behavior in real time, rather than relying solely on signature-based detection of known threats.
Backup and Recovery Capabilities
Insurers scrutinize backup practices closely because ransomware claims are so directly tied to how quickly and completely a business can recover without paying a ransom. Applications frequently ask about cloud backup solutions, backup frequency, offsite storage, and whether backups are isolated from the primary network.
Continuous Monitoring
A business that can detect an intrusion within hours, rather than weeks, dramatically limits the scope and cost of an incident. Insurers now regularly ask whether a business maintains round the clock monitoring of its network and endpoints.
Email Security and Filtering
Since phishing remains the leading cause of breaches, insurers ask pointed questions about email filtering, domain authentication protocols, and whether inbound email is scanned for malicious attachments and links.
Patch Management
Unpatched software is one of the most common entry points for attackers. Insurers want evidence of a documented patch management process, including timelines for applying critical security updates.
Employee Security Training
Human error remains a leading cause of breaches, and insurers increasingly ask whether a business conducts regular phishing simulations and security awareness training for staff.
Access Controls and Privilege Management
Applications often ask whether the business follows the principle of least privilege, limiting administrative access to only those who truly need it, and whether access is reviewed and revoked promptly when employees leave.
Incident Response Planning
Insurers want to know that a business has a written incident response plan, with clear roles, escalation procedures, and communication steps, rather than a plan to figure things out during the actual event.
Vendor and Third-Party Risk Management
Supply chain attacks have made insurers more curious about how a business vets and monitors the security practices of its vendors, contractors, and software providers.
How Underwriting Questions Have Changed
Older cyber insurance applications asked broad, self-reported questions with little verification. Modern applications look very different. Many carriers now require:
- Detailed technical questionnaires covering specific tools and configurations
- Supporting documentation, such as security policies or vulnerability scan results
- Attestations signed by an IT leader or outside technology provider
- In some cases, external scans of the company’s public-facing systems to independently verify claims
- Follow-up calls or audits for larger policies or higher-risk industries
This added scrutiny catches businesses off guard, especially those that answered application questions optimistically in prior years without having the controls fully implemented. A mismatch between what was claimed on an application and what is actually in place can lead to a denied claim later, even if the business believed it was covered.
What Happens When a Business Does Not Meet Requirements
Falling short of an insurer’s expectations does not always mean an outright denial. It can also show up as:
- Significantly higher premiums to offset perceived risk
- Reduced coverage limits or higher deductibles for ransomware-specific claims
- Exclusions for certain types of incidents until specific controls are implemented
- A requirement to implement missing controls within a set period as a condition of coverage
- Non-renewal at the next policy period if gaps are not addressed
For many businesses, the financial difference between a well-prepared application and an underprepared one is substantial. Strong security controls do not just reduce risk of an incident, they directly reduce the cost of transferring that risk through insurance.
Industry-Specific Underwriting Pressure
Certain industries face even closer scrutiny from cyber insurance carriers due to the sensitivity of the data they handle or their history of claims.
Healthcare
Healthcare organizations handle protected health information subject to strict regulatory requirements, making them a frequent ransomware target. Healthcare practice support providers often work directly with insurers or their clients to document HIPAA-aligned controls during the underwriting process.
Financial Services
Financial firms manage highly sensitive account and transaction data, and regulators impose their own security expectations on top of insurer requirements. Financial services support teams frequently coordinate documentation for both compliance audits and insurance applications simultaneously.
Legal
Law firms hold privileged client information that makes them attractive targets for attackers seeking leverage or valuable data. Legal practice IT providers help firms document access controls and confidentiality safeguards that insurers specifically ask about.
Manufacturing
Manufacturers increasingly rely on connected operational technology, which introduces additional risk categories that insurers are still refining their questions around. Manufacturing sector solutions focus on securing both business systems and production environments to satisfy these evolving expectations, alongside dedicated support for plant floor technology.
Hospitality
Hotels and hospitality businesses process significant volumes of payment card data, making them a frequent target for both attackers and closer insurer scrutiny. Hospitality technology support helps these businesses maintain the payment security standards insurers expect to see documented.
Preparing for a Cyber Insurance Application or Renewal
Businesses that treat cyber insurance preparation as an ongoing process, rather than a last-minute scramble before a renewal deadline, consistently see better outcomes. A practical preparation approach includes the following steps.
Step 1: Conduct a Security Gap Assessment Start with a technology self assessment to identify where current controls fall short of what insurers typically require.
Step 2: Prioritize High-Impact Controls First Focus first on MFA, endpoint detection, backup isolation, and email filtering, since these are the controls insurers weigh most heavily.
Step 3: Document Everything Maintain written policies, configuration records, and training logs so they are ready to support an application or a post-incident claim.
Step 4: Test Incident Response Procedures Run at least one tabletop exercise so the plan reflects how the business would actually respond, not just how it looks on paper.
Step 5: Review Vendor Contracts Confirm that key vendors and software providers meet reasonable security expectations, since third-party incidents increasingly trigger claims.
Step 6: Work With a Knowledgeable Technology Partner A provider offering reliable IT support can translate insurer requirements into a practical technical roadmap rather than leaving business owners to interpret dense questionnaires alone.
The Role of Continuous Monitoring in Claims Outcomes
Beyond approval, monitoring plays a major role in how claims are actually handled after an incident occurs. Insurers increasingly examine how quickly a breach was detected and contained when evaluating a claim. A business with continuous network monitoring in place can typically demonstrate a faster detection timeline, which can influence both the claim outcome and future premium calculations.
This is one of the clearest examples of how security investment and insurance costs are directly connected. It is not just about qualifying for a policy. It is about ensuring that if an incident does happen, the business has the evidence and the response speed needed to support a smooth claims process.
AI and the Future of Cyber Insurance Underwriting
Artificial intelligence is starting to influence both sides of the cyber insurance relationship. On the underwriting side, insurers are experimenting with automated scanning tools that assess a company’s external attack surface before issuing a quote. On the business side, AI powered services can help identify vulnerabilities and unusual activity before they turn into the kind of incident that triggers a claim in the first place.
As businesses adopt more AI tools internally, insurers are also beginning to ask new questions about how that technology is deployed and secured. A secure AI adoption approach, paired with a documented AI readiness evaluation, positions a business to answer these emerging questions with confidence rather than uncertainty. Secure platforms that support secure remote access are also drawing more attention from underwriters as remote and hybrid work remain permanent fixtures for many businesses.
Common Mistakes That Hurt Insurance Applications
Businesses frequently make avoidable mistakes that weaken their applications or expose them during a claim.
- Overstating current controls. Answering “yes” to a control that is only partially implemented can void coverage if discovered during a claim investigation.
- Failing to update coverage as the business grows. A policy sized for a smaller operation may leave significant gaps once the business expands.
- Ignoring endpoint devices outside the office. Remote and hybrid employees introduce risk that many applications specifically ask about but businesses forget to secure.
- Not reviewing exclusions carefully. Some policies exclude specific attack types or require particular controls to be in place for certain coverage to apply.
- Treating the policy as a substitute for security investment. Insurance transfers financial risk, but it does not prevent an incident or the operational disruption that comes with one.
- Neglecting to isolate backup systems. Insurers pay close attention to whether backups are separated from production networks, and applications that leave offsite data storage practices vague often face additional underwriting questions or lower coverage limits.
Businesses that address these issues before submitting an application typically move through underwriting faster and avoid the frustrating back-and-forth that comes with incomplete or inconsistent answers. It is also worth remembering that insurers periodically update their questionnaires as new attack methods emerge, so a policy that was approved smoothly two years ago may face a very different set of questions at the next renewal.
Building Long-Term Alignment Between Security and Insurance
The businesses that fare best in this new underwriting environment treat security and insurance as connected, not separate, decisions. A few practices support that alignment over time:
- Reviewing security controls annually, ahead of each policy renewal rather than reactively
- Keeping documentation current as tools, vendors, and staff change
- Involving a technology partner directly in the application or renewal process when questions get technical
- Using insurer questionnaires as a free security checklist rather than an obstacle to check off quickly
- Treating strategic IT guidance as an ongoing relationship rather than a one-time consultation before a deadline
- Confirming that proactive threat protection measures stay current as new vulnerabilities and attack techniques emerge throughout the year
This approach turns what many business owners see as a frustrating annual chore into a useful forcing function that keeps security practices current. It also builds a more collaborative relationship with an insurance broker or carrier, since businesses that can speak confidently about their controls tend to move through renewals with fewer surprises and fewer requests for additional documentation.
Additional Layers Worth Strengthening
Beyond the core controls insurers ask about directly, a few supporting investments make the overall security and insurance picture stronger.
- Modern productivity software tools with built-in security features reduce reliance on outdated, unsupported applications that are harder to secure
- Reliable unified communication tools reduce shadow IT, where employees turn to unapproved apps that fall outside the company’s security controls
- Structured technology procurement solutions ensure new hardware and software are vetted for security before they are deployed, rather than creating gaps after the fact
- Ongoing advanced threat prevention keeps the overall risk profile low between insurance renewal cycles, not just during the application process
Turning Renewal Season Into a Security Improvement Cycle
Rather than viewing the cyber insurance renewal date as a deadline to survive, many businesses now use it as a natural checkpoint to reassess their entire technology environment. This shift in mindset tends to produce better outcomes on both the insurance and security sides of the equation.
A practical annual cycle might look like this:
- Three months before renewal, complete an internal review of controls against the previous year’s application answers
- Address any gaps with business AI solutions or additional monitoring tools where automation can close detection gaps efficiently
- Two months before renewal, request an updated free IT assessment to confirm improvements are documented and measurable
- One month before renewal, finalize documentation, policy updates, and training records so the application reflects the business’s current state accurately
- After renewal, revisit manufacturing IT management practices or other industry-specific controls that may need attention before the next cycle begins
This structured approach reduces last-minute scrambling, gives leadership time to budget for any needed upgrades, and creates a clear paper trail that supports both smoother underwriting and stronger protection against real incidents.
Communication During and After an Incident
Even businesses with strong controls in place can experience a security incident. How that incident is handled, both technically and in terms of internal and external communication, significantly affects the insurance claims process. Business communication platforms that remain accessible even during a network disruption help ensure that leadership, staff, and outside partners stay coordinated throughout the response.
Insurers generally expect a business to notify them promptly once an incident is identified, often within a specific window defined in the policy. Delayed notification, incomplete documentation of the timeline, or inconsistent internal communication can all complicate a claim, regardless of how well the underlying technical response was handled. A dependable technical support partner who understands both the technical and administrative sides of incident response can help ensure nothing falls through the cracks during a stressful, time-sensitive situation.
Working With a Local Partner Who Understands Both Sides
Navigating cyber insurance requirements alongside day-to-day business operations is difficult to do alone, particularly for businesses without a dedicated internal security team. CMIT Solutions of Greenville helps local businesses across manufacturing, healthcare, financial services, legal, and hospitality industries translate insurer requirements into practical, achievable technology improvements, rather than leaving them to interpret dense underwriting questionnaires on their own.
The goal is not simply passing an application. It is building a security foundation strong enough that insurance becomes a backup layer of protection rather than the primary plan, while also keeping premiums manageable and claims processes smooth if an incident does occur. Businesses that pair strong technical controls with sound hardware and software solutions tend to be better positioned as insurers continue expanding the questions they ask about device management and technology lifecycle practices.
If your business is approaching a cyber insurance renewal, or has been surprised by new underwriting requirements, it is worth reviewing your current security posture before the application lands on your desk. Schedule a consultation to walk through where your business stands today, or connect with specialists who can help align your technology environment with what insurers now expect.
“`html id=”cyber-insurance-underwriting-faq”
Frequently Asked Questions