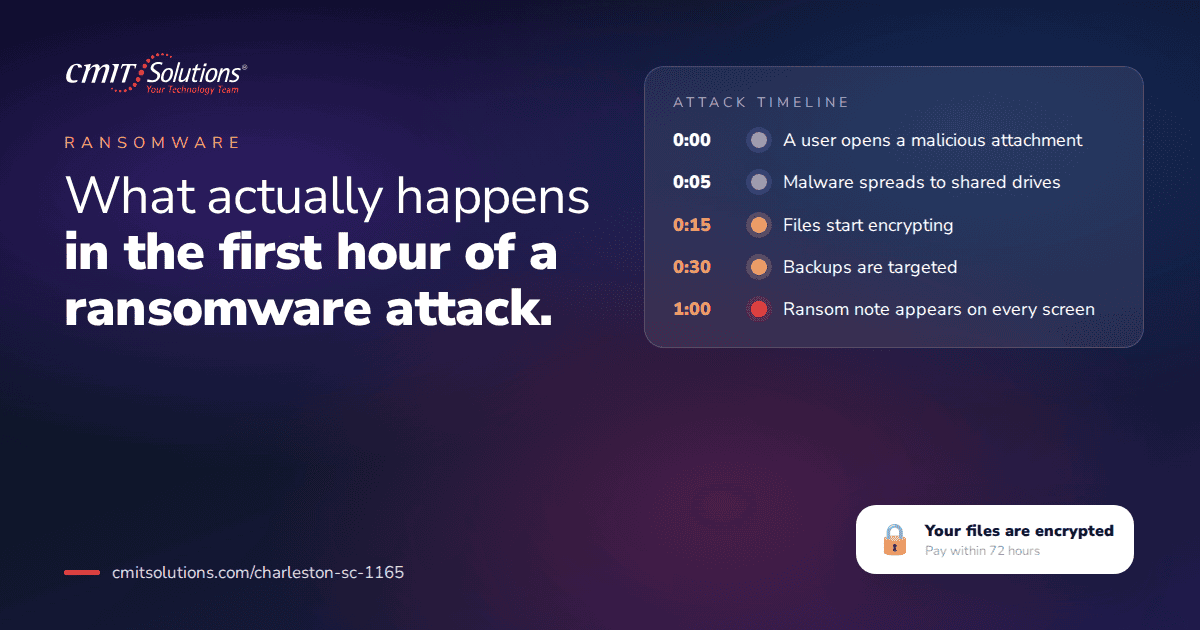
Most people picture a ransomware attack as a single dramatic moment: a red screen, a ransom note, files suddenly locked. In reality, the first hour looks nothing like that. It’s quieter, more confusing, and far more critical than most business owners realize. What happens in those sixty minutes often determines whether a business recovers in days or spends months rebuilding.
Understanding this timeline isn’t just useful after the fact. It’s the difference between a team that knows exactly what to do and one that freezes while the damage keeps spreading.
Minute Zero: The Attack Was Already Working Before Anyone Noticed
By the time ransomware actually encrypts files, the attacker has usually already been inside the network for days, sometimes weeks. The visible “attack” is really the final stage of a much longer process. Understanding this timeline matters because it reframes the entire problem: the goal isn’t just reacting fast in the first hour, it’s catching the earlier stages before encryption ever begins, a concept explored in proactive IT monitoring.
Before the visible attack, the following usually already happened:
- Initial access gained through a phishing email, stolen credentials, or an unpatched vulnerability
- Quiet exploration of the network to identify valuable files, backups, and administrative accounts
- Disabling or weakening of security tools designed to detect the coming attack
- Data quietly copied off the network, setting up a second layer of extortion
- Backup systems specifically targeted and often compromised first
By the time encryption starts, the attacker already knows exactly what they’re locking and how much leverage they have.
Minutes 1 to 5: The First Signs Something Is Wrong
The earliest signs of an active ransomware attack are usually subtle enough to be dismissed at first glance. An employee notices files won’t open. A shared drive suddenly looks different. Print jobs fail for no clear reason.
Typical early indicators include:
- File names suddenly appearing with unfamiliar extensions
- Applications crashing or refusing to open previously accessible files
- A noticeable spike in CPU or disk activity across multiple machines at once
- Antivirus or security software showing alerts that get dismissed as false positives
- Slower network performance as encryption processes consume system resources
This is exactly why reactive IT problems create such dangerous blind spots. Without active monitoring, these early warning signs are easy to miss or explain away until the damage has already spread much further.
Minutes 5 to 15: The Moment of Recognition
At some point in the first fifteen minutes, someone finally realizes this isn’t a routine glitch. Maybe a ransom note appears on screen. Maybe an entire shared drive becomes inaccessible all at once. Maybe multiple employees report the same problem within minutes of each other.
This moment matters enormously, because what happens next depends entirely on whether the business has a plan or is improvising under pressure.
- Businesses with a documented response plan immediately know who to call and what steps to take first
- Businesses without one often waste critical minutes trying to figure out who’s responsible for what
- Panic-driven decisions at this stage, like shutting down systems incorrectly, can sometimes destroy forensic evidence needed for recovery
The gap between these two outcomes is covered in more detail in IT outage impact, where confusion in the earliest moments often causes more lasting damage than the technical failure itself.
Minutes 15 to 25: Containment Becomes the Priority
Once ransomware is confirmed, the immediate goal shifts to stopping it from spreading any further. Every additional minute of delay typically means more encrypted files and more compromised systems.
Effective containment steps include:
- Isolating affected devices from the network immediately, without powering them off completely
- Disconnecting shared drives and network storage to prevent encryption from spreading further
- Disabling remote access temporarily to cut off any active attacker connection
- Preserving evidence rather than wiping devices, since forensic details matter for recovery and reporting
- Notifying key stakeholders internally so decisions can be made quickly and consistently
Proper network segmentation makes this stage significantly faster and more effective, since a well-structured network management services setup limits how far an attack can spread in the first place, sometimes containing it to a single device instead of an entire office.
Minutes 25 to 35: Assessing the Actual Damage
With the spread contained, the next priority becomes understanding the full scope of what’s been affected. This step is often more complicated than it sounds, since ransomware frequently spreads across multiple systems before detection.
Key questions during this phase include:
- Which specific systems, servers, and devices have been encrypted
- Whether backup systems were also compromised or remain intact
- Whether any data appears to have been copied or exfiltrated before encryption
- Whether the attacker still has any active access to the network
- What business operations are directly affected and which can continue unaffected
This is where the difference between tested and untested backups becomes painfully clear. A backup strategy that’s never been verified often reveals its weaknesses at exactly the wrong moment, a risk detailed in cloud backup options.
Minutes 35 to 45: The Ransom Note Decision
Most ransomware attacks include a note demanding payment, often with a countdown timer designed to pressure quick decisions. This is one of the most consequential moments in the entire incident, and it’s not one that should be handled alone or under panic.
Important considerations at this stage:
- Law enforcement generally advises against paying ransoms, since payment doesn’t guarantee data recovery
- Paying can mark a business as a repeat target for future attacks
- Legal and regulatory obligations may require specific reporting steps regardless of payment decisions
- Cyber insurance policies, if in place, often dictate specific procedures that must be followed
This is exactly the kind of decision that should be mapped out well before an attack happens, not figured out in real time while a countdown clock is running. A resilient recovery strategy built around ransomware backup protection often removes the pressure to pay entirely, since clean, tested backups make restoration possible without negotiating with attackers.
Minutes 45 to 60: Beginning the Recovery Process
By the end of the first hour, the focus shifts from containment and assessment to the early stages of recovery. This doesn’t mean systems are back online yet, but it marks the point where a clear path forward starts to take shape.
Early recovery activities typically include:
- Confirming which backups are clean, tested, and safe to restore from
- Beginning the process of rebuilding or restoring the most critical systems first
- Communicating with employees about what to expect over the coming hours and days
- Preparing initial client or vendor communications if operations will be visibly affected
- Documenting the incident thoroughly for compliance, insurance, and legal purposes
Businesses with a prioritized recovery order already established, knowing exactly which systems matter most, tend to restore operations significantly faster than those figuring it out on the fly.
Why the First Hour Determines the Next Month
The decisions made in that first sixty minutes ripple far beyond the immediate crisis. Businesses that contain the attack quickly, preserve clean backups, and follow a documented plan often return to normal operations within days. Businesses that delay, panic, or lack a plan can face weeks or months of disruption, a gap explored in detail in cost of downtime.
Long-term consequences of a mishandled first hour can include:
- Extended operational downtime affecting revenue and client relationships
- Permanent data loss if backups were compromised or never properly tested
- Regulatory fines if breach notification requirements aren’t met promptly
- Increased cyber insurance premiums or denied claims due to inadequate security practices
- Lasting reputational damage if clients weren’t informed clearly and quickly
Why Ransomware Attacks Are Becoming More Frequent
Ransomware isn’t a rare, isolated threat anymore. It’s become a structured criminal industry, with attackers using increasingly automated and AI-assisted tools to identify and exploit vulnerable businesses faster than ever, a trend covered in ransomware backup protection.
Several factors are driving this increase:
- Ransomware-as-a-service platforms allow less technically skilled attackers to launch sophisticated attacks
- Automated scanning tools constantly search for unpatched systems and weak entry points
- Double extortion tactics, combining encryption with data theft, increase pressure on victims to pay
- Smaller businesses are increasingly targeted, since attackers assume weaker defenses than large enterprises
How MFA Fatigue and Phishing Often Set the Stage
Many ransomware attacks don’t start with a sophisticated technical exploit. They start with something much simpler: a stolen password combined with persistence. Attackers flood employees with authentication requests until one gets approved out of sheer annoyance, granting the access needed to begin the entire attack chain.
Common entry points that lead to ransomware include:
- Convincing phishing emails that trick employees into entering credentials on fake login pages
- Repeated authentication prompts that wear down an employee until one is approved by mistake
- Reused passwords exposed in unrelated data breaches and tested against business accounts
- Unpatched software vulnerabilities that provide a direct path into the network
Recognizing these earlier warning signs, rather than only the final encryption stage, is where prevention actually happens. Regular security awareness training helps employees catch these attempts before they ever reach the point of encryption.
Why a Layered Security Stack Matters More Than Any Single Tool
No single piece of software stops every ransomware attack. What actually works is a layered approach where multiple tools catch different stages of the attack chain, ideally stopping it long before the first hour ever begins.
A layered defense typically includes:
- Email filtering that catches phishing attempts before they reach an inbox
- Endpoint detection and response that flags suspicious behavior on individual devices
- Network monitoring that identifies unusual traffic patterns indicating lateral movement
- Multi-factor authentication configured to resist common bypass techniques
- Regular vulnerability scanning that closes gaps before attackers find them
Understanding where basic antivirus software falls short compared to more advanced detection tools is covered in cybersecurity stack basics. A comprehensive cybersecurity protection services approach ties these layers together so that a single failure doesn’t lead to a company-wide incident.
Choosing the Right Detection and Response Model
Businesses often assume basic antivirus is enough, but modern ransomware requires active detection and response capable of identifying an attack while it’s still unfolding, not after files are already encrypted. Choosing between managed detection and response, managed security service providers, and broader security platforms depends heavily on the specific risk profile of the business, a comparison covered in right security model.
Building an Incident Response Plan Before You Need One
The single biggest factor separating a fast, controlled recovery from a chaotic, drawn-out crisis is whether a documented incident response plan already exists. Building this plan during an actual attack almost always leads to worse outcomes.
A strong incident response plan should clearly define:
- Who is responsible for making key decisions during an incident
- The exact order in which systems should be isolated and assessed
- Which backups are considered clean and how quickly they can be restored
- How and when to communicate with employees, clients, and regulators
- What role, if any, cyber insurance and legal counsel play in the process
Businesses without a documented plan often lose valuable time in exactly the moments when speed matters most.
Compliance Obligations During a Ransomware Incident
For businesses in regulated industries, the first hour isn’t just about technical recovery. It’s also the start of a compliance clock that often carries legal deadlines for notification and reporting, a distinction covered in audit ready compliance.
Businesses should understand in advance:
- What breach notification timelines apply to their specific industry and location
- Which regulatory bodies or clients must be informed, and within what timeframe
- What documentation needs to be preserved throughout the incident for later review
- How third-party vendors and partners should be notified if their data was involved
A dedicated compliance support services partner helps ensure these obligations are met correctly, reducing the chance of additional penalties layered on top of an already difficult situation.
Cloud Systems and Ransomware: A Growing Target
As more businesses shift critical operations to cloud platforms, ransomware has evolved to target these environments directly, not just traditional on-premises servers. Gaps between disconnected cloud applications create exactly the kind of blind spots attackers exploit, a vulnerability outlined in hidden cloud risks.
Businesses relying on cloud platforms should confirm:
- Cloud backups are configured separately from primary storage and regularly tested
- Administrator accounts carry stronger authentication requirements than standard users
- File-sharing permissions are reviewed regularly rather than left unchecked
- Former employee access is removed promptly across every connected platform
A centralized cloud services solutions strategy makes it far easier to maintain consistent protection across every platform the business depends on.
Remote Work and the Expanded Attack Surface
Distributed teams have significantly expanded the number of potential entry points for ransomware. An employee logging in from a home network or personal device presents a different risk profile than one working inside a monitored office environment, a shift discussed in remote team support.
Businesses supporting remote or hybrid teams should ensure:
- Remote access tools require strong, monitored authentication by default
- Personal devices used for work meet minimum security standards before connecting
- Employees have a clear, fast way to report suspicious activity regardless of location
- Communication stays centralized so response coordination doesn’t fall apart during a crisis
Reliable unified communications tools help keep distributed teams aligned, especially critical during the fast-moving early hours of an active incident.
The Role of Regular Monitoring in Stopping Attacks Before Hour One
The businesses that never experience this timeline at all are usually the ones with continuous, active monitoring catching suspicious activity days or weeks before encryption would ever begin. This is the real goal, not just responding well to an attack in progress, but identifying the early stages before the countdown clock ever starts, a concept explored further in threat exposure management.
Effective ongoing monitoring includes:
- Real-time alerts for unusual login patterns or privilege escalation attempts
- Behavioral analysis flagging activity that deviates from normal network patterns
- Regular vulnerability scans identifying unpatched systems before attackers find them
- Centralized visibility across every device, account, and connected platform
Why Preparation Beats Reaction Every Time
Every step covered in this first-hour timeline becomes faster, calmer, and more effective when it’s been planned in advance rather than improvised under pressure. Businesses that invest in strategic IT guidance before an incident happens consistently recover faster and with far less disruption than those scrambling to build a plan while the clock is already running.
Preparation should include:
- A documented, tested incident response plan everyone understands
- Regularly tested backups stored separately from the primary network
- Layered security tools covering email, endpoints, and network traffic
- Ongoing employee training to catch attacks before they ever reach the encryption stage
- A trusted IT partner who can respond immediately, not just during business hours
Why Charleston Businesses Need a Partner Who Moves Fast
When ransomware hits, every minute matters, and a slow or unresponsive IT partner can turn a contained incident into a company-wide disaster. Local businesses benefit from working with a team that understands the regional business landscape and can respond immediately, not after navigating a distant call center.
CMIT Solutions of Charleston helps businesses build the layered defenses, tested backups, and documented response plans that make the difference between a fast, controlled recovery and a prolonged crisis. The goal isn’t just surviving the first hour. It’s making sure that hour never has to happen in the first place.
Getting ahead of this starts with an honest assessment of where your current systems and plans stand today, before an attacker forces that conversation on their terms instead of yours.
The Bottom Line
The first hour of a ransomware attack is chaotic, fast-moving, and unforgiving of hesitation. Every decision, from containment to communication to the ransom note itself, carries consequences that extend far beyond that initial sixty minutes. Businesses that prepare in advance, with tested backups, a documented plan, and layered security, move through this timeline with control instead of panic.
The businesses that never have to live through this hour at all are the ones investing in prevention long before an attacker ever gets the chance to test their defenses.
If your business doesn’t have a clear plan for the first hour of a ransomware attack, now is the time to build one, not during the incident itself. Schedule a consultation to get a clear assessment of your current defenses and response readiness.
Frequently Asked Questions