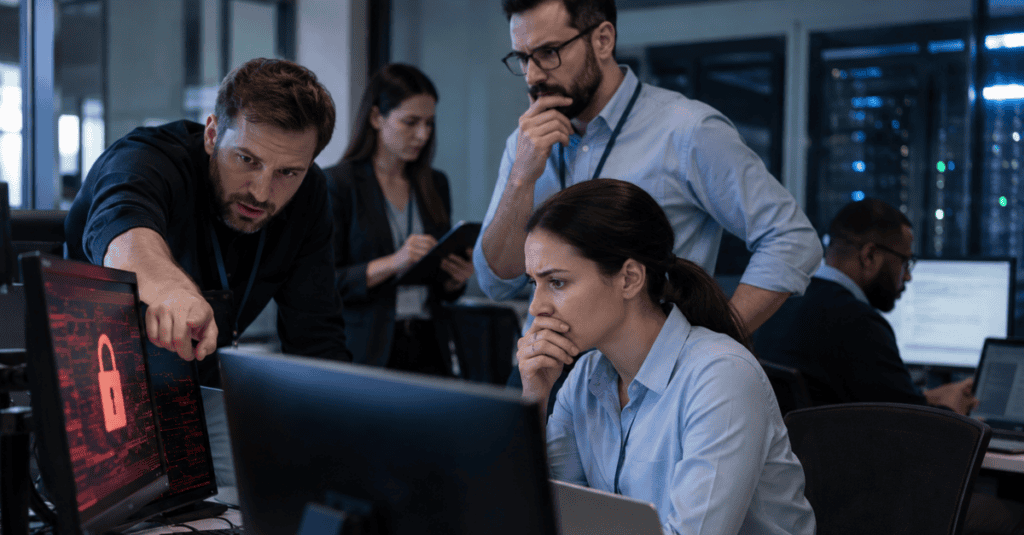
A ransomware attack rarely announces itself politely. One moment employees are working normally, and the next, files are locked, screens display a ransom note, and panic starts spreading through the office. What happens in the first few hours after that discovery often determines whether a business recovers in days or spends weeks rebuilding from scratch.
CMIT Solutions of Greenville has walked local businesses through exactly this kind of crisis, and the pattern is consistent: organizations with a clear, rehearsed response plan recover faster and lose far less than those scrambling to figure things out in real time. This article walks through what should happen hour by hour after a ransomware attack is discovered, and why preparation matters just as much as the response itself.
Why the First Hours Matter So Much
Ransomware doesn’t just encrypt files and sit still. Many strains continue spreading across a network for hours or even days if left unchecked, moving from one device to another, searching for backups to disable, and exfiltrating data before the encryption process even finishes. Every minute of delay in containment can mean more systems affected and more data at risk.
At the same time, panic leads to mistakes. Employees may try to reboot machines, disconnect drives, or pay the ransom without consulting anyone, actions that can destroy evidence or make recovery harder. A calm, structured response in those first hours protects both the technical recovery process and the business’s ability to make informed decisions afterward. This urgency is part of why so many companies are re-examining their sophisticated ransomware attack trends and asking whether their current defenses are actually built for what’s happening now.
Minute Zero: Recognizing the Signs
Before any response can begin, the attack has to be identified. Common early warning signs include:
- Files suddenly renamed with unusual extensions
- A ransom note appearing on desktops or in shared folders
- Unusual spikes in CPU or disk activity across multiple machines
- Employees reporting they can no longer open files
- Security tools flagging unauthorized encryption processes
- Sudden inability to access shared drives or applications
The faster these signs are recognized and reported, the more options a business has for limiting the damage. This is one reason continuous monitoring tools built around modern threat detection tools matter so much. Automated detection can catch encryption behavior in its earliest stages, sometimes before a human would ever notice.
Hour One: Contain and Isolate
Once ransomware is confirmed or even strongly suspected, the priority shifts immediately to containment. This is not the time to investigate root causes or assess the full scope. The goal is simple: stop the spread.
Key actions during this window include:
- Disconnecting affected devices from the network immediately, using physical unplugging rather than shutting them down
- Disabling Wi-Fi and shared network drives to prevent lateral movement
- Isolating backup systems to protect them from being targeted next
- Alerting the internal IT team or managed service provider without delay
- Documenting the time the attack was discovered and every action taken from that point forward
Shutting down a device completely, rather than disconnecting it, can sometimes destroy volatile memory evidence that’s useful later for understanding how the attack happened. Disconnecting from the network while leaving the device powered on is usually the safer first move. This is exactly the kind of split-second decision that becomes far easier when a business already has proactive network visibility in place, since IT teams can see exactly which systems are affected in real time instead of guessing.
Hours Two to Four: Activate the Incident Response Plan
If a formal incident response plan exists, this is when it gets put into action. If one doesn’t exist, this is when the gaps become painfully obvious. A functional response plan should clearly define:
- Who has authority to make decisions during an active incident
- Which internal and external contacts need to be notified immediately
- How communication will happen if email and messaging systems are compromised
- What systems are considered critical and should be prioritized for restoration
- Where backup and recovery resources are stored and how to access them
During this stage, businesses should also loop in their cyber defense services provider if they haven’t already, since specialized expertise at this point can significantly shorten the recovery timeline. Companies that have already reviewed next-gen ransomware preparation strategies tend to move through this phase with far less confusion than those encountering these decisions for the first time mid-crisis.
Hours Four to Eight: Assess the Scope
With the immediate spread contained, attention turns to understanding exactly what happened. This phase typically involves:
- Identifying which systems, servers, and devices were affected
- Determining whether data was exfiltrated in addition to encrypted
- Reviewing logs to trace how the attacker initially gained access
- Checking whether backups were tampered with or remain intact
- Classifying the sensitivity of any data that may have been exposed
This is also when many businesses discover unseen security weaknesses that had existed for months or even years without anyone noticing. Understanding the entry point matters not just for recovery, but for making sure the same vulnerability doesn’t lead to a repeat attack once systems are restored.
Should a Business Ever Pay the Ransom?
This question comes up in nearly every ransomware incident, and there’s no universally correct answer. A few important considerations:
- Paying the ransom does not guarantee working decryption keys will be provided
- Some attackers demand additional payments after the first one is made
- Paying may violate regulations in certain industries or jurisdictions
- Law enforcement generally advises against payment when possible
- Cyber insurance policies often have specific requirements around ransom payment decisions
This decision should never be made unilaterally by a single employee in a moment of panic. It requires input from leadership, legal counsel, and often law enforcement, which is exactly why having a documented decision-making process matters as much as the technical recovery itself.
Hours Eight to Twenty-Four: Begin Restoration
Once the scope is understood and containment is holding, restoration can begin. This is where a business’s backup strategy is truly tested. Businesses with tested, isolated backups can often restore critical systems within hours. Those without reliable backups face a much longer, more uncertain path.
Effective restoration typically follows this order:
- Restore the most business-critical systems first, based on a pre-defined priority list
- Rebuild affected systems from clean images rather than restoring on top of infected ones
- Verify restored systems are free of malware before reconnecting them to the network
- Reset credentials across the organization, especially for any accounts that may have been compromised
- Gradually reintroduce systems to the network in a controlled, monitored sequence
Businesses that have invested in faster cyberattack recovery strategies and reliable backup systems consistently report shorter downtime and lower recovery costs. Increasingly, organizations are turning to intelligent recovery systems that automate much of the verification and restoration process, reducing the chance of human error during an already stressful event.
Communication: Internal and External
While technical teams work on containment and restoration, communication has to happen in parallel. Silence during a crisis tends to create more anxiety and speculation than transparency does.
Internal communication should cover:
- What employees can and cannot do while systems are down
- Alternative ways to communicate if email is unavailable
- Reassurance that leadership is actively managing the situation
- Clear instructions to avoid discussing the incident on personal social media
External communication may need to include:
- Clients or partners whose data or services could be affected
- Regulatory bodies, depending on the industry and nature of the breach
- Law enforcement, particularly for larger incidents involving data theft
- Cyber insurance providers, who often require prompt notification
Healthcare organizations in particular need to move carefully here, since healthcare data protection requirements can trigger specific notification obligations depending on what data was involved. Similarly, businesses in the nonprofit sector should review their nonprofit breach readiness plans, since donor and grant data often carries its own reporting expectations.
Preserving Evidence for Investigation
Throughout the entire response, preserving evidence matters just as much as restoring operations. This includes:
- Keeping logs and system images from affected devices before wiping or rebuilding them
- Documenting a detailed timeline of when each action was taken and by whom
- Saving copies of the ransom note and any communication from the attacker
- Recording which accounts and systems were accessed during the incident
- Working with forensic specialists if the incident is significant enough to warrant deeper investigation
This evidence becomes critical not only for law enforcement involvement, but also for insurance claims and any regulatory reporting that follows. Rushing to wipe and rebuild systems without preserving this information can create major problems weeks later.
The Role of Compliance in Recovery
For regulated industries, ransomware recovery isn’t just a technical process, it’s also a compliance obligation. Businesses need to understand their specific reporting timelines and requirements well before an incident occurs, not while it’s happening.
Organizations working with government contracts should be especially mindful, since frameworks discussed in defense contractor compliance requirements don’t pause just because a business is in recovery mode. Financial institutions and accounting firms face similar pressure, particularly during high-volume periods, which ties directly into ongoing conversations about financial sector threat monitoring as a year-round priority rather than a seasonal concern.
Working with a provider that offers structured compliance program support before an incident occurs means the reporting process during recovery is far less chaotic, since the framework for who needs to be notified and when is already established.
Rebuilding Trust After an Incident
Technical recovery is only part of the picture. Clients, employees, and partners will remember how a business handled the crisis, not just that a crisis happened. Rebuilding trust involves:
- Being transparent about what happened without overexplaining technical details
- Sharing what steps are being taken to prevent a repeat incident
- Following through on any commitments made during the communication process
- Demonstrating visible improvement in security posture over the following months
Businesses that treat this as an opportunity to strengthen relationships, rather than simply moving past an embarrassing event, often come out of the incident with stronger client confidence than before.
Preventing the Next Attack
Once systems are stable, attention should shift toward preventing a repeat incident. This typically includes:
- Conducting a full post-incident review to identify exactly how the attack began
- Patching the specific vulnerability that was exploited
- Strengthening layered security architecture across the network rather than relying on a single point of defense
- Reviewing and testing backup systems more frequently going forward
- Expanding employee training based on how the attack initially gained access
Many organizations also use this moment to evaluate automated IT operations as a way to catch anomalies faster next time, reducing reliance on manual monitoring that can miss early warning signs during off-hours.
Supporting Infrastructure That Makes Recovery Possible
None of this response happens effectively without solid infrastructure already in place before the attack occurs. Businesses should evaluate whether they have:
- 24/7 IT management that can respond immediately when an incident is detected, regardless of the hour
- Network monitoring services that provide visibility into unusual activity before it escalates
- Secure cloud infrastructure with proper access controls and backup redundancy
- Team communication platforms that remain accessible even if primary email systems go down
- Responsive IT help available around the clock, not just during standard business hours
- Hardware procurement services ready to quickly replace compromised devices when needed
- Business productivity tools configured with appropriate security settings from the start
- IT roadmap planning that accounts for disaster recovery as an ongoing priority, not an afterthought
- Custom IT plans structured around a business’s actual risk profile rather than a one-size-fits-all package
Businesses in healthcare should also revisit common healthcare security missteps that tend to resurface after an incident, while those exploring around-the-clock monitoring options should look into 24/7 security monitoring as a longer-term solution. Companies moving significant operations to the cloud should also revisit overlooked cloud vulnerabilities that often go unnoticed until an incident forces the issue, and those supporting hybrid teams should confirm their secure hybrid work tools haven’t introduced new gaps along the way. Ongoing ongoing compliance checks round out a recovery strategy that holds up well past the first few weeks after an incident.
A Simple First-Hours Checklist
For quick reference during an active incident, here’s a condensed version of the priorities covered above:
- Disconnect affected devices from the network without shutting them down
- Alert IT and leadership immediately
- Activate the documented incident response plan
- Isolate and protect backup systems
- Assess the scope of affected systems and potential data exposure
- Involve legal counsel before making any decisions about ransom payment
- Begin restoration from clean, verified backups
- Communicate clearly with employees, clients, and regulators as needed
- Preserve evidence for investigation and insurance purposes
- Schedule a post-incident review once systems are stable
Final Thoughts
Ransomware recovery isn’t just about technology, it’s about having a clear, tested plan and the right partners in place before an attack ever happens. CMIT Solutions of Greenville helps local businesses build that kind of preparedness, so the first hours after an incident are guided by a plan rather than panic.
If your business doesn’t have a tested incident response and recovery plan in place, now is the time to build one. Schedule a consultation to review your current setup and close the gaps before an attacker finds them first.
Frequently Asked Questions