The difference comes down to scope. A managed service provider keeps your technology running, a managed security service provider defends it from cyber threats, and a managed intelligence provider does both while governing the AI tools your team has already started to use.
- Managed service provider (MSP): Handles day-to-day IT operations, from networks and devices to help desk support and backups. The goal is uptime and smooth operations.
- Managed security service provider (MSSP): Focuses only on cybersecurity, with round-the-clock monitoring, threat detection, and incident response run from a security operations center. The goal is reducing risk.
- Managed intelligence provider (MIP): Does the MSP job, layers on security, and adds governance for AI and automation so a business can adopt these tools safely. The goal is productivity without new exposure.
For more than 30 years, CMIT Solutions has guided small and mid-sized businesses through choices like MSP vs MSSP, and now MSP vs MIP, helping them pick the right level of support as their technology, and their risks, have changed. Below is a plain breakdown of each model and where a growing business usually lands.
To adopt AI productively while keeping your systems protected, explore CMIT Solutions’ managed AI solutions.
MSP vs MSSP vs MIP: what are the differences?
The three models differ mainly by scope and by the goal each one serves, and they build on one another more than they compete. Most providers specialize in a single layer, though the categories increasingly overlap as security and AI become part of everyday business technology.
The table below shows how the three compare on the points that matter most to a buyer.
| Category | Managed service provider (MSP) | Managed security service provider (MSSP) | Managed intelligence provider (MIP) |
| Primary focus | Keeping IT running and efficient | Defending systems against cyber threats | Running and securing IT, plus governing AI use |
| Core services | Network and device management, help desk, cloud, backups, patching | 24/7 monitoring, threat detection, incident response, vulnerability management, compliance reporting | MSP and security services, plus AI policy, approved tool management, and monitoring of AI activity |
| Security scope | Baseline protections such as antivirus, firewalls, and patching | Advanced, layered security run from a security operations center | Layered security extended to cover the data shared with AI tools |
| AI governance | Not a focus; AI tools sit outside typical scope | Limited to the security risks AI tools create | Central role: acceptable use policies, data controls, and oversight of sanctioned and unsanctioned AI |
| Best-fit business scenario | A business that needs reliable IT without an in-house team | A business with IT in place but a serious security or compliance burden | A growing business where staff are adopting AI and need it managed safely |
The sections below break down each model, and CMIT Solutions helps businesses figure out which one fits today and what to add as they grow.
What is a managed service provider (MSP)?
A managed service provider handles the daily technology work that keeps a business running. This includes managing networks, devices, and software, backing up data, and staffing a help desk, usually for a predictable monthly fee. The aim is steady uptime, so staff can focus on work, not IT problems.
Most MSPs work from a network operations center, or NOC, where they watch system health and step in before small issues turn into downtime.
Core services an MSP handles
MSP services cover the core of day-to-day IT. Common ones include:
- Network and infrastructure management: Keeping routers, servers, and connections stable and secure. This covers routine configuration and performance checks.
- Help desk and user support: Resolving everyday issues such as password resets, device setup, and software questions. Support is usually available during business hours or around the clock.
- Cloud and backup management: Moving workloads to the cloud and protecting data with regular, tested backups. This supports recovery when something goes wrong.
- Patching and maintenance: Applying updates that fix bugs and close known weaknesses. This reduces the risk of outages and some attacks.
When an MSP is the right fit
An MSP fits a business that needs dependable IT but lacks the staff or budget to run it alone. If your main concerns are uptime, support, and keeping technology organized, rather than advanced threats, an MSP covers the essentials well. Many smaller firms start here and add more later.
When a business outgrows basic support, CMIT Solutions helps it map out which added capabilities, security or AI oversight, will matter most next.
See what unplanned downtime could be costing your business with the IT downtime calculator.
What is a managed security service provider (MSSP)?
A managed security service provider focuses only on cybersecurity. It delivers round-the-clock monitoring, threat detection, incident response, and compliance support, typically from a security operations center, or SOC, staffed by analysts. Where an MSP keeps systems running, an MSSP works to keep them safe from attacks and data loss.
That focus is the key structural difference from an MSP: the MSSP works from a SOC rather than a NOC, with a team built around detecting and stopping threats instead of general IT upkeep.
Many of the controls an MSSP manages, such as multifactor authentication, logging, and tested backups, line up with the baseline safeguards recommended for small and mid-sized businesses.
Core services an MSSP handles
MSSP services center on protection and response. They commonly include:
- Continuous monitoring and threat detection: Watching systems day and night for signs of attack. Alerts are triaged by security analysts, not just by software.
- Incident response: Containing, investigating, and recovering from attacks when they happen. The goal is to limit damage and restore operations quickly.
- Vulnerability management: Scanning for weak points across devices and applications, then ranking what to fix first. This keeps limited resources focused on real risk.
- Compliance support: Producing the monitoring and reporting needed for rules such as HIPAA, PCI DSS, and similar frameworks. This helps regulated businesses stay audit ready.
MSSP vs MDR: clearing up a common mix-up
Managed detection and response, or MDR, is often confused with an MSSP, but it is narrower. MDR is a specific service, advanced threat hunting and hands-on response, that the stronger MSSPs provide. Put simply, MDR is a capability inside the broader category of managed security, not a separate type of provider.
When an MSSP is the right fit
An MSSP fits a business that already has working IT but faces real security pressure, whether from its industry, its data, or past incidents. If you handle sensitive records, face strict regulations, or cannot find security staff to hire, dedicated monitoring and response close a serious gap.
CMIT Solutions builds this kind of layered protection into its managed services, so security is designed in from the start rather than bolted on after a scare.
For continuous monitoring, threat detection, and incident response tailored to your business, explore CMIT Solutions’ cybersecurity services.
What is a managed intelligence provider (MIP)?
A managed intelligence provider does everything an MSP does, adds security, and takes responsibility for the AI and automation layer a business runs on. In practice, that means setting rules for AI use, protecting the data that flows into AI tools, and keeping it aligned with how the company works.
The term is new, and no licensing board stands behind it, so the label alone tells you little about a provider’s real capability.
What a managed intelligence provider actually does
Managed AI work focuses on adopting these tools productively without creating new risk. A capable MIP usually handles:
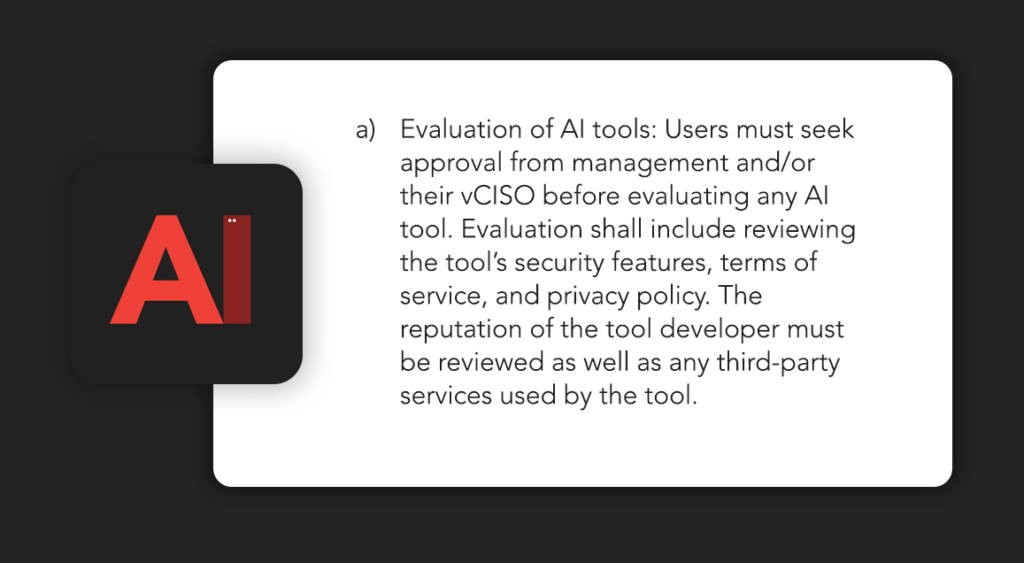
- AI acceptable use policies: Defining which tools are approved, what data staff may enter, and who signs off on new tools. This gives employees clear, safe boundaries.
- AI data governance: Controlling what sensitive information can reach outside AI models, and keeping records of how tools are used. This protects client and company data.
- Shadow AI visibility: Finding unsanctioned AI tools employees adopt on their own, which is where most AI risk starts. Visibility turns a blind spot into something that can be managed.
- Productivity and efficiency support: Helping teams use approved tools for real work, such as drafting, summarizing, and routine automation. The payoff is time saved without cutting corners on security.
Frameworks such as the NIST AI Risk Management Framework give smaller businesses a structured, vendor-neutral way to manage AI risk, and a strong MIP puts that kind of structure into practice.
How to tell a real MIP from a relabeled MSP
Because the term has spread faster than the capability, it helps to ask pointed questions. A genuine MIP should be able to show the following:
- A written AI governance approach: Not a sales pitch, but actual policy templates, approval workflows, and data rules it can tailor to your business.
- Security tied to AI, not separate from it: Evidence that AI oversight connects to the same monitoring and controls protecting the rest of your systems.
- Visibility into AI usage: A way to see which AI tools employees use, including the ones no one approved.
- Practical, SMB-sized guidance: Advice scaled for a business without an AI team or a large budget, not enterprise theory.
This is the role CMIT Solutions is built for, pairing locally delivered support with a nationwide network of specialists, so a small business gets AI guidance it could not staff on its own.
Additional reading: managed intelligence provider
For regulated businesses, AI governance also has to respect existing obligations, such as protecting controlled government data under defense contracting rules.
If your business handles controlled federal information, CMIT Solutions can align your security and AI practices with CMMC compliance services.
Can one provider cover all three roles?
Yes, and that is increasingly the model small businesses prefer. Because IT, security, and AI governance depend on each other, a single provider can run all three, which is essentially the MIP role. Keeping the layers together means one team sees the whole picture, from infrastructure to AI.
Splitting the layers across separate vendors is where problems start. When one company runs your network, another watches for threats, and a third weighs in on AI, issues that sit on the boundary can fall through the cracks.
CMIT Solutions brings these layers under one roof, so a growing business gets one advisor across IT, security, and AI rather than several vendors to coordinate.
Additional reading: MSP to MIP
How to choose the right provider as your business adopts AI
Start with your biggest risk, not the acronym. If your pain is downtime, you need an MSP; if it is threats or compliance, you need MSSP-level security; if your team is already using AI tools, you need a provider that can govern them. Growing businesses usually need all three.
For a business already using AI, the sharper question is no longer MSP vs MSSP but MSP vs MIP: whether to keep IT and AI managed separately, or bring them together under one provider that governs both. For most SMBs adopting AI, that points toward the MIP role.
A few questions make the choice clearer:
- Your current gaps: Is the problem keeping IT running, defending it, managing AI, or all three at once? Name the most urgent one first.
- Your risk and compliance load: Regulated or data-heavy businesses need deeper security than a basic MSP provides. This often points toward MSSP-level or MIP support.
- Your internal team: The less in-house IT and security talent you have, the more value a broader provider adds. Few SMBs can staff AI governance alone.
- Your AI footprint: If employees already use tools like ChatGPT or Copilot without oversight, the question is no longer whether to manage AI, only who does it.
A realistic scenario: a growing firm adopts AI
Consider an illustrative example, a thirty-person accounting firm, not a specific CMIT client. Its MSP keeps the network and laptops running smoothly, so leadership feels covered.
Then staff start pasting client financial details into a free AI tool to speed up reports. The MSP does not watch for this, and the firm has no policy, so sensitive data leaves its control without anyone noticing.
An MSSP might catch some of that data movement, but it would not set the rules for acceptable AI use or train the team. Closing the gap takes the MIP role: an approved tool list, data controls, monitoring, and staff guidance, layered on top of the IT and security already in place.
For a business at this stage, CMIT Solutions can turn scattered AI use into a managed, lower-risk advantage, with security and strategy handled together.
Many businesses assume their cyber insurance will pay out after an incident, but insurers increasingly expect specific security controls to be in place before they issue or renew a policy.
Use CMIT Solutions’ insurance readiness assessment to check whether your security environment meets what insurers now expect.
Put AI to work without inheriting new risk
Recognized on Entrepreneur’s Franchise 500 for more than a decade and named ConnectWise Partner of the Year, CMIT Solutions pairs security-first managed IT, responsive local support backed by a nationwide network, and strategic guidance. Figuring out which model fits, and governing AI safely as you grow, is the kind of decision CMIT Solutions handles every day, so the heavy lifting sits with CMIT, not with you.
CMIT Solutions already delivers this kind of secure, compliant IT for multi-location businesses. The Optyx case study shows how a 13-location optical chain kept every store compliant and connected with always-on support and backup internet, gaining the confidence to expand without IT headaches.
To find out where your business lands and how to adopt AI safely, contact us online or call CMIT Solutions at (800) 399-2648.
Frequently asked questions
How much do MSP, MSSP, and MIP services cost?
Most MSP, MSSP, and MIP services are billed as a predictable monthly fee, usually per user or per device rather than per project. MSP pricing covers core IT support, MSSP pricing reflects the depth of security monitoring, and MIP pricing adds AI governance for using AI tools safely.
Will switching IT providers mean replacing our current security tools?
Not usually. A good provider first reviews the security tools you already have and keeps what works before adding or replacing anything. Expect an early assessment that maps your current tools against any gaps, so you keep the value you have already paid for and avoid a full rebuild.
How long does it take to switch to a new managed IT provider?
Switching usually takes a few weeks, depending on your size and systems. A provider typically begins by auditing your current setup and documenting devices and accounts, then layers in monitoring and controls. Expect a short discovery phase before full coverage is active, with the most urgent gaps handled first.
What reporting should I expect from a managed IT provider?
Expect regular reports, usually monthly, covering system health, security activity, and open issues. An MSP focuses on uptime and support metrics, while an MSSP or MIP adds threat detection, incidents handled, and compliance status. Ask upfront how often a provider reports and who reviews the results with you.
What should be in a managed IT services contract?
A managed IT services contract should list the services covered, response times, and what counts as an emergency. Look for clear pricing, data ownership, security responsibilities, and how either side can end the agreement. For AI support, confirm who sets usage policies and who is accountable if data is mishandled.