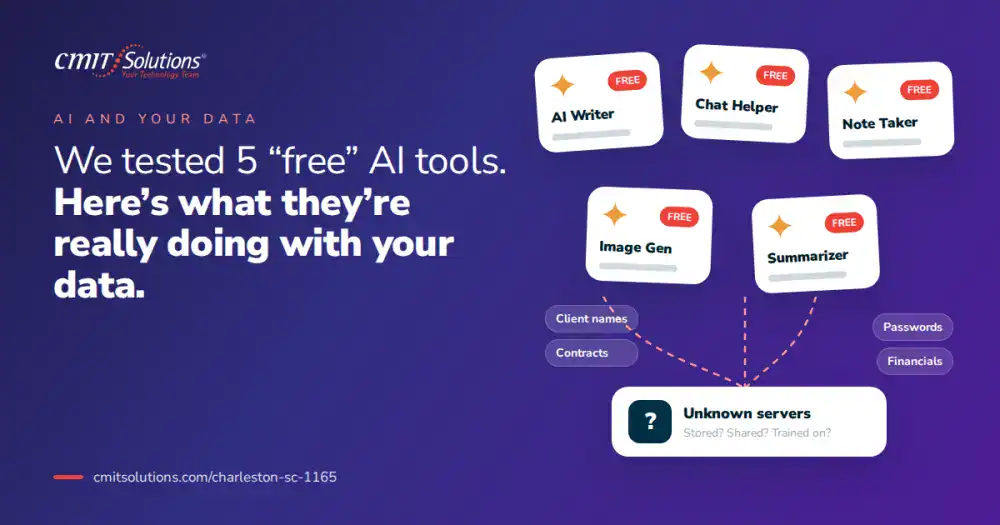
Free artificial intelligence tools are everywhere right now. They show up in browser extension stores, in app marketplaces, in LinkedIn feeds, and increasingly in the daily workflow of employees who never asked IT for permission. A free AI notetaker joins a client call. A free summarizer chews through a contract. A free image generator turns a confidential product roadmap into a slide graphic.
Nobody thinks much about it, because nothing appears to go wrong. There is no error message, no security alert, and no invoice. The work just gets faster.
So our team ran an experiment. We evaluated five categories of widely used free AI tools that we regularly find installed on client devices, read their published terms of service and privacy documentation line by line, watched their network behavior, and mapped what actually happens to business data once it leaves a laptop in Mount Pleasant or West Ashley.
The findings were not dramatic in a Hollywood sense. There were no hooded hackers. What we found instead was quieter and, for a small or mid sized business, considerably more expensive: a slow, permanent, contractually authorized leak of information that companies are legally obligated to protect.
This article walks through what we tested, what we found, and what a business should do about it. If your team is already deep into daily AI use, the practical starting point is a written clear AI policy that defines what is allowed before anyone has to guess.
Why “Free” Is Never Actually Free
Running a large language model is expensive. Inference costs money. Storage costs money. GPUs cost a great deal of money. When a company hands you access at no charge, it is funding that operation some other way.
There are only a handful of realistic business models behind a free AI product:
- Training data acquisition. Your inputs improve the model, which increases the company’s core asset value.
- Freemium conversion. The free tier is a funnel, and your usage patterns become sales intelligence.
- Data brokerage. Usage metadata, behavioral signals, and sometimes content are packaged and sold to third parties.
- Advertising and profiling. Your prompts reveal intent, and intent is the most valuable signal in advertising.
- Acquisition positioning. User volume and accumulated data make the company attractive to a buyer, and your data transfers with the sale.
Only the second of those is genuinely benign for a business user. The other four mean your information is the product. That is not a conspiracy theory. It is written, in plain language, in documents that almost nobody reads.
Understanding this economic reality is the foundation for everything else, and it is why AI data privacy has moved from an abstract compliance topic to an operational one.
How We Tested
We wanted this review to reflect real conditions, not a laboratory. Our approach:
- Selected five tool categories that appear most frequently during client device audits
- Created a sample data set that mimicked realistic business content, including invented client names, fabricated financial figures, mock health information, and a synthetic contract
- Read the complete terms of service, privacy policy, data processing addendum, and acceptable use policy for the free tier of each tool
- Compared the free tier terms against the paid or enterprise tier terms of the same vendor
- Monitored outbound connections, permissions requested, and persistence behavior
- Checked for published security certifications, breach history, and subprocessor disclosure
We deliberately did not test only obscure tools. Several of the products in these categories are well known, well funded, and widely trusted. The problems we found are not a matter of shady operators. They are a matter of how free tiers are designed.
A similar methodology underlies good continuous threat exposure practice, where you assume exposure exists and go looking for it rather than waiting for an alert.
Tool 1: The Free AI Meeting Assistant
This is the category we encounter most often, and the one that worries us most.
What it does: Joins video calls as a participant, records audio, produces a transcript, and generates a summary with action items.
What we found:
The free tier granted the vendor a broad, perpetual, worldwide license to use uploaded content for product improvement. Transcripts were retained by default with no automatic deletion window on the free plan. The paid enterprise tier of the same vendor offered a zero retention option and contractual commitments against training use. The free tier offered neither.
More concerning was the consent structure. The tool joined calls as a bot participant, which meant that every other person on the call was being recorded, often without a clear disclosure beyond a small notification. In a state with all party consent requirements, or in a call involving attorneys, clinicians, or financial advisors, that is a meaningful legal problem rather than a technical one.
What a meeting transcript actually contains:
- Client names, company names, and deal values
- Salary discussions and personnel decisions
- Unreleased product plans and pricing strategy
- Legal exposure discussed candidly before counsel refines it
- Medical details in any healthcare adjacent conversation
- Credentials, occasionally, when someone reads a login aloud
A year of transcripts is arguably the single most sensitive asset a company owns, and it was sitting on infrastructure governed by a consumer agreement that nobody at the company had reviewed.
Firms handling privileged conversations should look closely at law firm confidentiality obligations before allowing any recording bot into a client call.
Tool 2: The Free Browser Writing Extension
What it does: Adds AI drafting, rewriting, and tone adjustment directly inside the browser, working across email, CRM, ticketing systems, and internal web applications.
What we found:
The permission request was the headline. To function, the extension requested the ability to read and change all data on all websites. That is not unusual for this category, and it is not necessarily malicious, but it is functionally unlimited access to everything the user sees in a browser.
That includes:
- Full email content in a webmail client
- Records displayed inside the CRM
- Patient or client portals
- Banking and payroll interfaces
- Any internal application accessed through the browser
The privacy policy distinguished between “content you submit” and “content the extension processes,” and the retention terms applied cleanly only to the first category. The second was governed by language broad enough to permit substantial collection.
We also found that the extension updated automatically. The version reviewed on day one was not the version running on day thirty. Permissions granted once persist across updates, and the code behind those permissions can change without a new consent prompt. Extensions have historically been an acquisition target precisely because an installed base with broad permissions is valuable to whoever buys it.
This is exactly the blind spot that makes endpoint security essentials a moving target rather than a one time project.
Tool 3: The Free Document Summarizer
What it does: Accepts uploaded PDFs, Word files, and spreadsheets, then produces summaries, extracts key terms, and answers questions about the content.
What we found:
This tool retained full uploaded documents, not just derived text, and the free tier had no configurable retention period. Deleting a document from the interface removed it from the user view. The terms indicated that backup copies could persist afterward for an unspecified period.
The subprocessor list was the more interesting finding. Like most modern applications, the vendor relied on third parties for storage, model inference, analytics, and support ticketing. Uploading a document to one company meant distributing it across four or five, each with its own security posture and its own jurisdiction.
For a business, the categories of document most often fed into free summarizers are precisely the ones that carry regulatory weight:
- Signed contracts with confidentiality clauses
- Financial statements and tax documents
- Employee records and benefits enrollment forms
- Patient intake paperwork and insurance correspondence
- Vendor agreements containing pricing that is contractually secret
Uploading a contract that contains a confidentiality clause to a service that claims a license to use the content is, in a literal sense, a breach of that contract. The client whose information appears in the document never agreed to it.
Organizations subject to financial regulation should read GLBA financial requirements alongside their AI decisions, because the safeguards rule does not pause for a free tool.
Tool 4: The Free AI Image and Design Generator
What it does: Creates images from text prompts, edits uploaded photos, removes backgrounds, upscales resolution, and produces marketing graphics.
What we found:
This category surprised our team. On the surface, image generation feels low risk. The findings said otherwise.
First, uploaded images carry metadata. Photos taken on a phone often contain GPS coordinates, device identifiers, and timestamps. A staff member uploading a jobsite photo to remove a background may also be uploading the precise location and the time it was captured.
Second, the commercial use terms on the free tier were restricted. Output could be used for personal purposes, with commercial use reserved for paid plans. A marketing team generating brand assets on a free account was creating material the company did not clearly have the right to use, which becomes a problem the moment a campaign scales or a competitor notices.
Third, the ownership language was ambiguous. Some free tiers grant the user rights to the output. Others grant a license while retaining ownership. Others make no clear commitment at all. Building visual identity on that foundation is a risk that surfaces later, usually at the worst time.
Fourth, uploaded images frequently contain text. Screenshots of dashboards, whiteboard photos from planning sessions, and scanned documents all pass through image tools, and modern systems read text in images perfectly well.
Teams standardizing on approved creative and collaboration software will get better outcomes from supported productivity application support than from a patchwork of consumer accounts.
Tool 5: The Free AI Code and Spreadsheet Assistant
What it does: Suggests formulas, writes scripts, debugs code, and automates repetitive data work inside spreadsheets and development environments.
What we found:
Context is the issue. To be useful, this class of tool needs surrounding content. A formula suggestion requires seeing the data. A debugging suggestion requires seeing the code and, frequently, the configuration around it.
In practice that meant transmitting:
- Customer records sitting in adjacent spreadsheet columns
- Revenue figures, margins, and forecast models
- Database connection strings and internal endpoint addresses
- API keys pasted into configuration files
- Business logic that constitutes genuine intellectual property
The free tier terms permitted use of submitted content for model improvement, with an opt out available but disabled by default. Almost no user we observed had changed that setting, because almost no user knew it existed.
Credentials deserve special attention. A pasted API key is not merely exposed to the vendor. It may be retained, indexed, and in some architectures surfaced in response to another user’s query. Secret material should never enter a third party system, free or paid.
Businesses that depend on data analysis at scale benefit far more from governed platforms supported by strategic IT guidance than from ad hoc consumer tooling.
The Pattern Across All Five
Five different categories, five different vendors, one consistent structure.
Finding one: the free tier and the paid tier are governed by different contracts. In every case, the enterprise agreement offered protections the free agreement did not, including training exclusions, retention controls, deletion guarantees, and breach notification commitments. The model is identical. The legal protection is not.
Finding two: defaults favor collection. Where an opt out existed, it was off. Where retention was configurable, the default was indefinite. Where sharing was optional, it was enabled.
Finding three: nobody reads the terms. Combined, the documents for these five tools exceeded forty thousand words, written at a reading level that assumes legal training. Expecting an employee to parse that before summarizing a PDF is unrealistic.
Finding four: the tools are invisible to IT. Browser extensions, personal accounts, and mobile apps do not appear in a software inventory. Without monitoring, leadership has no idea which tools are in use.
Finding five: the risk compounds silently. One document is a small exposure. Eighteen months of daily use across a twenty person team is a comprehensive external copy of the business.
This is the phenomenon behind shadow AI risks, and it is now one of the most common gaps we identify during assessments.
The Compliance Consequences Nobody Budgets For
Data protection regulation does not distinguish between paid and free software. It asks a simpler question: did you exercise reasonable control over regulated information?
Healthcare organizations. Protected health information transmitted to a vendor without a business associate agreement is a disclosure. Free tiers do not offer business associate agreements. A meeting transcript mentioning a patient by name is sufficient. The relevant obligations are outlined in HIPAA compliance clarity.
Financial services and accounting. Customer financial information carries safeguard duties that extend to every service provider touching that data. Firms should review finance shadow AI exposure before the next examination cycle.
Businesses accepting card payments. Cardholder data has strict handling rules, and scope expands to any system that stores, processes, or transmits it. The practical requirements appear in the PCI DSS checklist.
Companies with California customers. Consumer rights include deletion and disclosure of sharing. You cannot honor a deletion request for data sitting in a vendor’s training set. Start with CCPA requirements explained and the related CPRA obligations overview.
Companies with European customers or staff. Cross border transfer rules, lawful basis requirements, and processor agreements all apply. The practical view is covered in the GDPR compliance guide.
Anyone carrying cyber insurance. Carriers increasingly ask specific questions about AI governance during renewal. An inaccurate answer can jeopardize a claim long after the fact.
The broader case for treating this seriously is made in cybersecurity compliance basics, and structured programs are what IT compliance services exist to support.
The Security Angle: Free Tools Widen the Attack Surface
Beyond privacy and compliance, free AI tools create direct security exposure.
Account security is weak by default. Free tiers frequently lack enforced multifactor authentication, single sign on integration, and administrative visibility. Employees use personal email addresses and reused passwords. When the employee leaves, the account and its data history leave with them.
Vendor breach becomes your breach. AI startups are attractive targets because they concentrate valuable data. A breach at a vendor holding your transcripts is a breach of your client confidentiality, and your clients will not accept the distinction.
Prompt injection is a live technique. Attackers embed instructions inside documents and web pages that AI tools then execute. A summarizer processing a hostile PDF can be manipulated into surfacing or exfiltrating other content it has access to.
Impersonation gets easier. Transcripts and email archives give an attacker perfect voice, vocabulary, and context, which is why AI phishing attacks now succeed against experienced staff.
Automated adversaries are scaling. The rise of agentic AI attacks means reconnaissance that once took a skilled human weeks now runs continuously and cheaply.
Detection matters as much as prevention here, which is where managed detection response and full cybersecurity services Charleston businesses rely on earn their place in a budget.
What We Are Not Saying
This is not an argument against AI adoption. Refusing these tools outright is a losing strategy, and it does not work anyway. Employees adopt them regardless, just without oversight, which produces the worst possible outcome: all of the risk and none of the visibility.
The goal is governed adoption. Businesses that do this well tend to move faster than competitors, not slower, because their teams can use powerful tools confidently instead of secretly. That is the practical argument in small business AI adoption and in the broader shift toward AI workforce augmentation.
A Practical Framework for Safe AI Use
Here is the approach we recommend to clients, structured so that a business of any size can execute it.
Step 1: Discover what is actually in use
You cannot govern what you cannot see. Inventory should cover:
- Browser extensions installed across all managed devices
- Applications on company and personally owned devices used for work
- Meeting platform integrations and connected third party bots
- Cloud application marketplace connections granted by users
- Software as a service subscriptions charged to expense reports
Expect surprises. In a typical assessment we find four to seven times more AI tools than leadership estimated, a pattern explored in unmonitored AI usage.
Step 2: Classify your data before you classify your tools
Sort information into tiers:
- Public. Marketing copy, published materials, general information.
- Internal. Process documents, non sensitive operational data.
- Confidential. Client lists, pricing, contracts, strategy.
- Regulated. Health, financial, payment card, and personal data.
Public and internal data can move through a wider range of tools. Confidential and regulated data belongs only in systems under contract.
Step 3: Select a small approved stack
Fewer tools, better governed, beats many tools loosely managed. Look for:
- Written commitments against training on your content
- Configurable retention with real deletion
- Single sign on and enforced multifactor authentication
- Administrative visibility and audit logging
- Published security certification and subprocessor disclosure
- A data processing agreement, and a business associate agreement where applicable
Most businesses already own capable AI features inside licensing they pay for. Deploying those properly through managed IT services provider support removes most of the motivation to reach for free alternatives.
Step 4: Write the policy in language people will follow
A usable policy fits on two pages and answers four questions: which tools are approved, what data may go into them, what is never permitted, and who to ask. Guidance on structuring this appears in AI governance basics.
Step 5: Enforce technically, not just on paper
Policy without controls is a suggestion. Practical enforcement includes:
- Extension allow lists managed through device policy
- Conditional access rules tied to identity
- Data loss prevention on outbound sensitive content
- Meeting platform settings restricting third party bots
- Blocking unapproved services at the network layer
This is standard work under network management solutions and disciplined responsive IT support team operations.
Step 6: Train for judgment, not memorization
Staff need a mental model, not a list. The simplest version: if you would hesitate to post it publicly, it does not belong in an unapproved tool. Reinforce with real examples, including seasonal scam awareness refreshers during high risk periods.
Step 7: Review on a schedule
Vendor terms change. Tools get acquired. New products appear monthly. Quarterly review is the minimum, and it should sit alongside your review of emerging digital threats.
Choosing Where AI Actually Belongs
Once governance exists, the useful question becomes where AI creates real value. Good candidates share traits: repetitive, rule based, high volume, low judgment, and easy to verify. Poor candidates involve regulated data, final decisions, or outputs nobody will check.
A structured evaluation approach is described in AI automation readiness, and the difference between marketing claims and measurable results is covered in practical AI integration.
At CMIT Solutions of Charleston, the pattern we see repeatedly is that companies who govern first and adopt second end up adopting more, not less, because the friction of uncertainty disappears.
Supporting Infrastructure Matters More Than the Tool
AI adoption stresses the systems underneath it. Before scaling usage, confirm that the fundamentals hold:
- Identity. Centralized accounts, enforced multifactor authentication, and clean offboarding.
- Data. Tested restoration through proper data backup and recovery rather than assumed file sync, an issue detailed in managed backup protection.
- Storage. Properly permissioned secure cloud services so sensitive files are not scattered across personal drives.
- Communication. Governed unified communications tools that control which integrations can join a meeting.
- Hardware. Devices capable of running modern security agents, sourced through planned hardware procurement help.
- Budget. Predictable flexible IT packages so security spending does not become a surprise.
Generative tools introduce additional considerations worth reviewing in generative AI security risk, and the wider operational shift is covered in AI reshaping business IT.
What This Costs If You Ignore It
The expense of governance is modest and predictable. The expense of ignoring it is neither:
- Regulatory penalties scaled to records affected
- Notification and credit monitoring obligations
- Legal defense and potential settlement
- Contract termination when clients learn their data was exposed
- Insurance premium increases or denied coverage
- Reputational damage in a market where referrals drive growth
Charleston is a relationship driven business community. Word moves quickly, and trust rebuilds slowly. Rising customer expectations around handling personal information are covered in customer privacy expectations.
Conclusion
The tools we tested were not scams. They worked, they were useful, and in several cases they were genuinely impressive. That is precisely the problem. Useful tools spread quickly, and free ones spread fastest of all, because there is no procurement conversation to slow them down and no invoice to trigger a review.
What the testing made clear is that “free” describes the price, not the terms. The exchange is real, it is documented, and it is happening every day inside businesses that have no idea it started.
The correct response is not fear and it is not prohibition. It is governance: know what is in use, know what data matters, choose a small set of tools with terms you can live with, write down the rules, enforce them technically, and revisit the decision every quarter. Companies that do this get the productivity gains without quietly handing over their most valuable asset.
If you are not certain what AI tools are currently running on your team’s devices, or what those tools are permitted to do with your information, that uncertainty is the thing worth resolving first. Our team works with organizations across the Lowcountry as their Charleston IT partner to bring visibility, structure, and control to exactly this problem.
Ready to find out what your business is really sharing? Schedule a consultation with CMIT Solutions of Charleston and get a clear picture of your AI exposure, your compliance position, and the practical steps to close the gap.
Frequently Asked Questions